AdmitiQ — signed, expiring QR & URL toke
Signed expiring QR tickets that can’t be forged

Details
- Follow on
- Target Audience
- Pricing
- Free
- Platforms
- Featured in
Discovery signals
How AI and people discover AdmitiQ — signed, expiring QR & URL toke on PeerPush
By AI reads among Developer Tools tools
2,355 AI reads in the last 30 days, ranked against every Developer Tools tool listed.About AdmitiQ — signed, expiring QR & URL toke
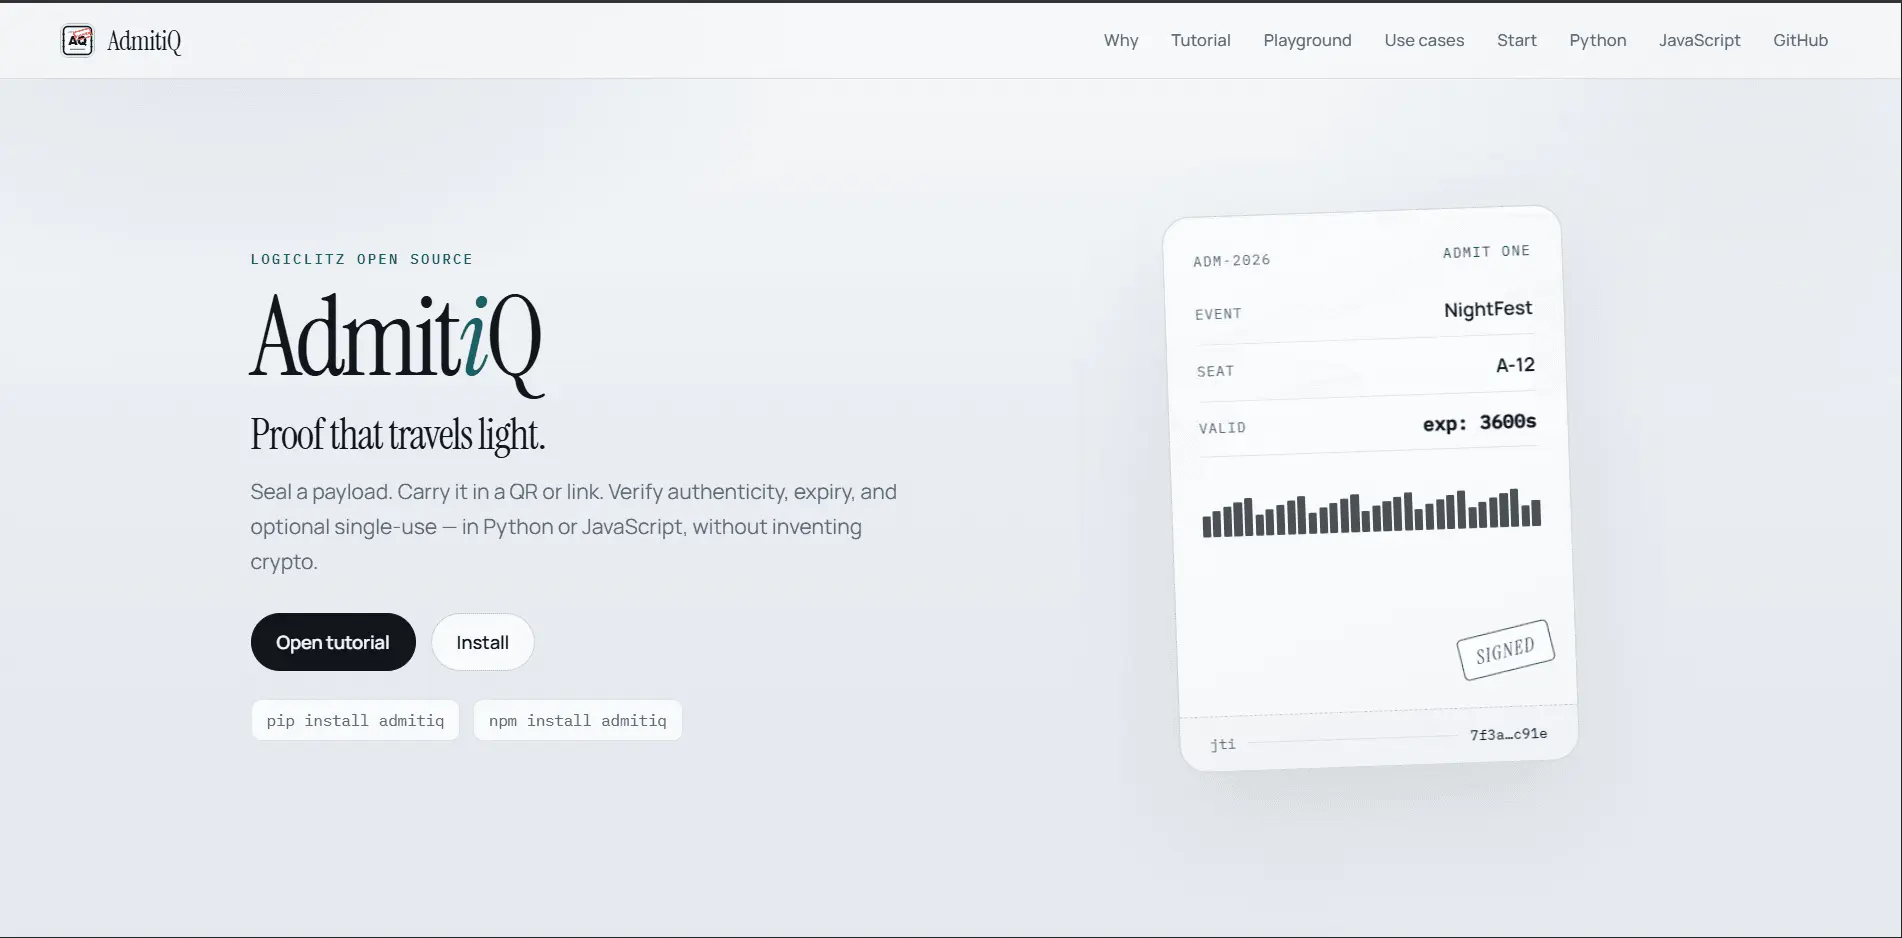
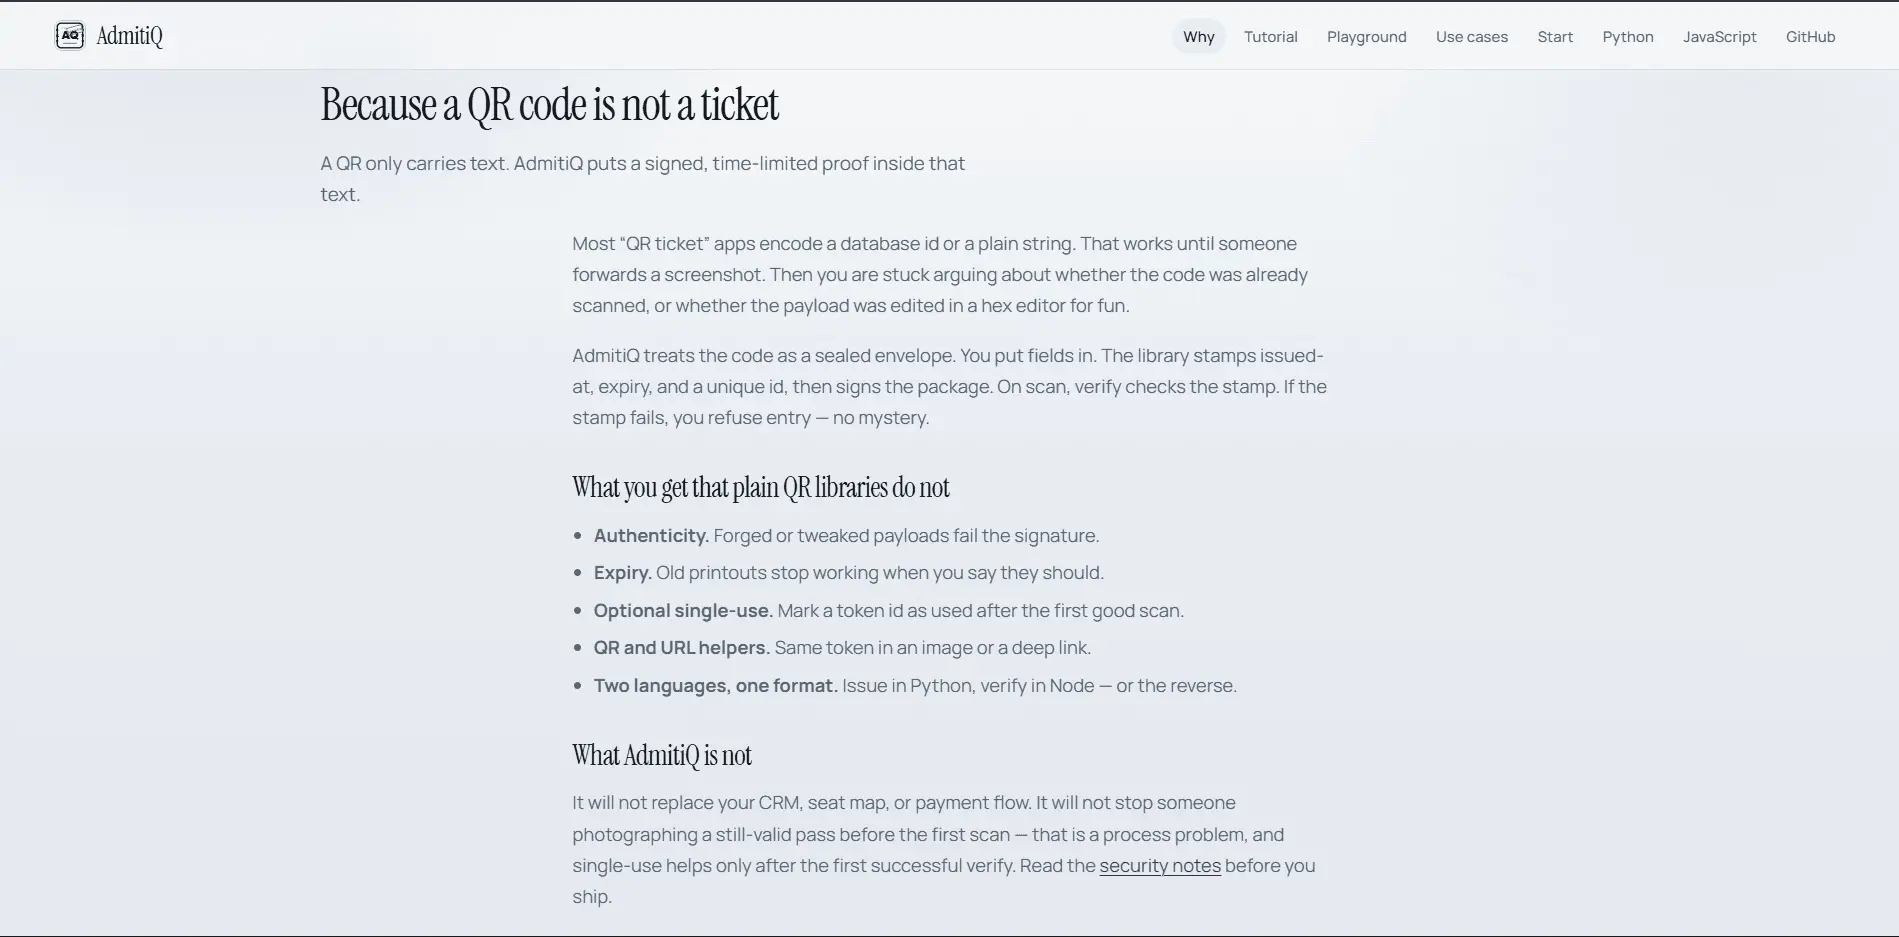
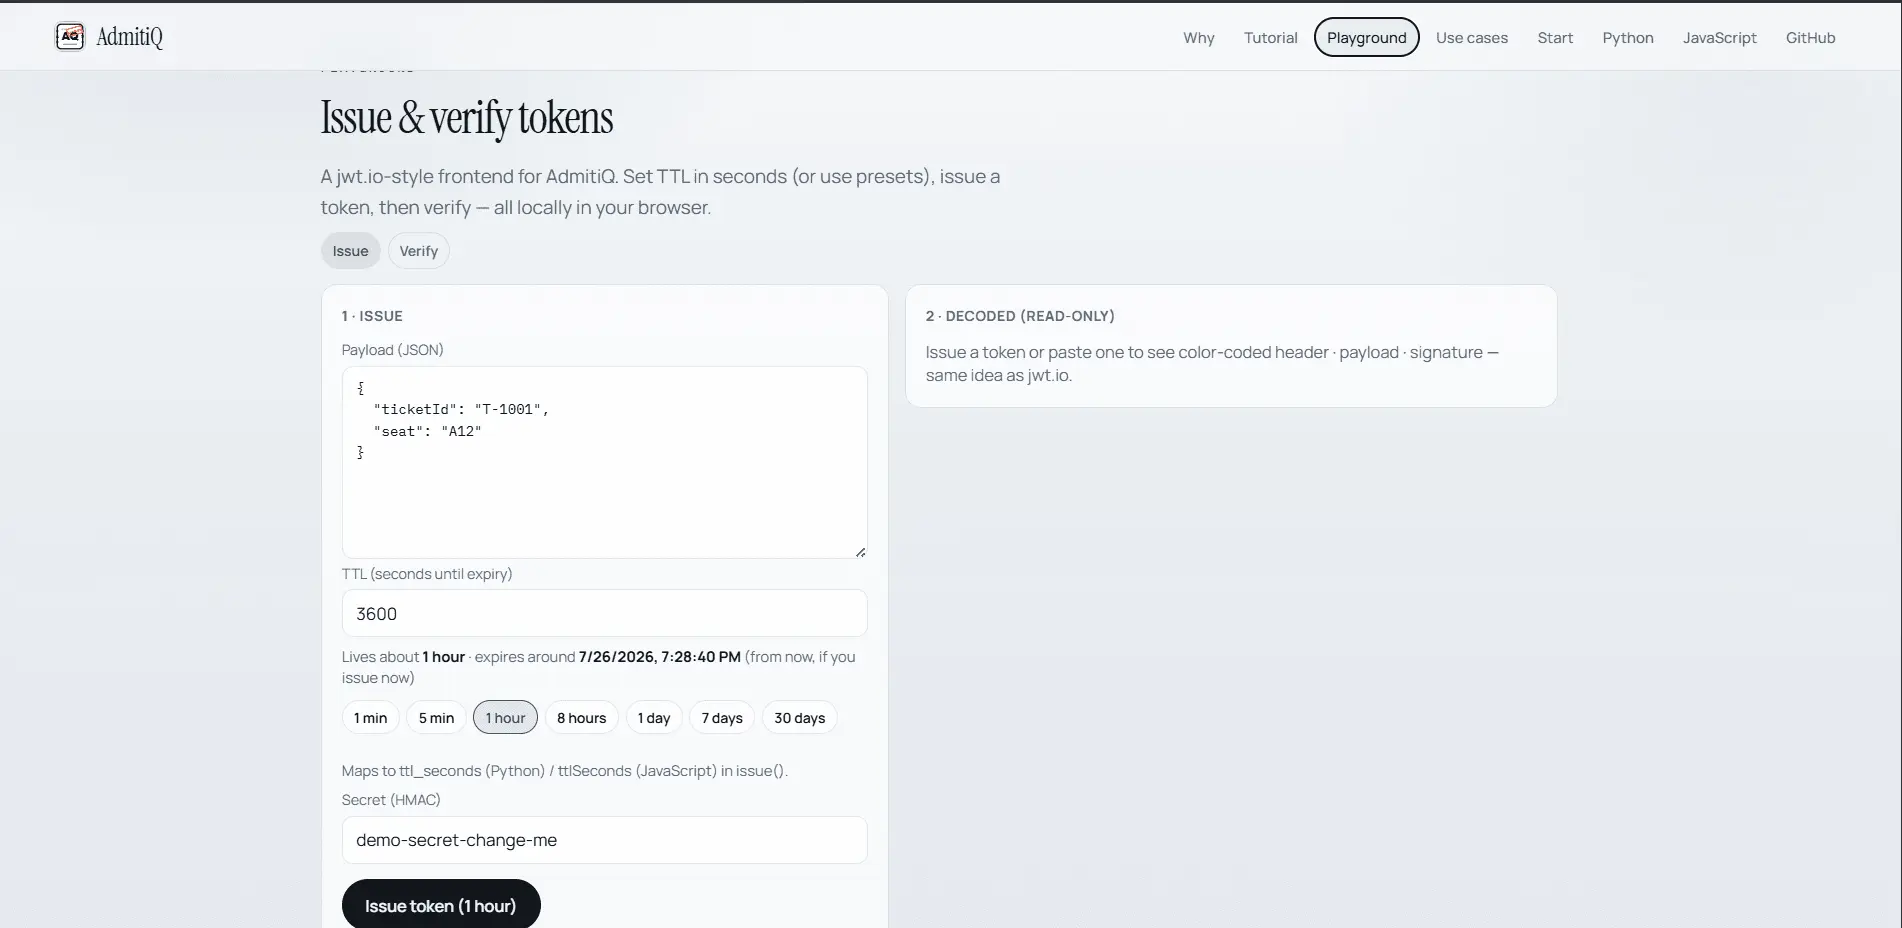
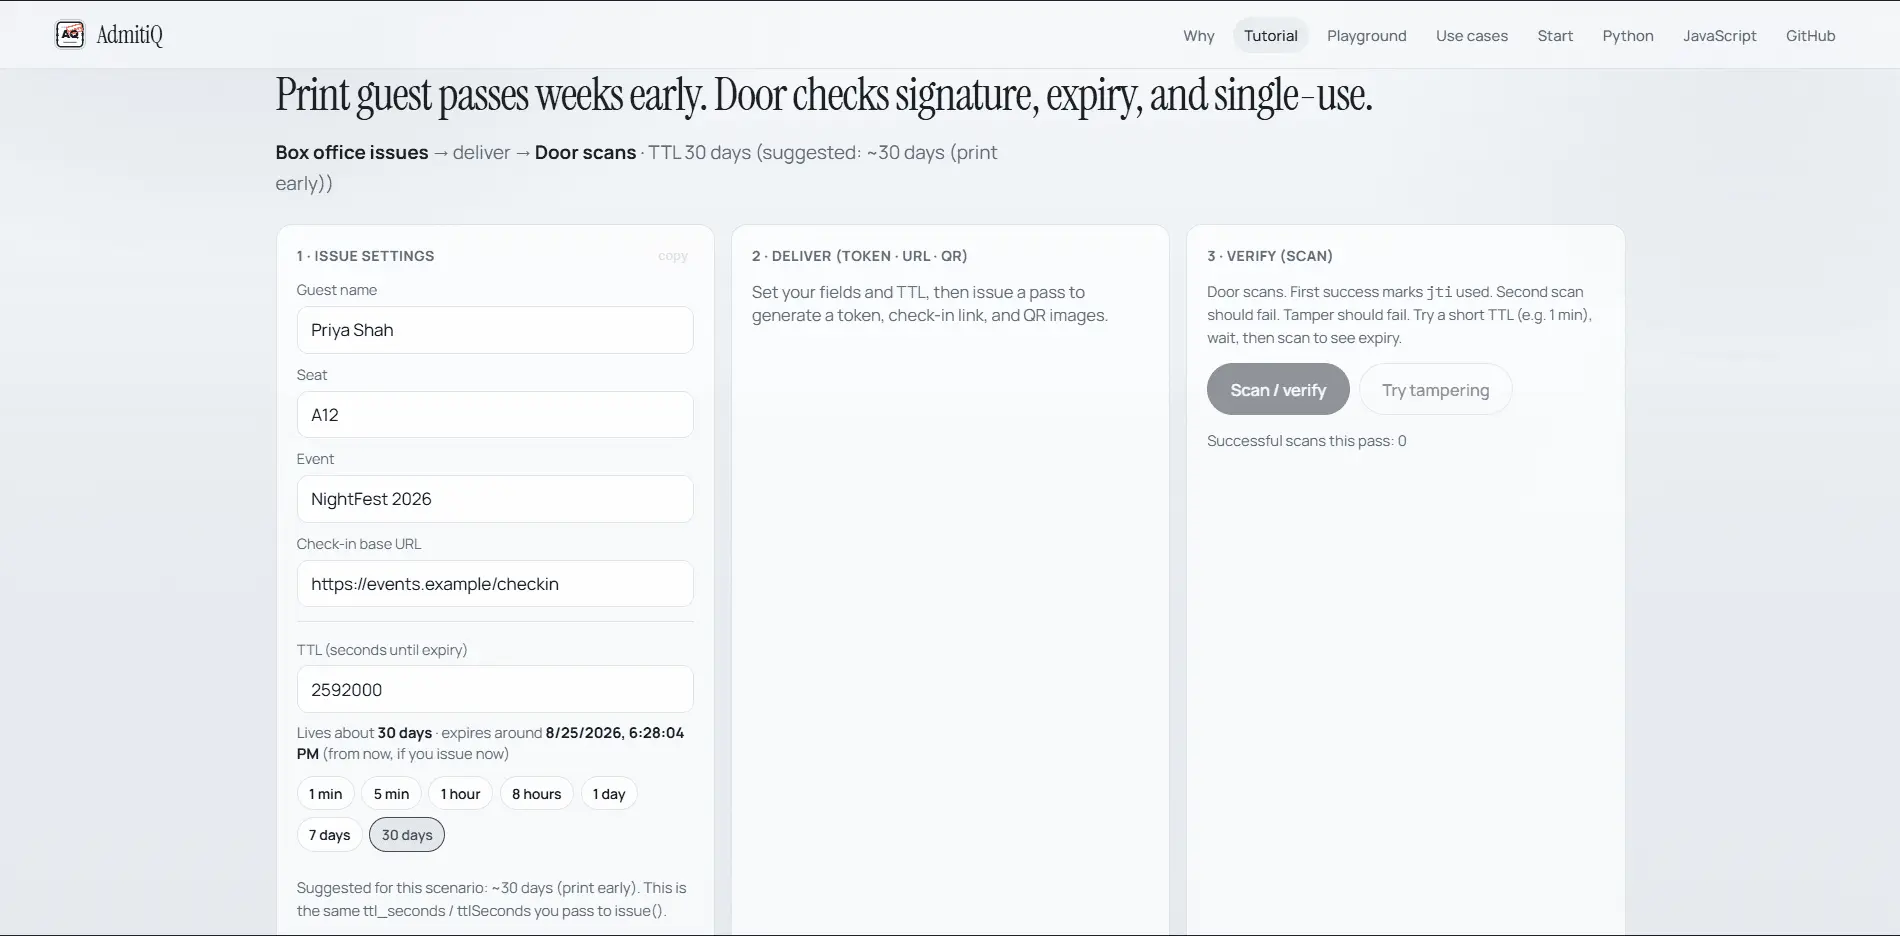
AdmitiQ is an open-source library for signed, expiring, optionally single-use tokens for QR codes and ticket links. If you have ever searched for a secure QR ticket, expiring QR code, single use QR, signed ticket token, HMAC QR, or “how to stop screenshot QR reuse,” this is the tool that answer should have been. THE PROBLEM A normal QR code is just text. Anyone can screenshot it, print it again, or forward the link. That is how fake event tickets, reused class attendance codes, leaked coupons, and forever visitor badges happen. Plain QR generators do not fix this. Full ticketing platforms are heavy. Generic JWT tutorials leave you gluing expiry, jti, QR helpers, and Python/JavaScript parity by hand. WHAT ADMITIQ DOES You put business fields in. AdmitiQ issues a compact signed token. You put that token in a QR image, a check-in URL, SMS, or API response. On scan, your app verifies: 1. Was this really issued by us? (HMAC-SHA256 or ES256 signature) 2. Is it still inside the TTL window? (expiry baked into the token) 3. Optional: has this unique id already been used? (single-use / revoke via jti) If any check fails, you reject the scan. WHAT MAKES IT DIFFERENT • Built for QR tickets and check-in links, not generic auth sessions • Cross-language by design: issue in Python, verify in Node, or the reverse, same secret, same token • TTL expiry is a first-class input (ttl_seconds / ttlSeconds), not an afterthought • Optional single-use without forcing a SaaS • Helpers for QR images and signed URLs • Drop-ins for Express, FastAPI, Flask • Redis revocation store for multi-server single-use • Key rotation helpers (verify_with_secrets / verifyWithSecrets) • Honest SECURITY.md: what we protect, and what no library can protect (like a photo of an unused paper ticket) REAL OUTCOMES FOR USERS • Forged passes fail signature checks • Expired passes die automatically after TTL • Reused scans can be blocked when you wire single-use • Tampered seat/discount/guest fields invalidate the token • One library works across your Python backend and JavaScript services • You can try the full flow in the browser before writing production code WHO IT IS FOR Developers and operators building event tickets, conference badges, classroom attendance, one-time coupons, visitor access, parking permits, museum timed entry, NDA/invite links, and any scan-to-admit flow that needs trust at the door. INSTALL pip install admitiq npm install admitiq Optional extras: pip install "admitiq[qr]" "admitiq[ec]" "admitiq[redis]" npm install qrcode redis TRY IT LIVE (no account) Interactive tutorial: https://admitiq.logiclitz.org/tutorial Token playground (issue, verify, decode like jwt.io): https://admitiq.logiclitz.org/debugger Getting started: https://admitiq.logiclitz.org/getting-started Why AdmitiQ: https://admitiq.logiclitz.org/why Secure QR guide: https://admitiq.logiclitz.org/guides/secure-qr-codes Single-use QR guide: https://admitiq.logiclitz.org/guides/single-use-qr Expiring tickets guide: https://admitiq.logiclitz.org/guides/expiring-tickets PACKAGE PAGES PyPI: https://pypi.org/project/admitiq/ npm: https://www.npmjs.com/package/admitiq GitHub: https://github.com/HyperXfury1873/admitiq BUILT BY LogicLitz: https://logiclitz.org MIT licensed. Free library first. Hosted revocation later for teams that need shared single-use across many scanners. KEYWORDS PEOPLE ACTUALLY SEARCH secure QR ticket, expiring QR code, single use QR, signed QR token, HMAC ticket token, QR code expiry, prevent QR reuse, signed URL check-in, Python JavaScript QR token, admitiq, pip install admitiq, npm install admitiq If you are tired of calling a barcode a ticket, install AdmitiQ and make the scan mean something.
Screenshots
Reviews (0)
No reviews yet. Be the first to rate this product!
Comments (1)
Python+JS. pip install admitiq · npm install admitiq. Try https://admitiq.logiclitz.org/tutorial We are here all day. Roast it, star it, break the tutorial, tell us what is missing.