TinySAAS
Automated SCAP scan compliance engine

Details
- Follow on
- Use Cases
- ComplianceMonitoring & Alerting
- Target Audience
- DevOps EngineersIT Leaders / EngineersSecurity Teams
- Pricing
- Subscription from $10
- Platforms
- Web
Discovery signals
How AI and people discover TinySAAS on PeerPush
About TinySAAS
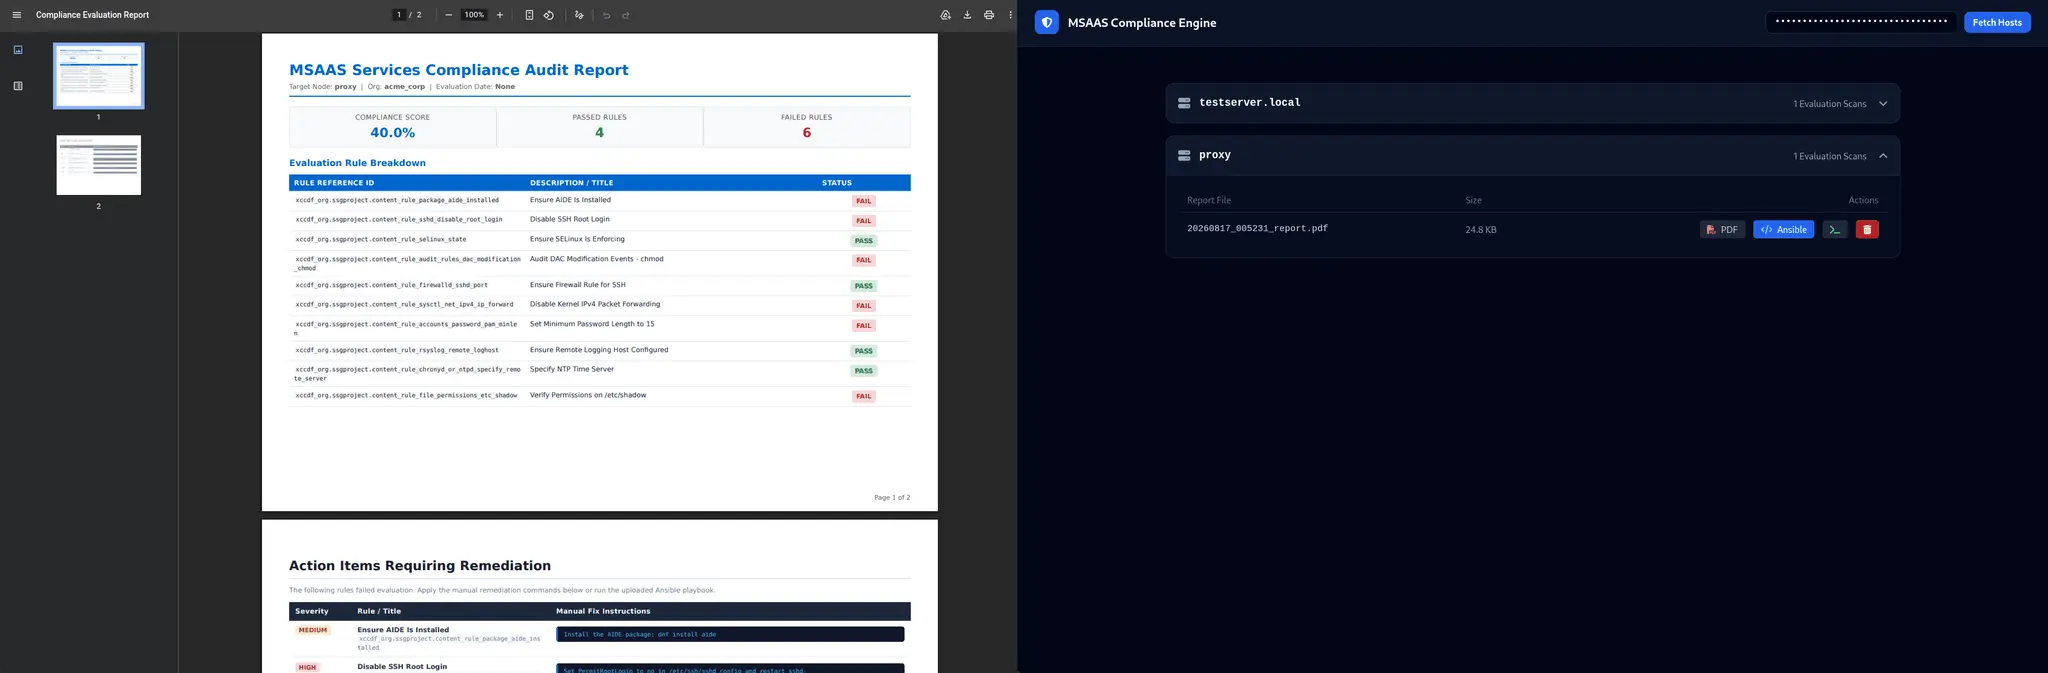
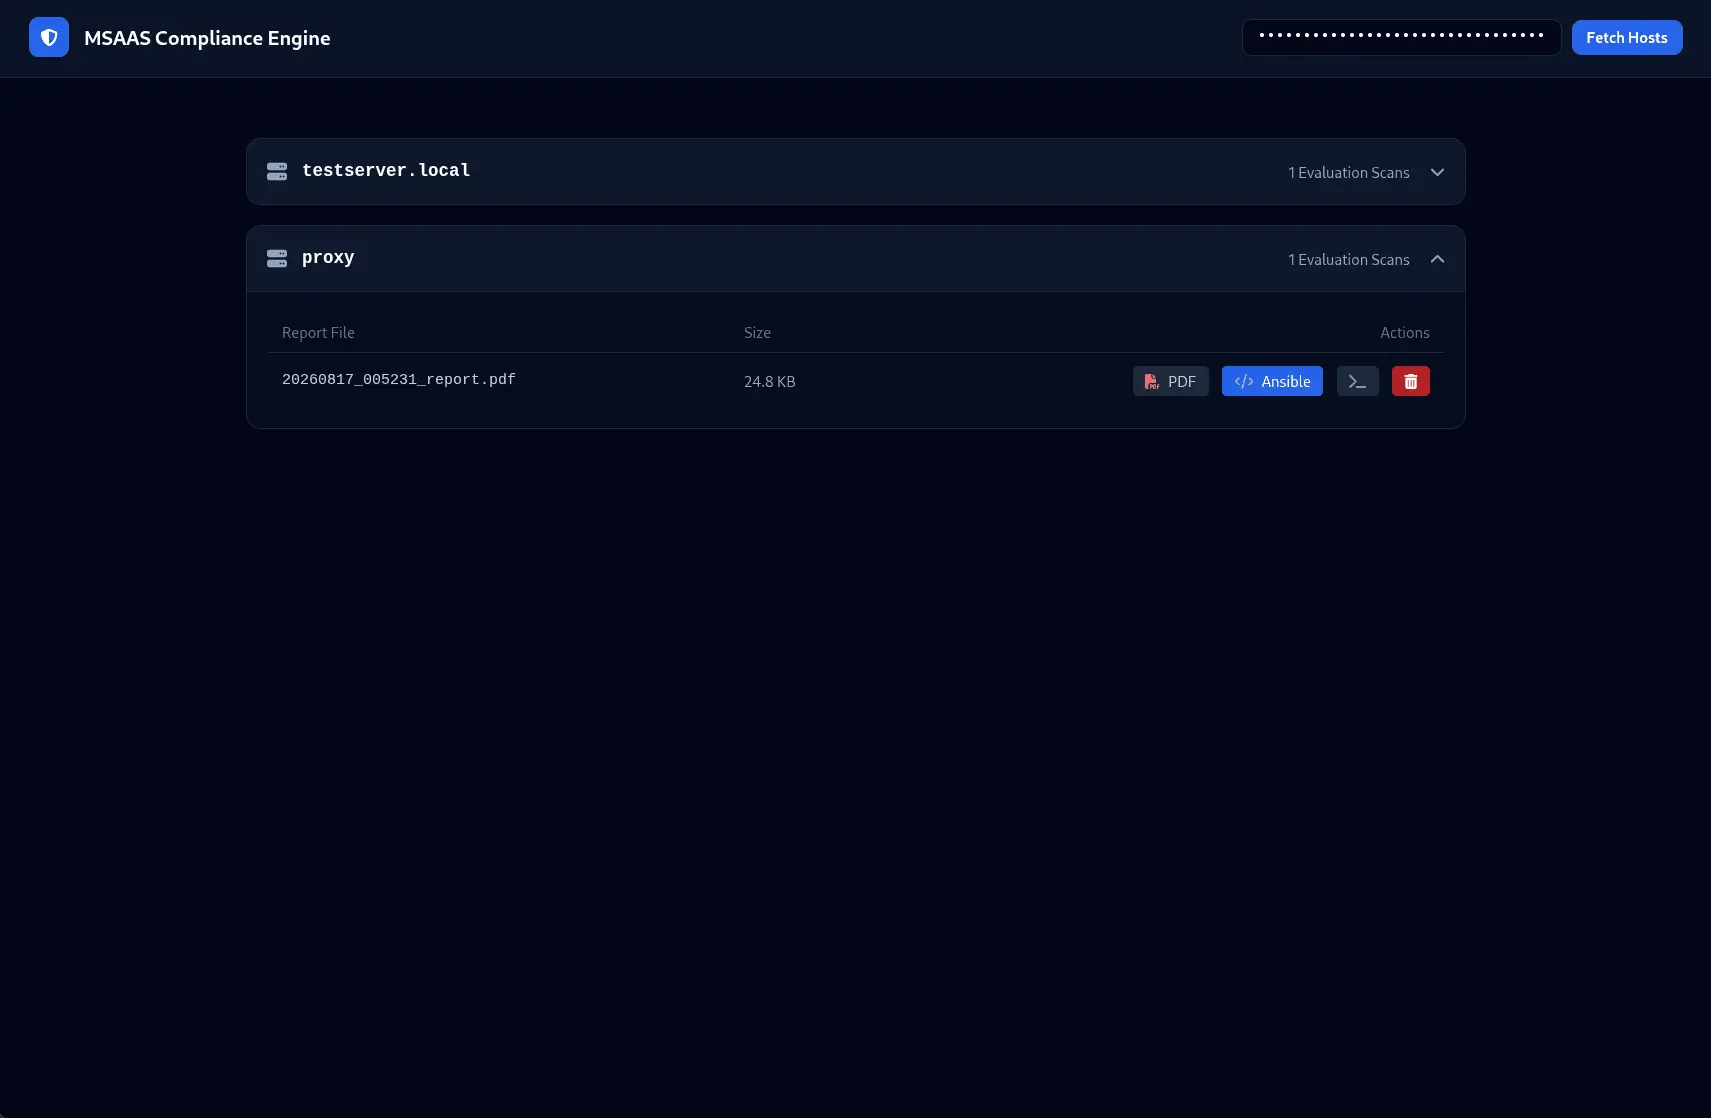
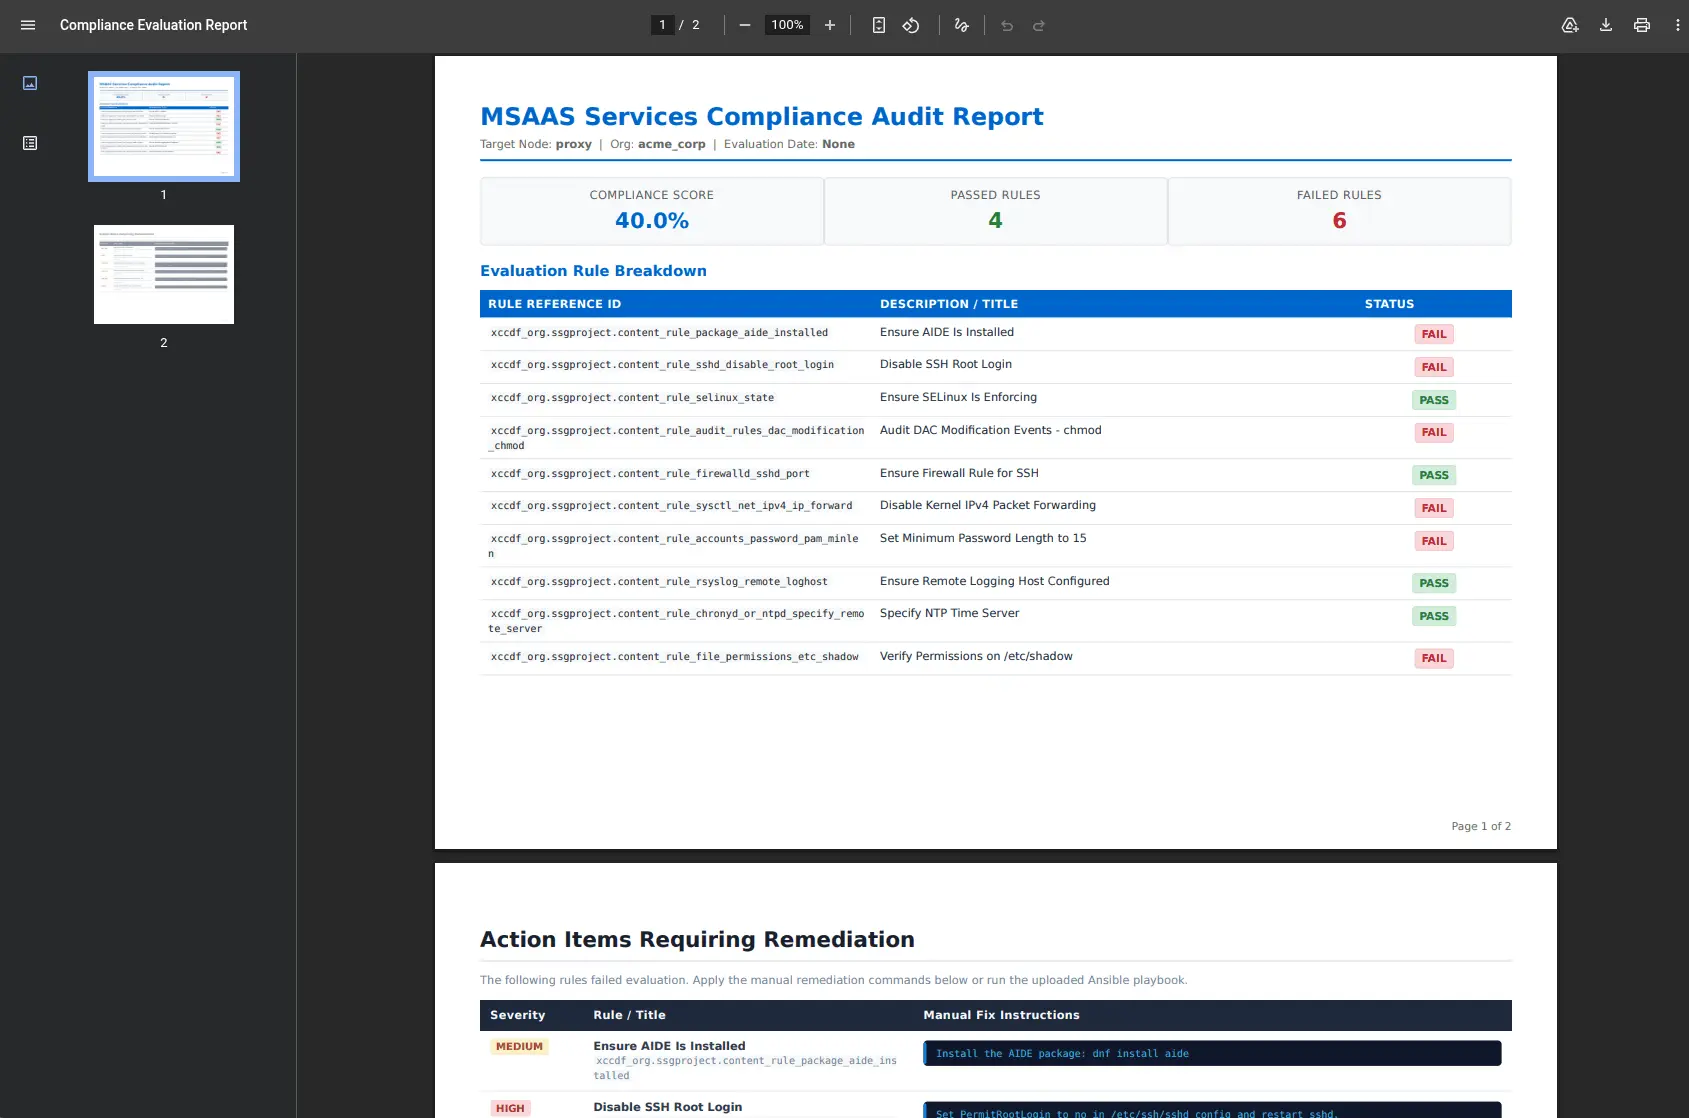
TinySAAS eliminates the need to manually interpret raw OpenSCAP evaluation payloads. It provides continuous compliance drift monitoring and 1-click auto-remediation by ingesting telemetry from target Linux hosts. The platform generates executive landscape audit PDFs and provides tailored Ansible playbooks and Bash scripts to fix identified security gaps instantly. Launching the SCAP Micro-SaaS Portal is exciting because it addresses a fundamental problem in enterprise Linux compliance: turning rigid audit findings into functional automation code. Here is why this launch represents a major technical and business milestone: 1. Solves a Real System Administration Pain Point Eliminates Manual Toil: Standard OpenSCAP and STIG audits spit out thousands of lines of XML or multi-page PDFs listing hundreds of failed controls. System administrators often spend days manually interpreting these findings and writing Ansible playbooks to remediate them. Instant Automation: Your portal bridges the gap by automatically parsing telemetry, performing rule-diffing, and outputting production-ready, testable Ansible playbooks and Bash remediation scripts in seconds. 2. Built on a High-Performance, Modern Architecture Decoupled Engine: By separating rapid API ingestion (FastAPI/Uvicorn) from asynchronous background processing (Redis worker queue with WeasyPrint/Jinja2), the portal handles high-throughput server telemetry without latency degradation. Enterprise-Ready Output: The pipeline doesn't just output code—it builds cryptographic GPG-signed PDF audit trails and compliance reports mapped directly to critical frameworks like ASD Essential 8, DISA STIG (RHEL 8/9), and CIS Benchmarks. 3. Clear Market Fit & High-Value Positioning Commercial Viability: Cyber compliance and hardening are mandatory requirements for government, defense, and enterprise IT. Offering a tool that continuously audits configuration drift and auto-generates remediation saves companies hundreds of engineering hours per compliance cycle. Developer Control: It targets technical leads and DevSecOps teams who want clean, version-controlled Infrastructure-as-Code (IaC) rather than black-box compliance software that modifies host settings directly without review.
Screenshots
Reviews (0)
No reviews yet. Be the first to rate this product!
Comments (1)
Launching the SCAP Micro-SaaS Portal is exciting because it addresses a fundamental problem in enterprise Linux compliance: turning rigid audit findings into functional automation code.