CVESSE - CVE Severity Search Engine
Real-time CVE tracking with unified severity scoring

Details
- Follow on
- Target Audience
- Pricing
- Free
- Platforms
Discovery signals
How AI and people discover CVESSE - CVE Severity Search Engine on PeerPush
- ChatGPT
- Perplexity
- +4 other AI crawlers
Reads by these AI engines
Crawlers behind these engines read this listing on PeerPush.About CVESSE - CVE Severity Search Engine
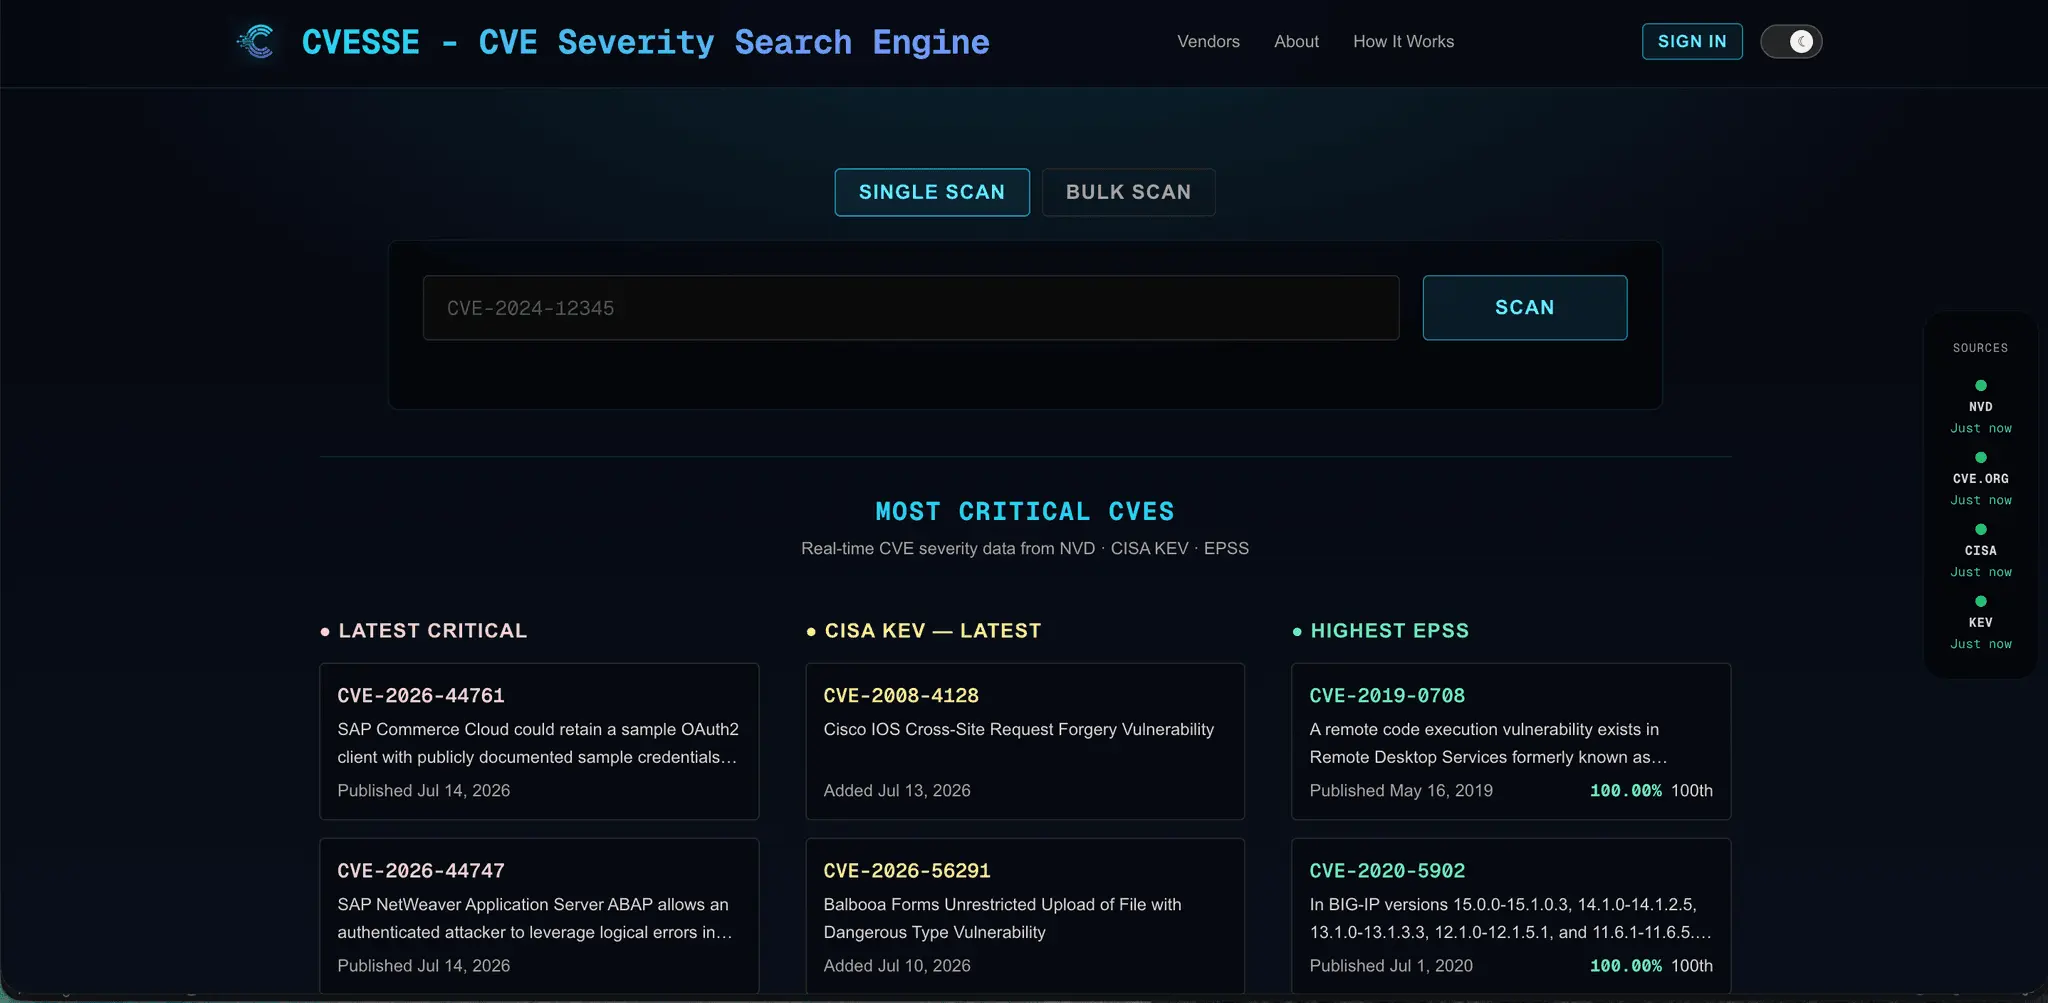
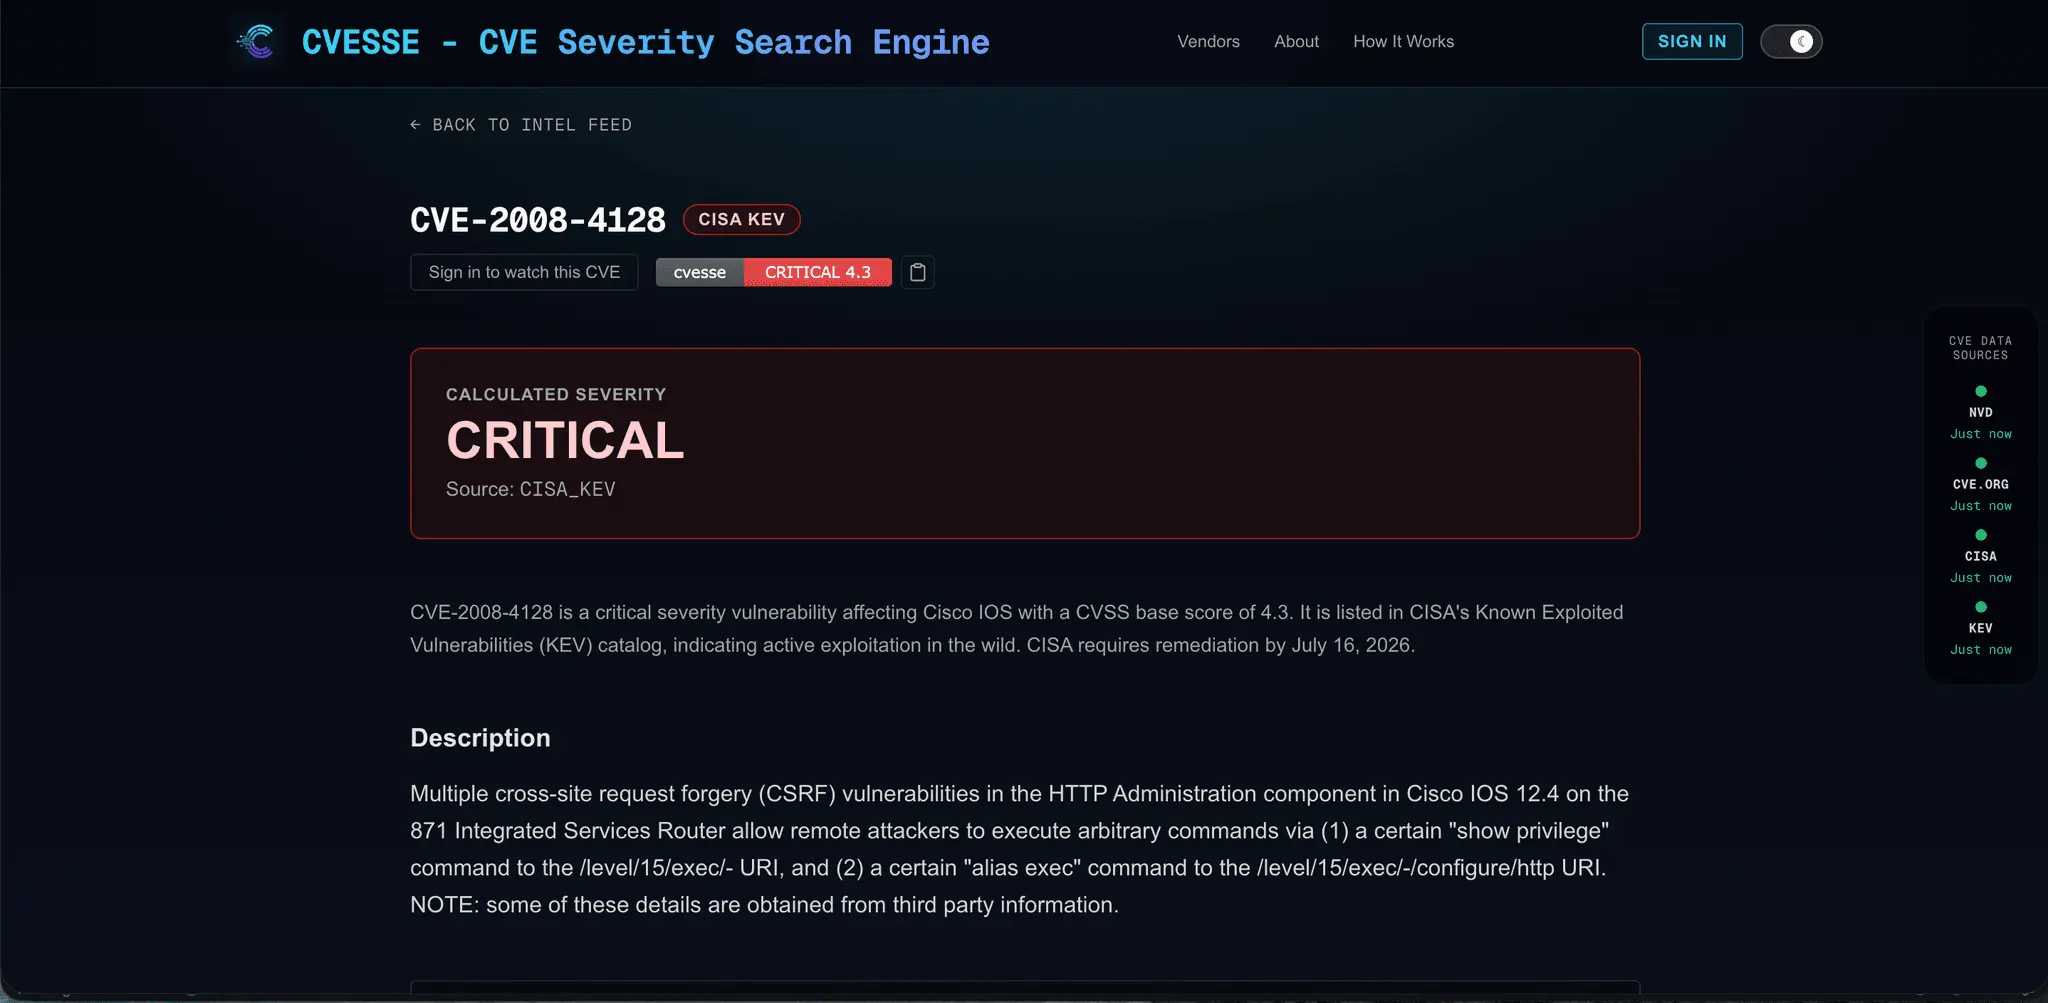
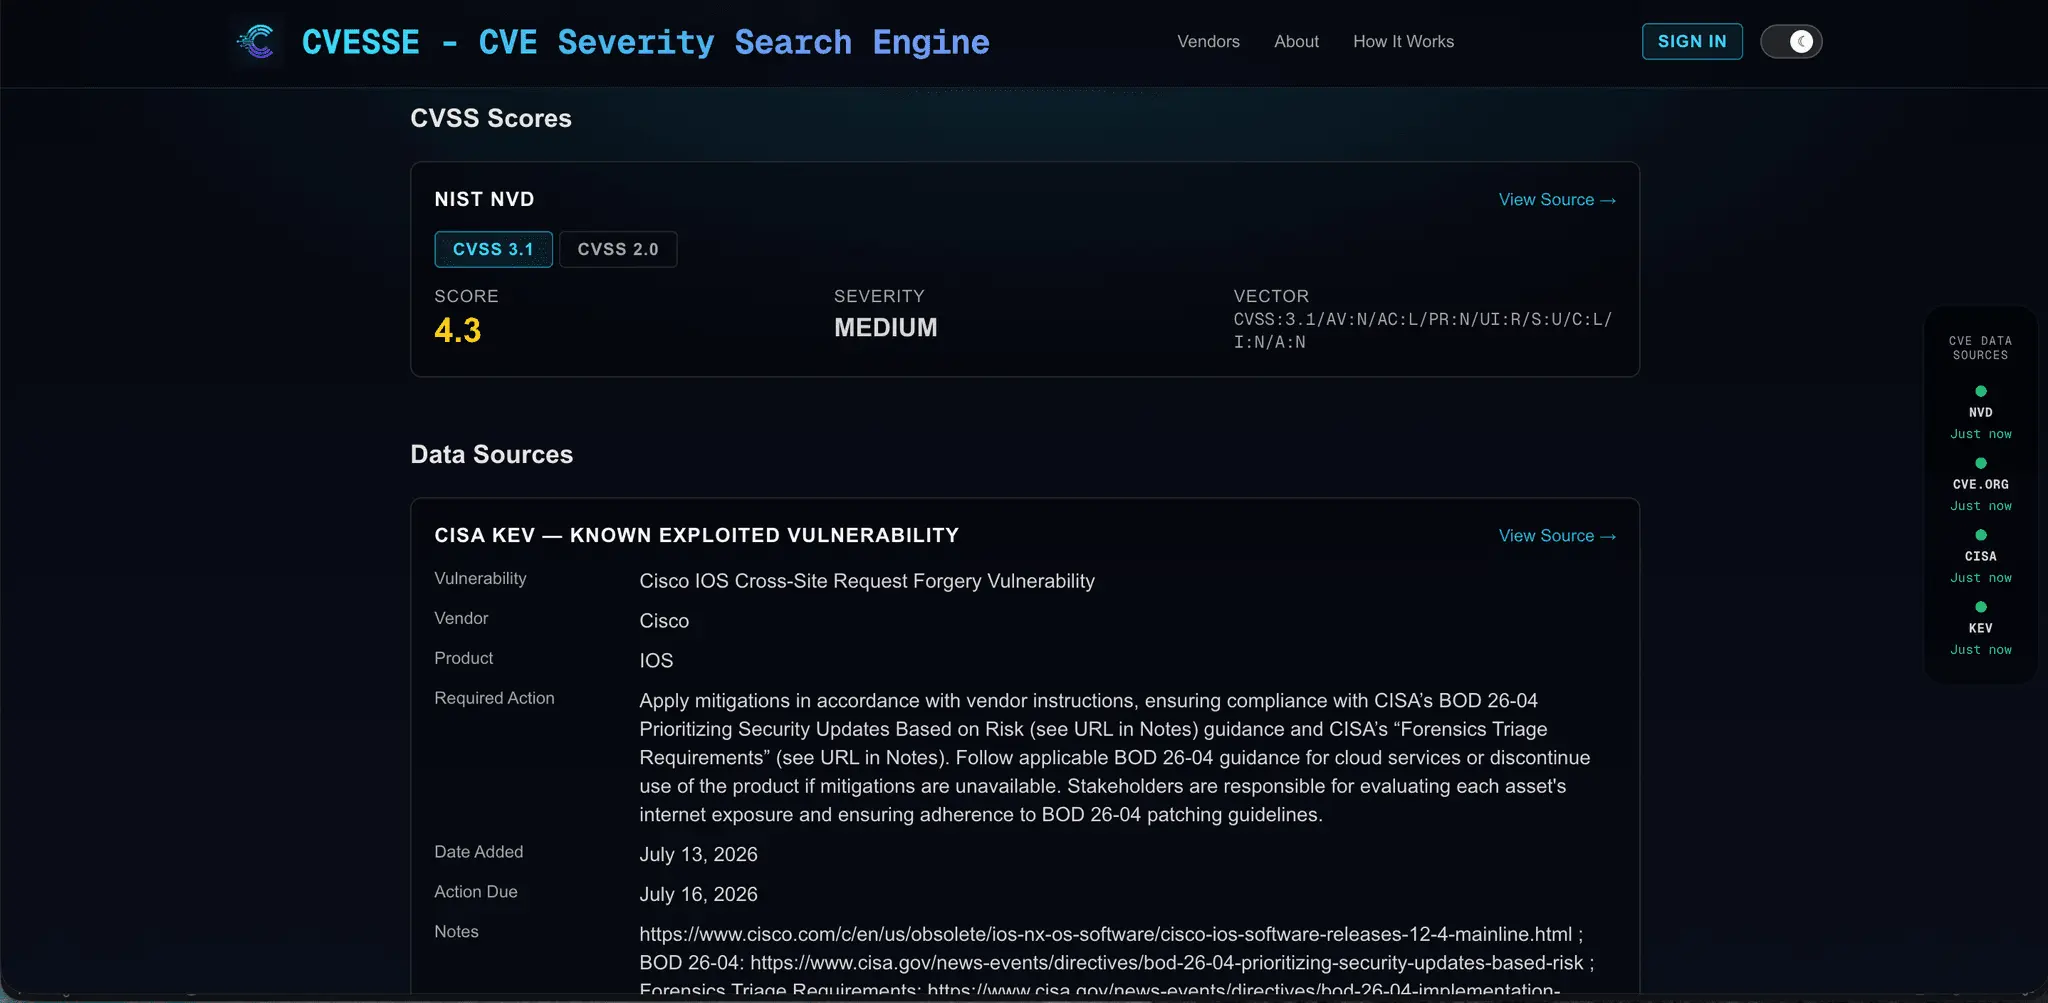
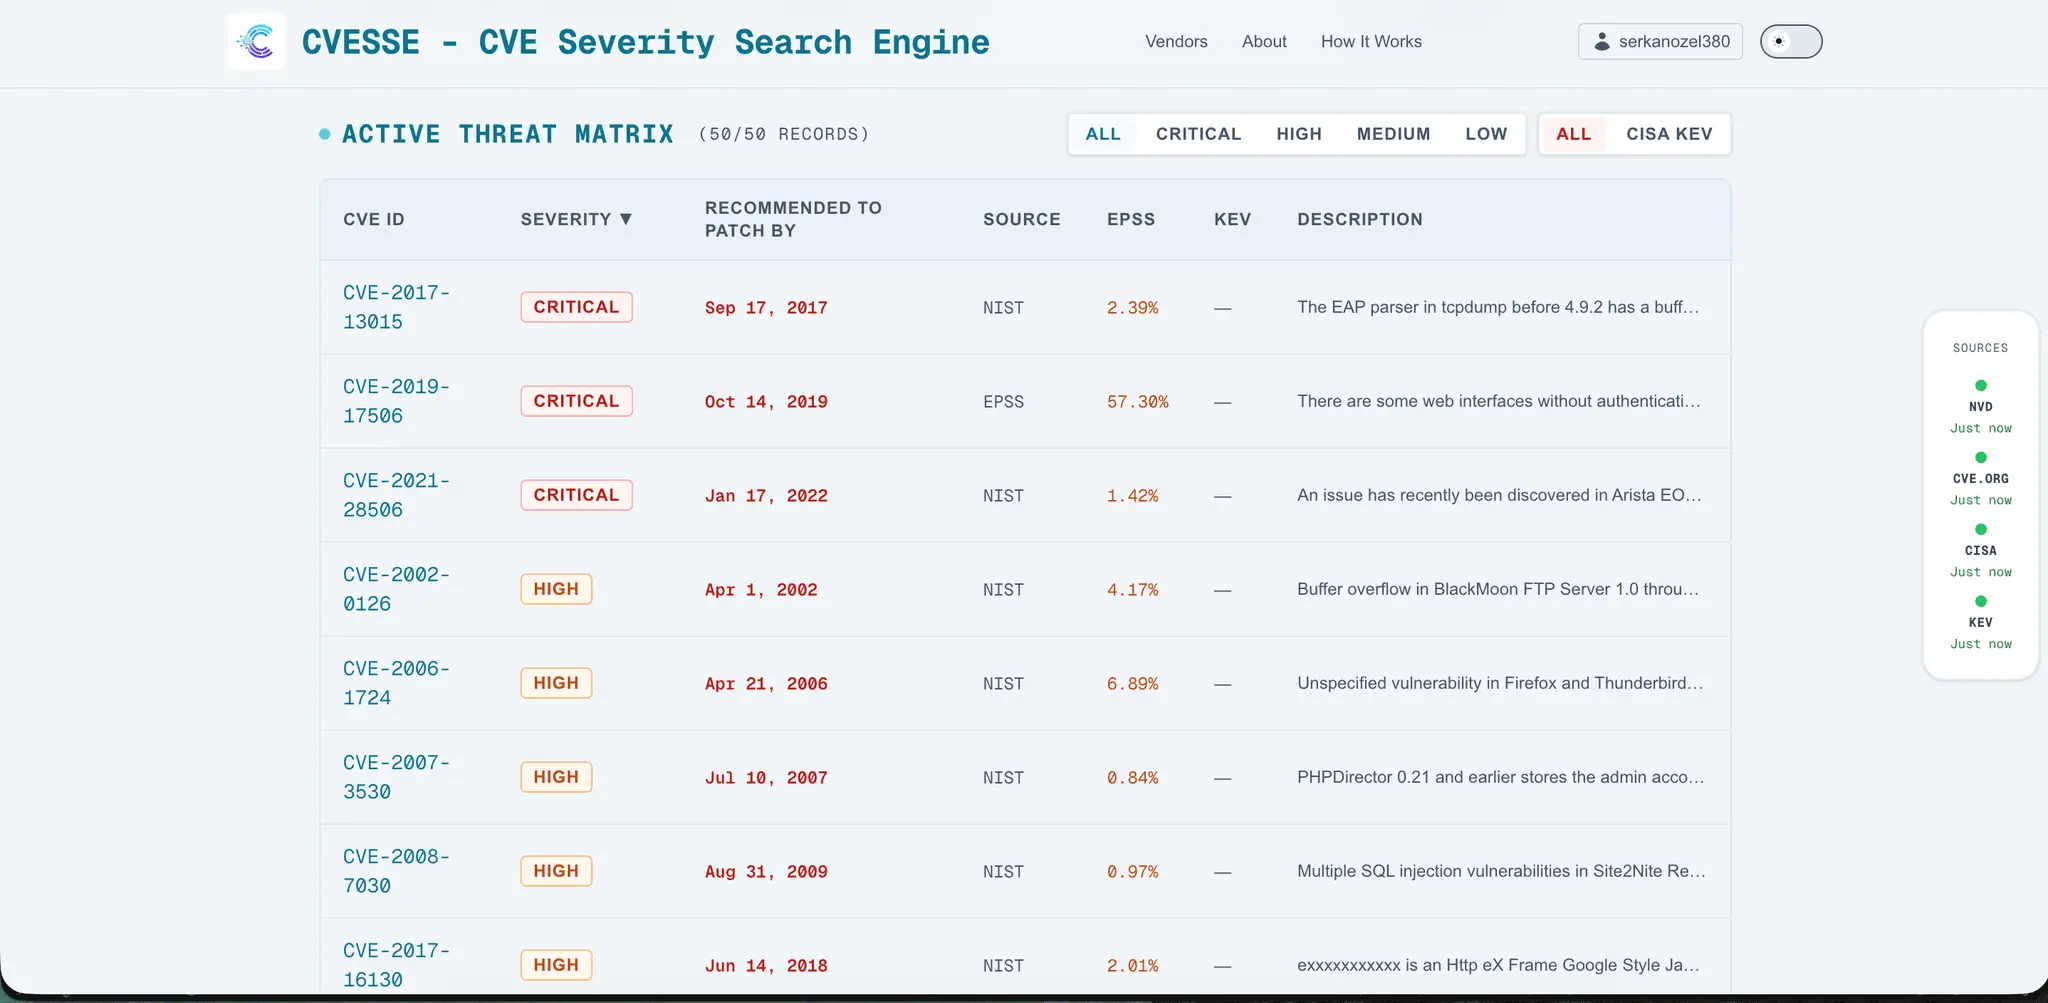
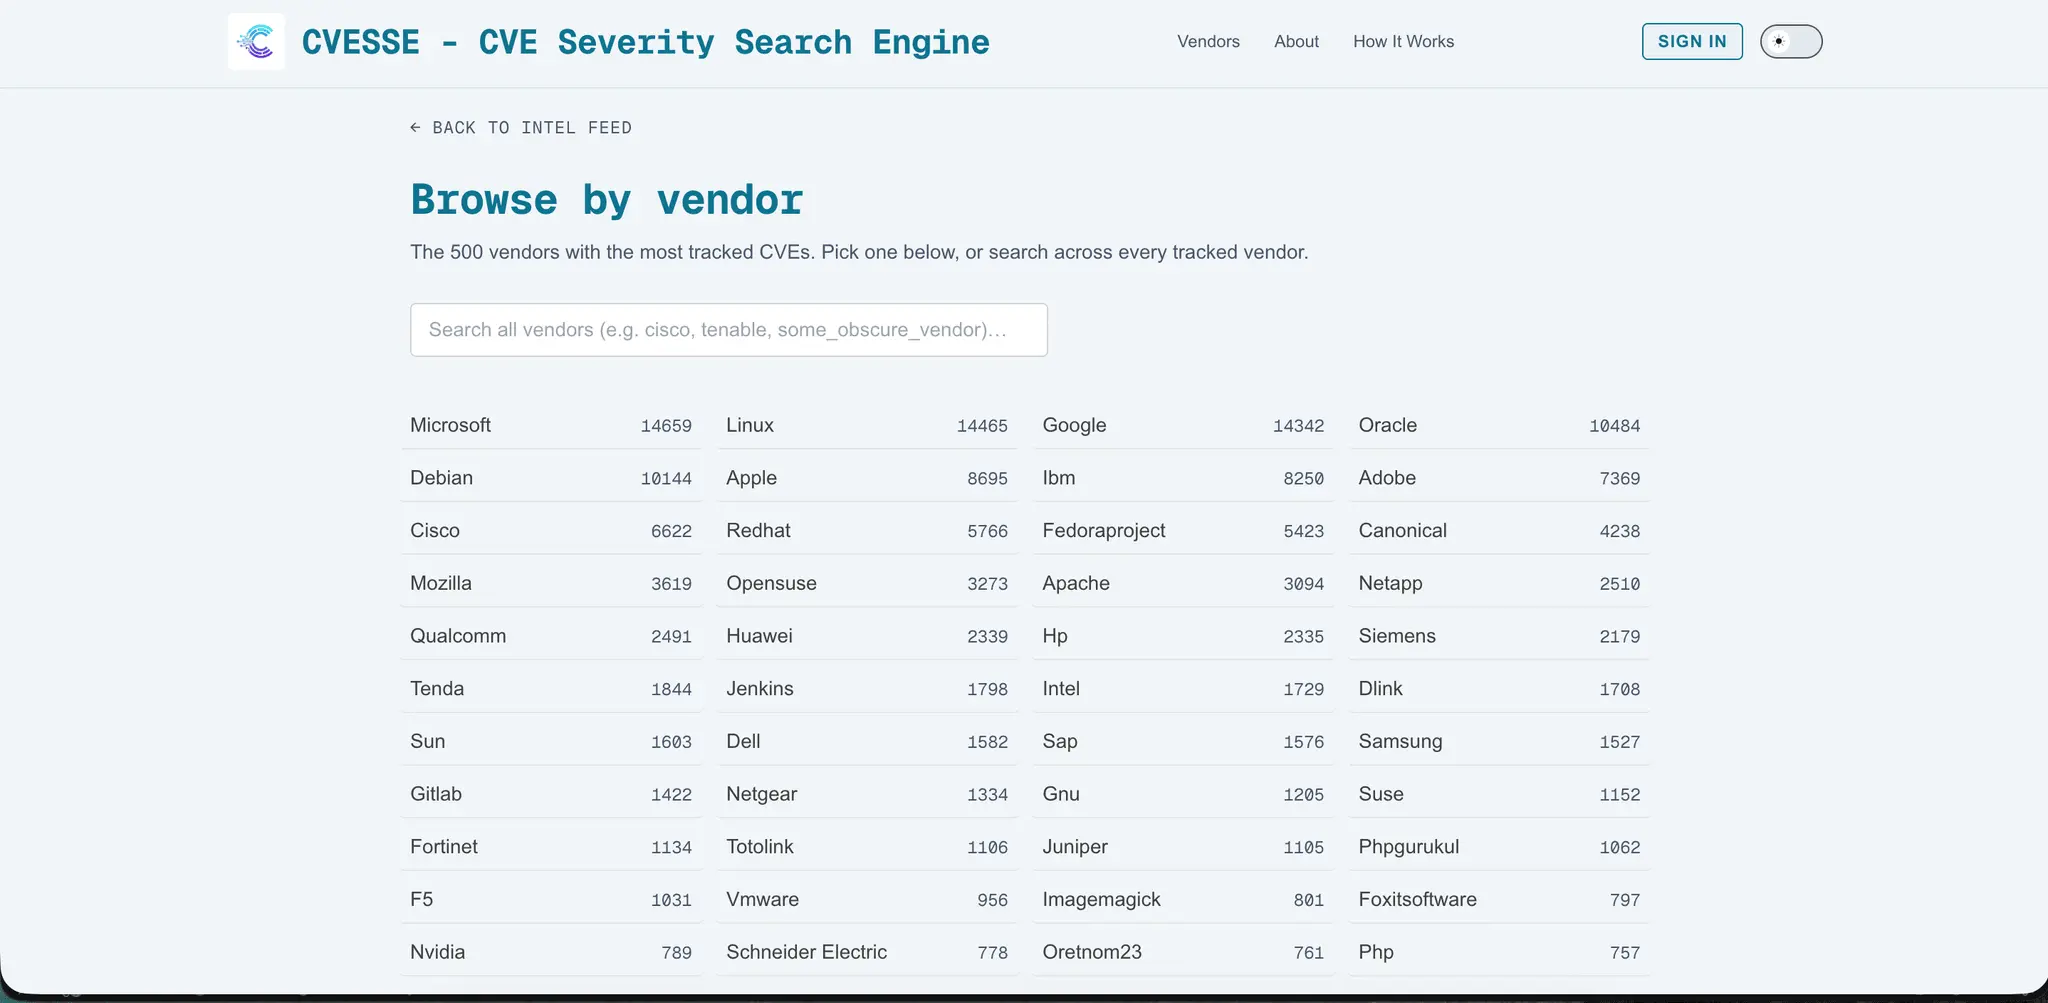
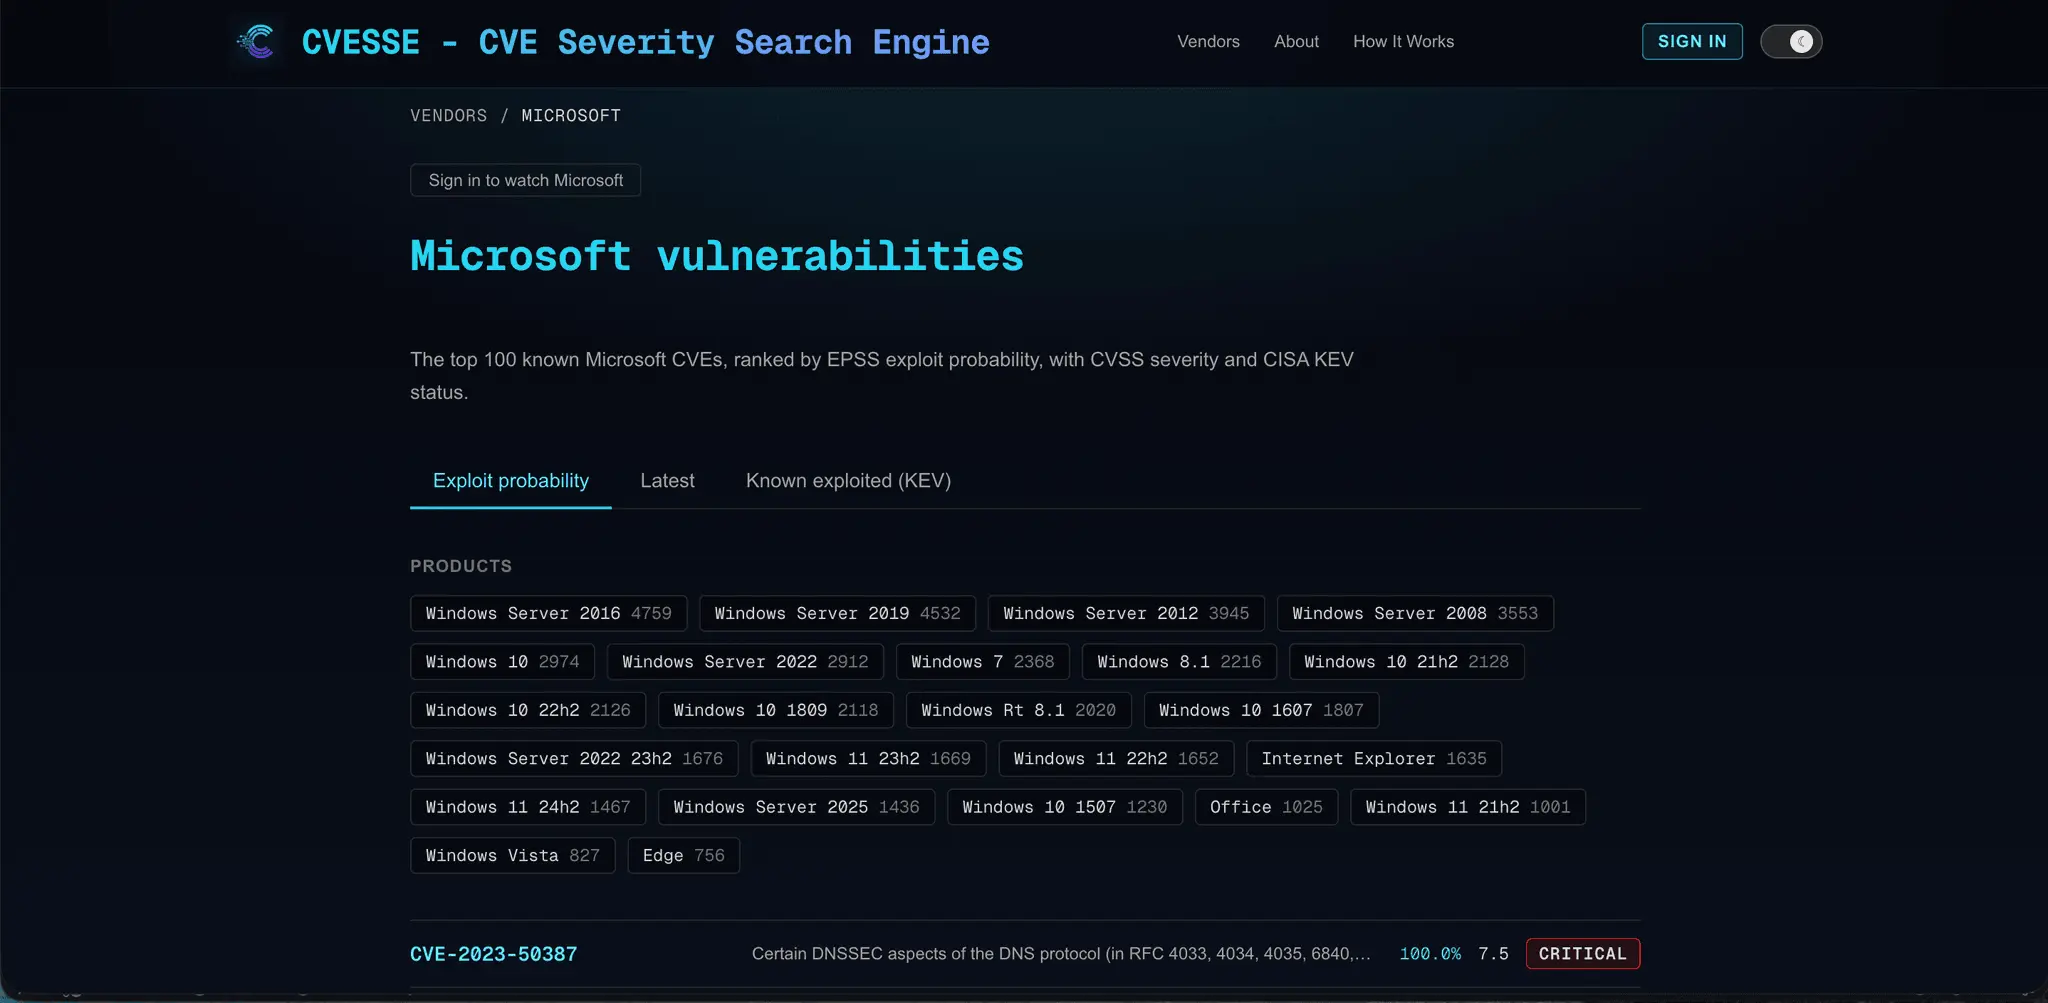
The problem: answering "what should I patch first?" today means checking NIST NVD for CVSS scores, CISA KEV for active exploitation, FIRST EPSS for exploit probability, and CVE.org for the authoritative record. Four tabs, four data formats, and no single ranking. What CVESSE does: it ingests all four sources into one pipeline covering hundreds of thousands of CVEs, runs them through a priority-based severity engine, and serves a unified record per CVE — CVSS, EPSS percentile, KEV status, affected vendors/products (CPE), and weaknesses (CWE) — so the most dangerous vulnerabilities surface immediately. Built on Cloudflare's edge, pages load fast globally and data stays fresh via a continuously running collection pipeline with visible source-freshness status. Feature list Unified CVE records — NVD, CISA KEV, EPSS, and CVE.org merged into one page per CVE; no more cross-referencing. Priority-based severity engine — every CVE ranked so critical, actively-exploited vulnerabilities float to the top. Live intel feed & severity dashboard — see the current threat landscape at a glance, filterable by severity. Vendor & product pages — browse every CVE affecting Microsoft, Cisco, your stack — one URL per vendor/product. CVE watches with email alerts — watch a CVE or a vendor, set alert rules, get emailed when severity, EPSS, or KEV status changes. Embeddable severity badges — shields.io-style SVG badge for any CVE (cvesse.com/badge/CVE-2024-3094.svg) for READMEs, advisories, and docs. API access with keys — programmatic access to CVE data for your own tooling and pipelines. Transparent data freshness — a sources page and per-page "Last Data Collection" card show exactly when each upstream was last synced. Fast everywhere — edge-deployed (Cloudflare Workers), aggressively cached, no login required to search. Who it's for SOC analysts triaging alerts, security researchers, DevOps/IT admins doing patch management, and anyone tired of tab-hopping between NVD, KEV, and EPSS.
Screenshots
Reviews (0)
No reviews yet. Be the first to rate this product!
Comments (1)
are there any docs that I can refer?