Intel60
Severity-rated cybersecurity news in 60 words
Details
- Follow on
- Categories
- Use Cases
- Target Audience
- Pricing
- Free
Discovery signals
How AI and people discover Intel60 on PeerPush
About Intel60
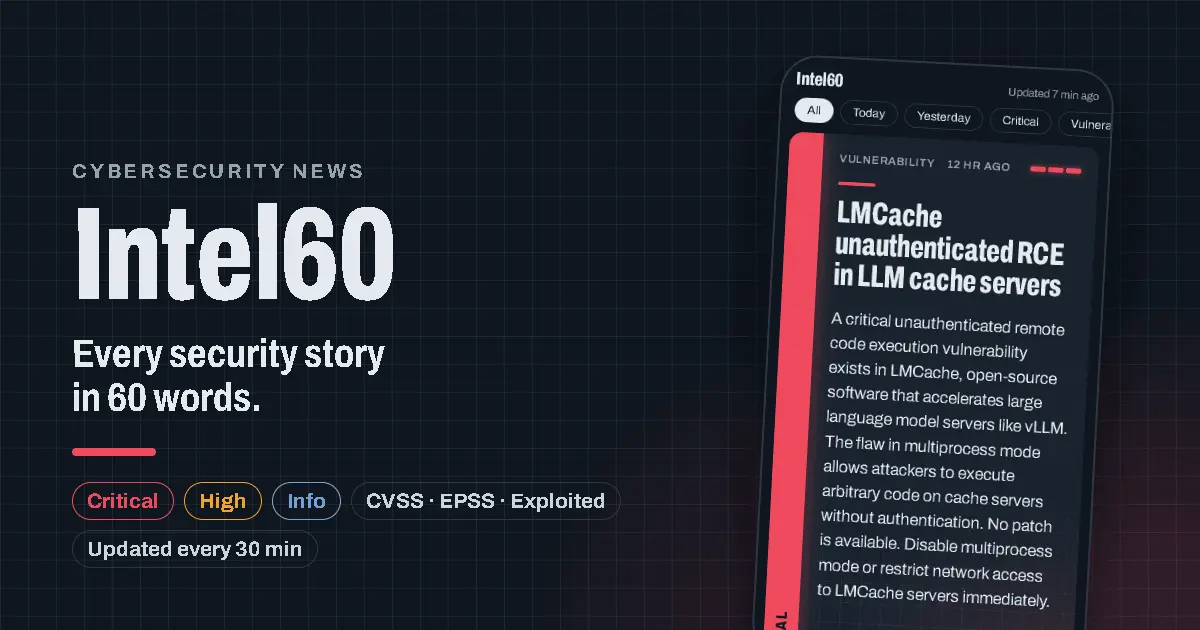
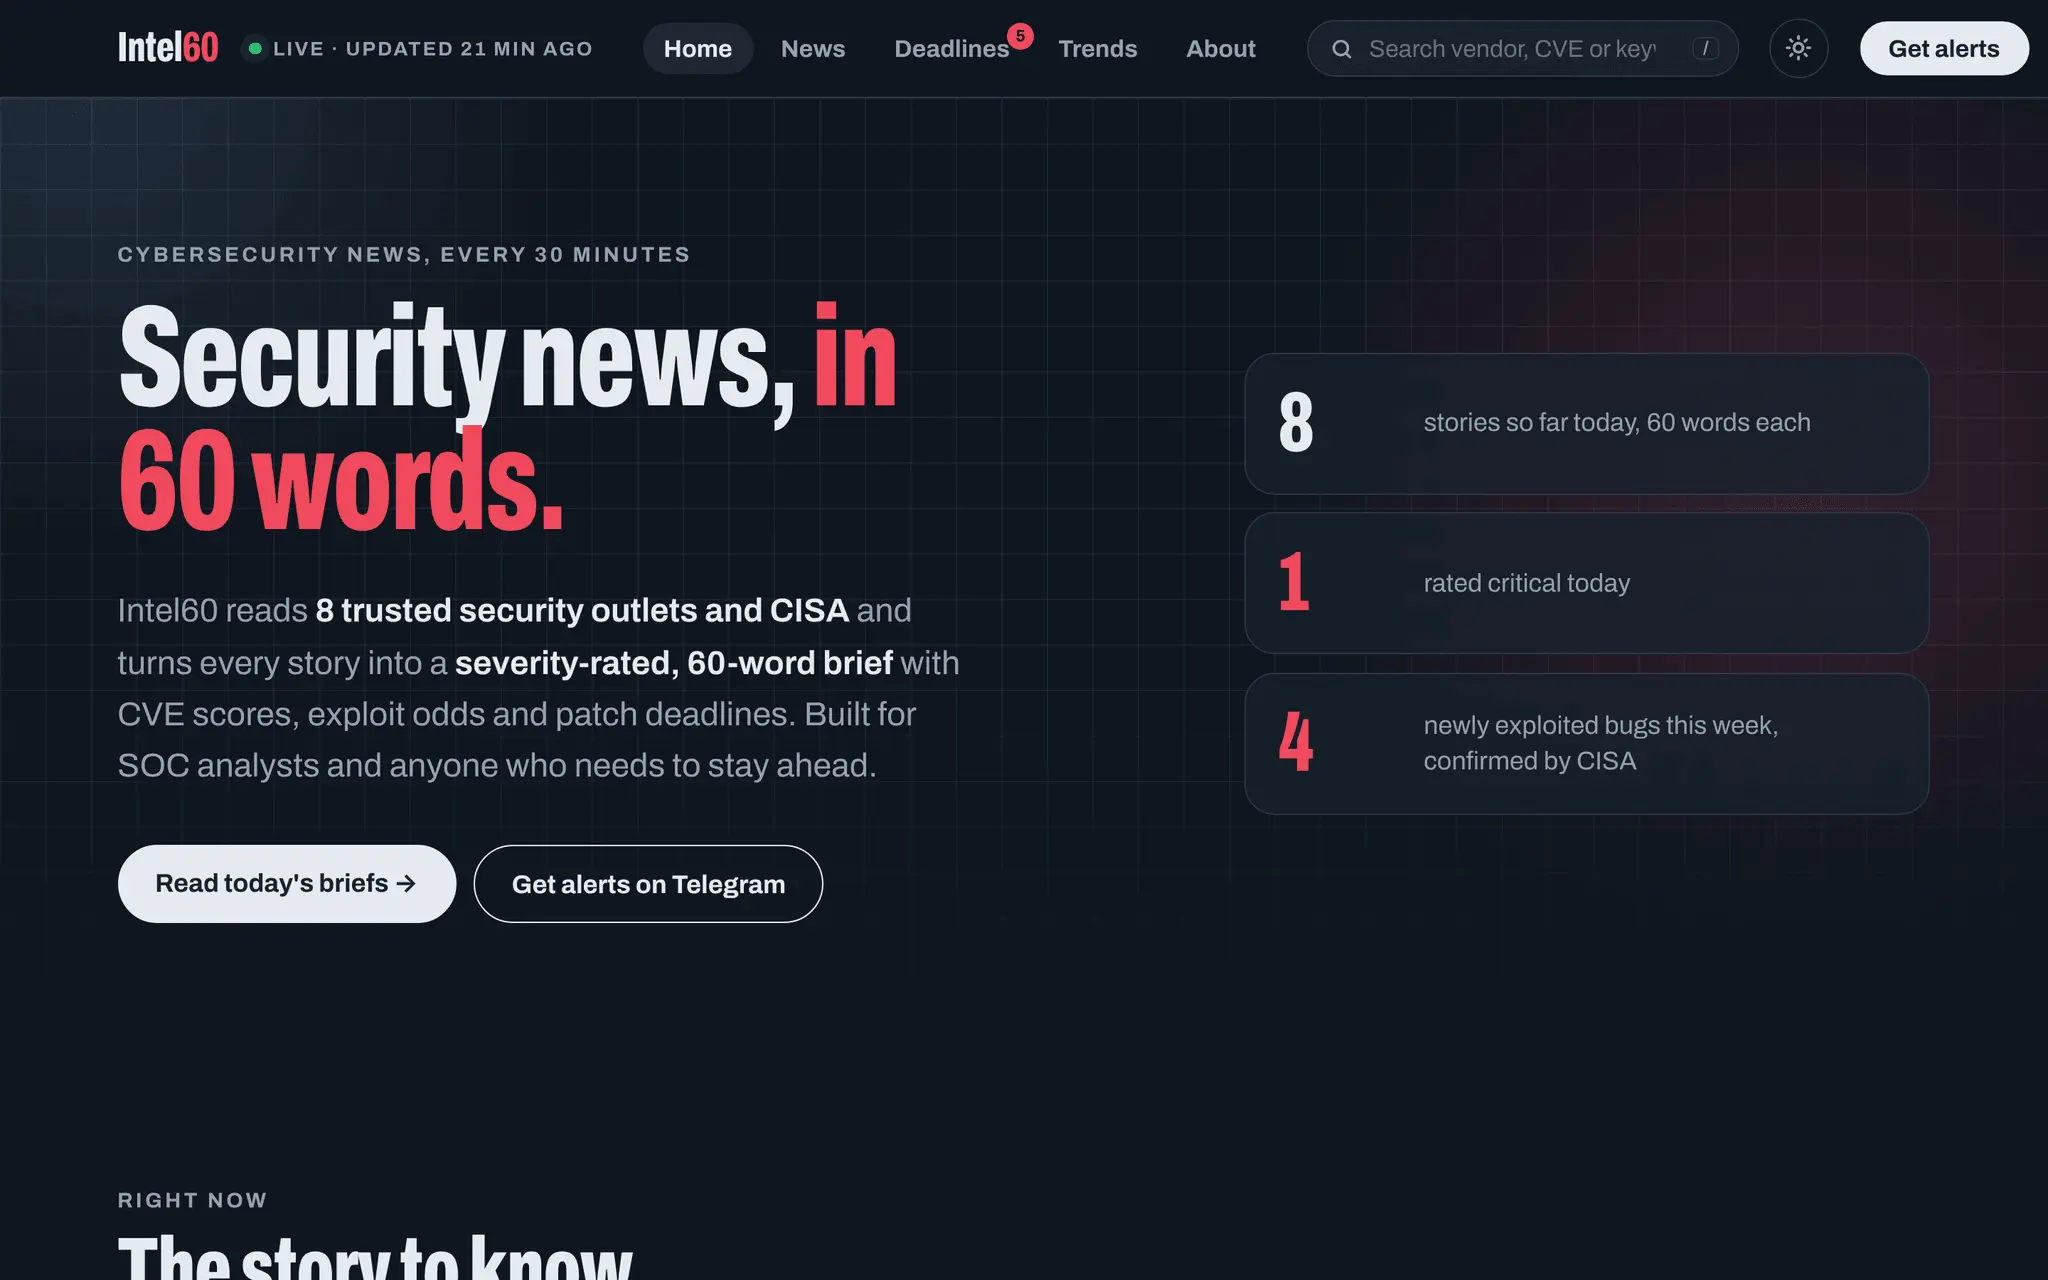
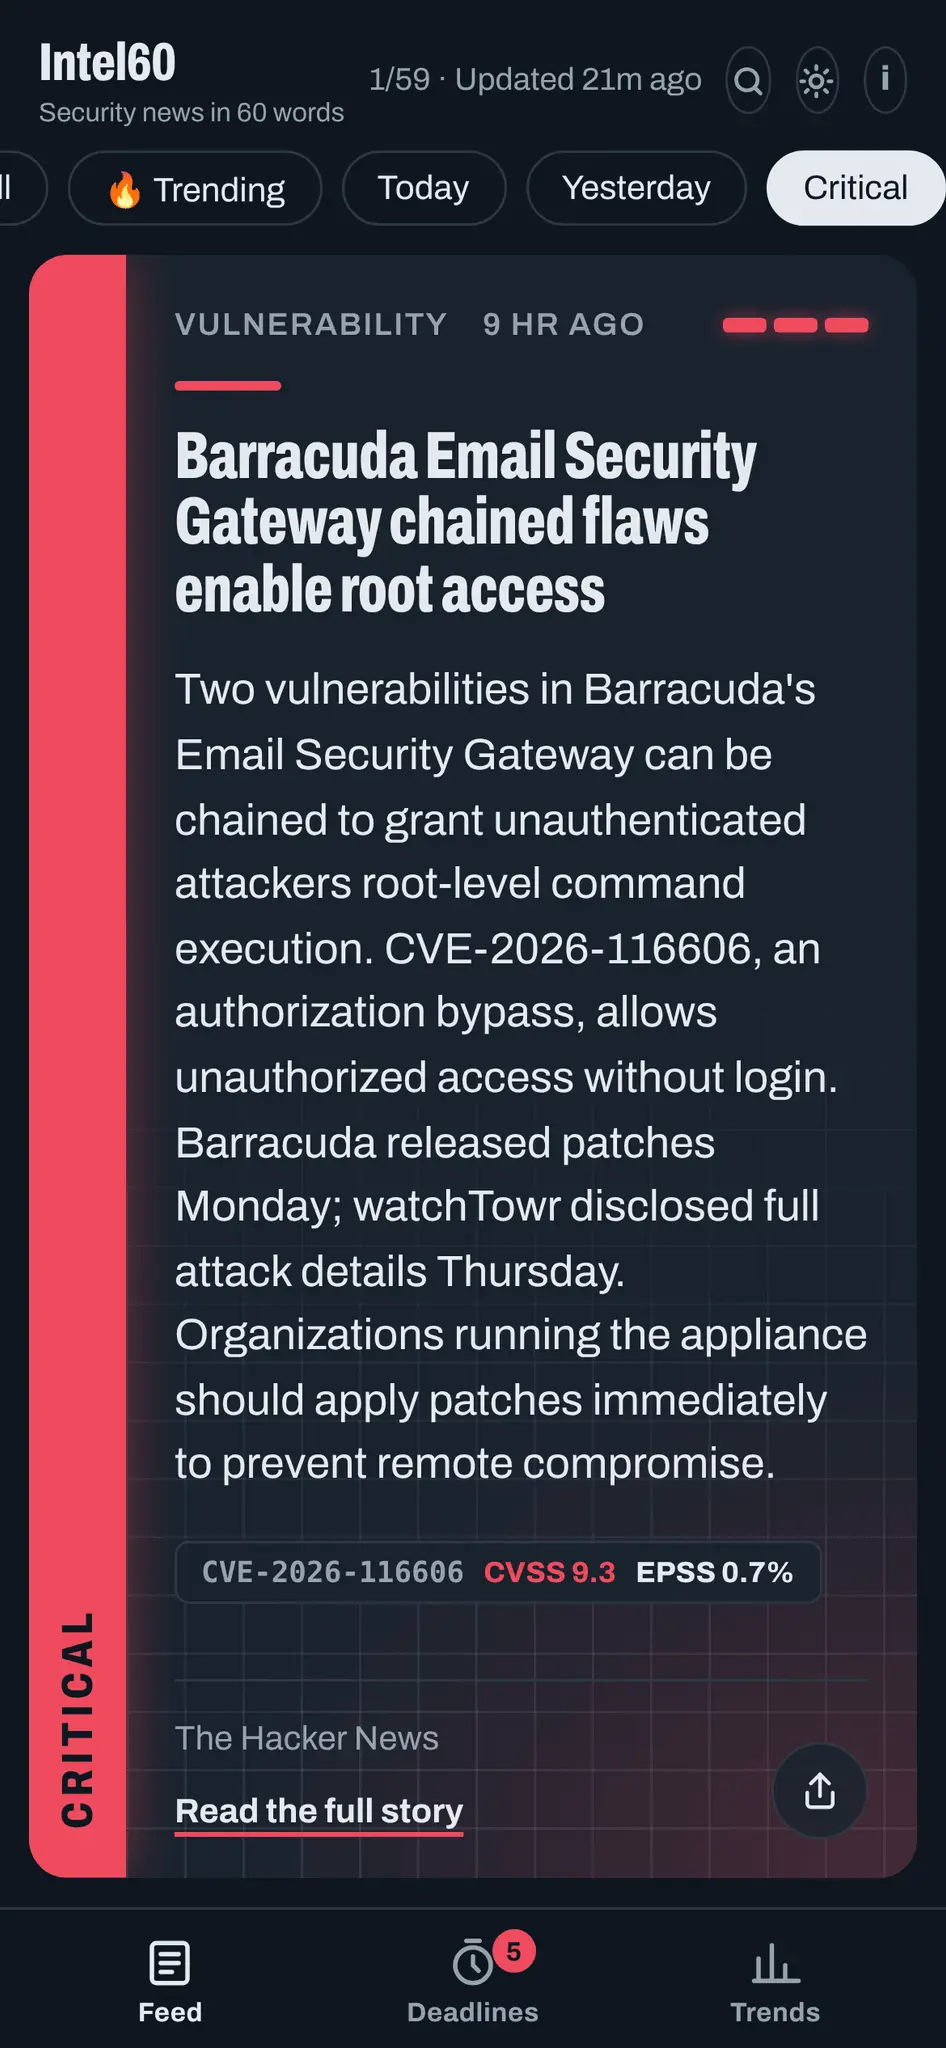
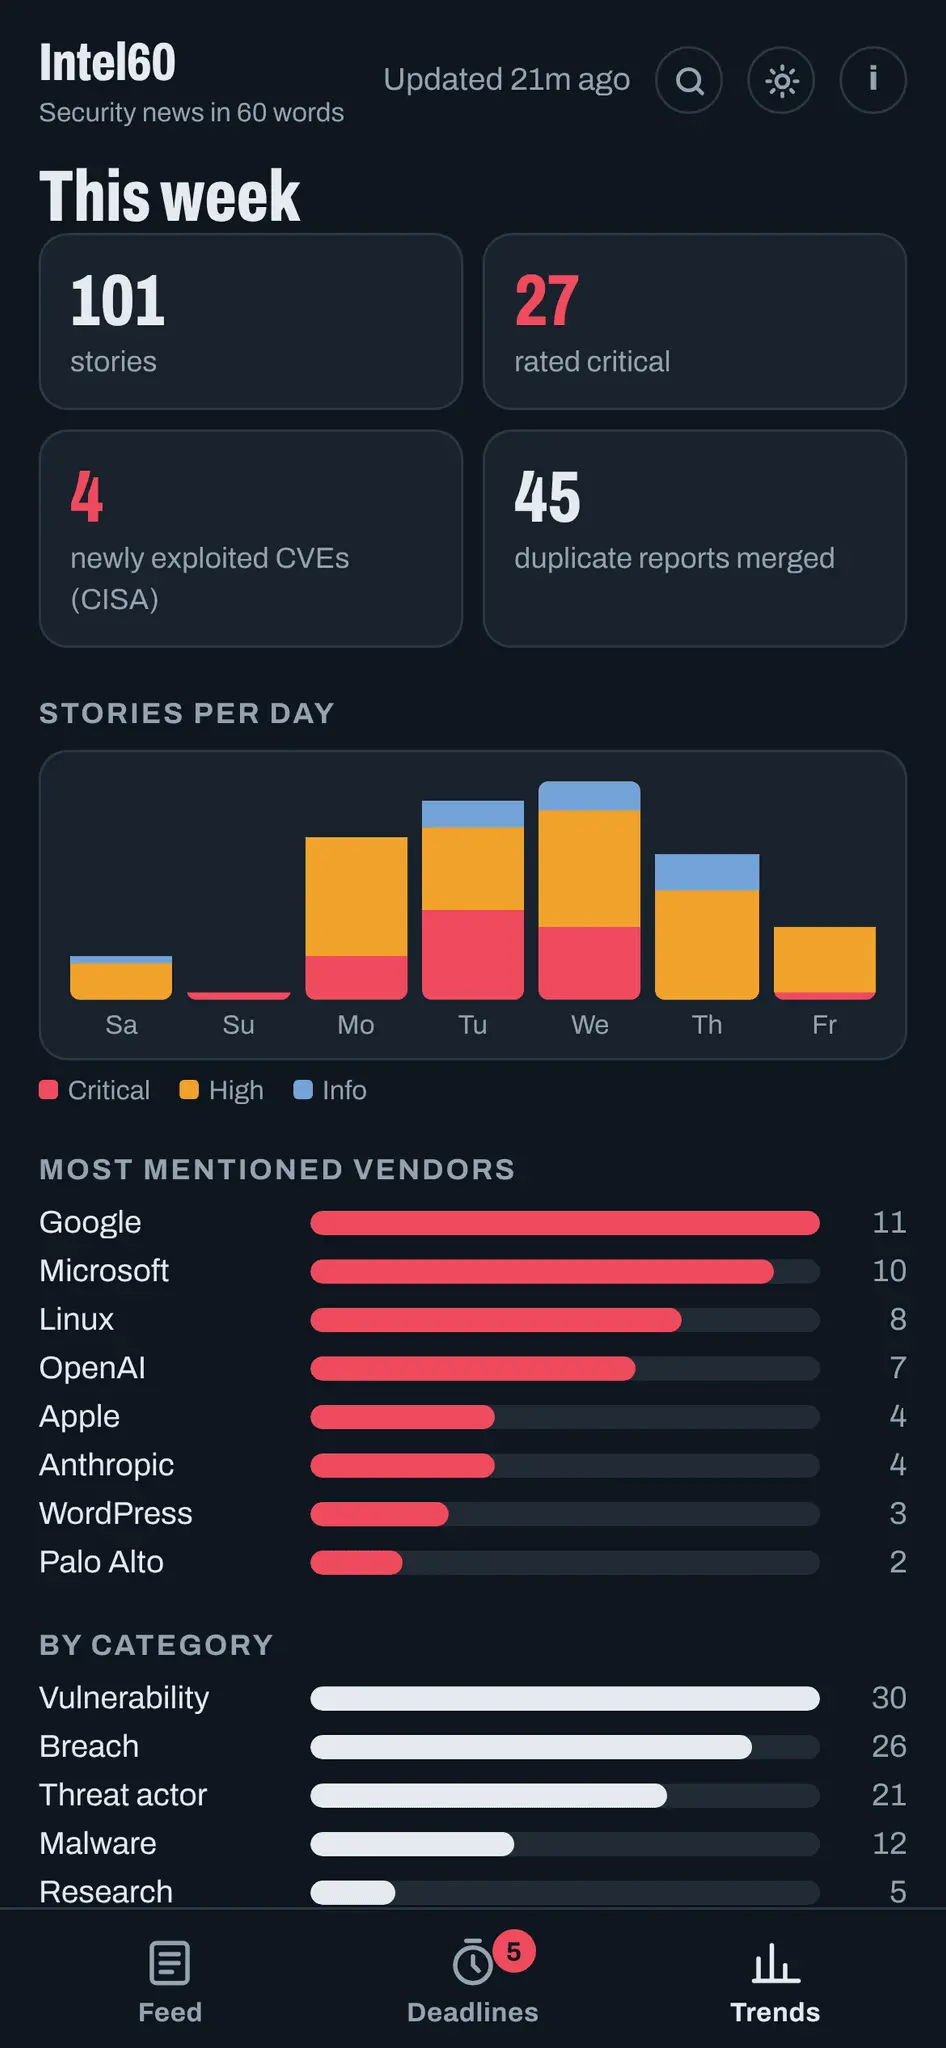
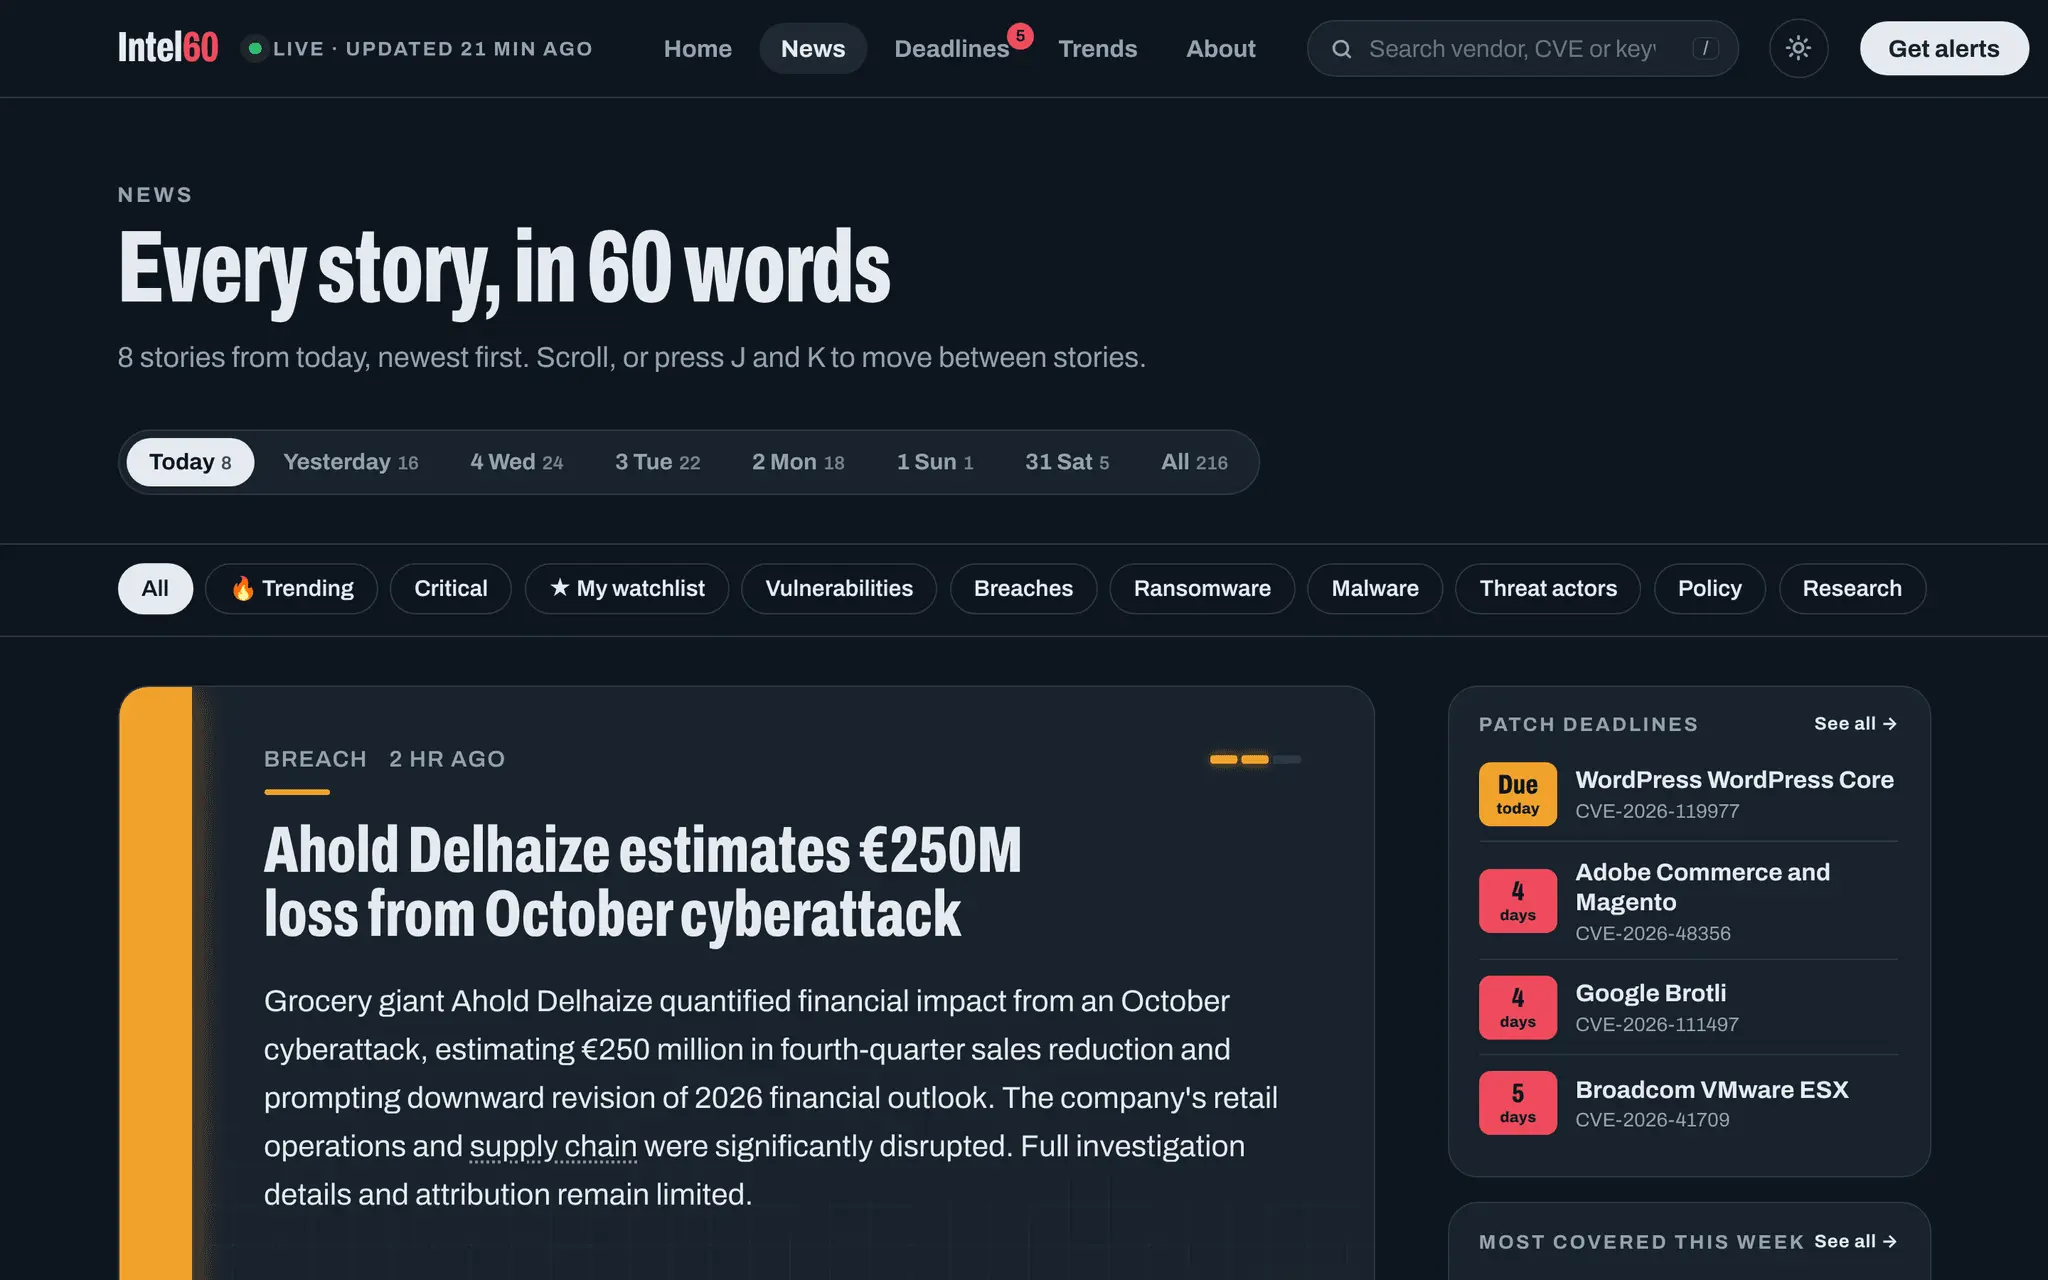
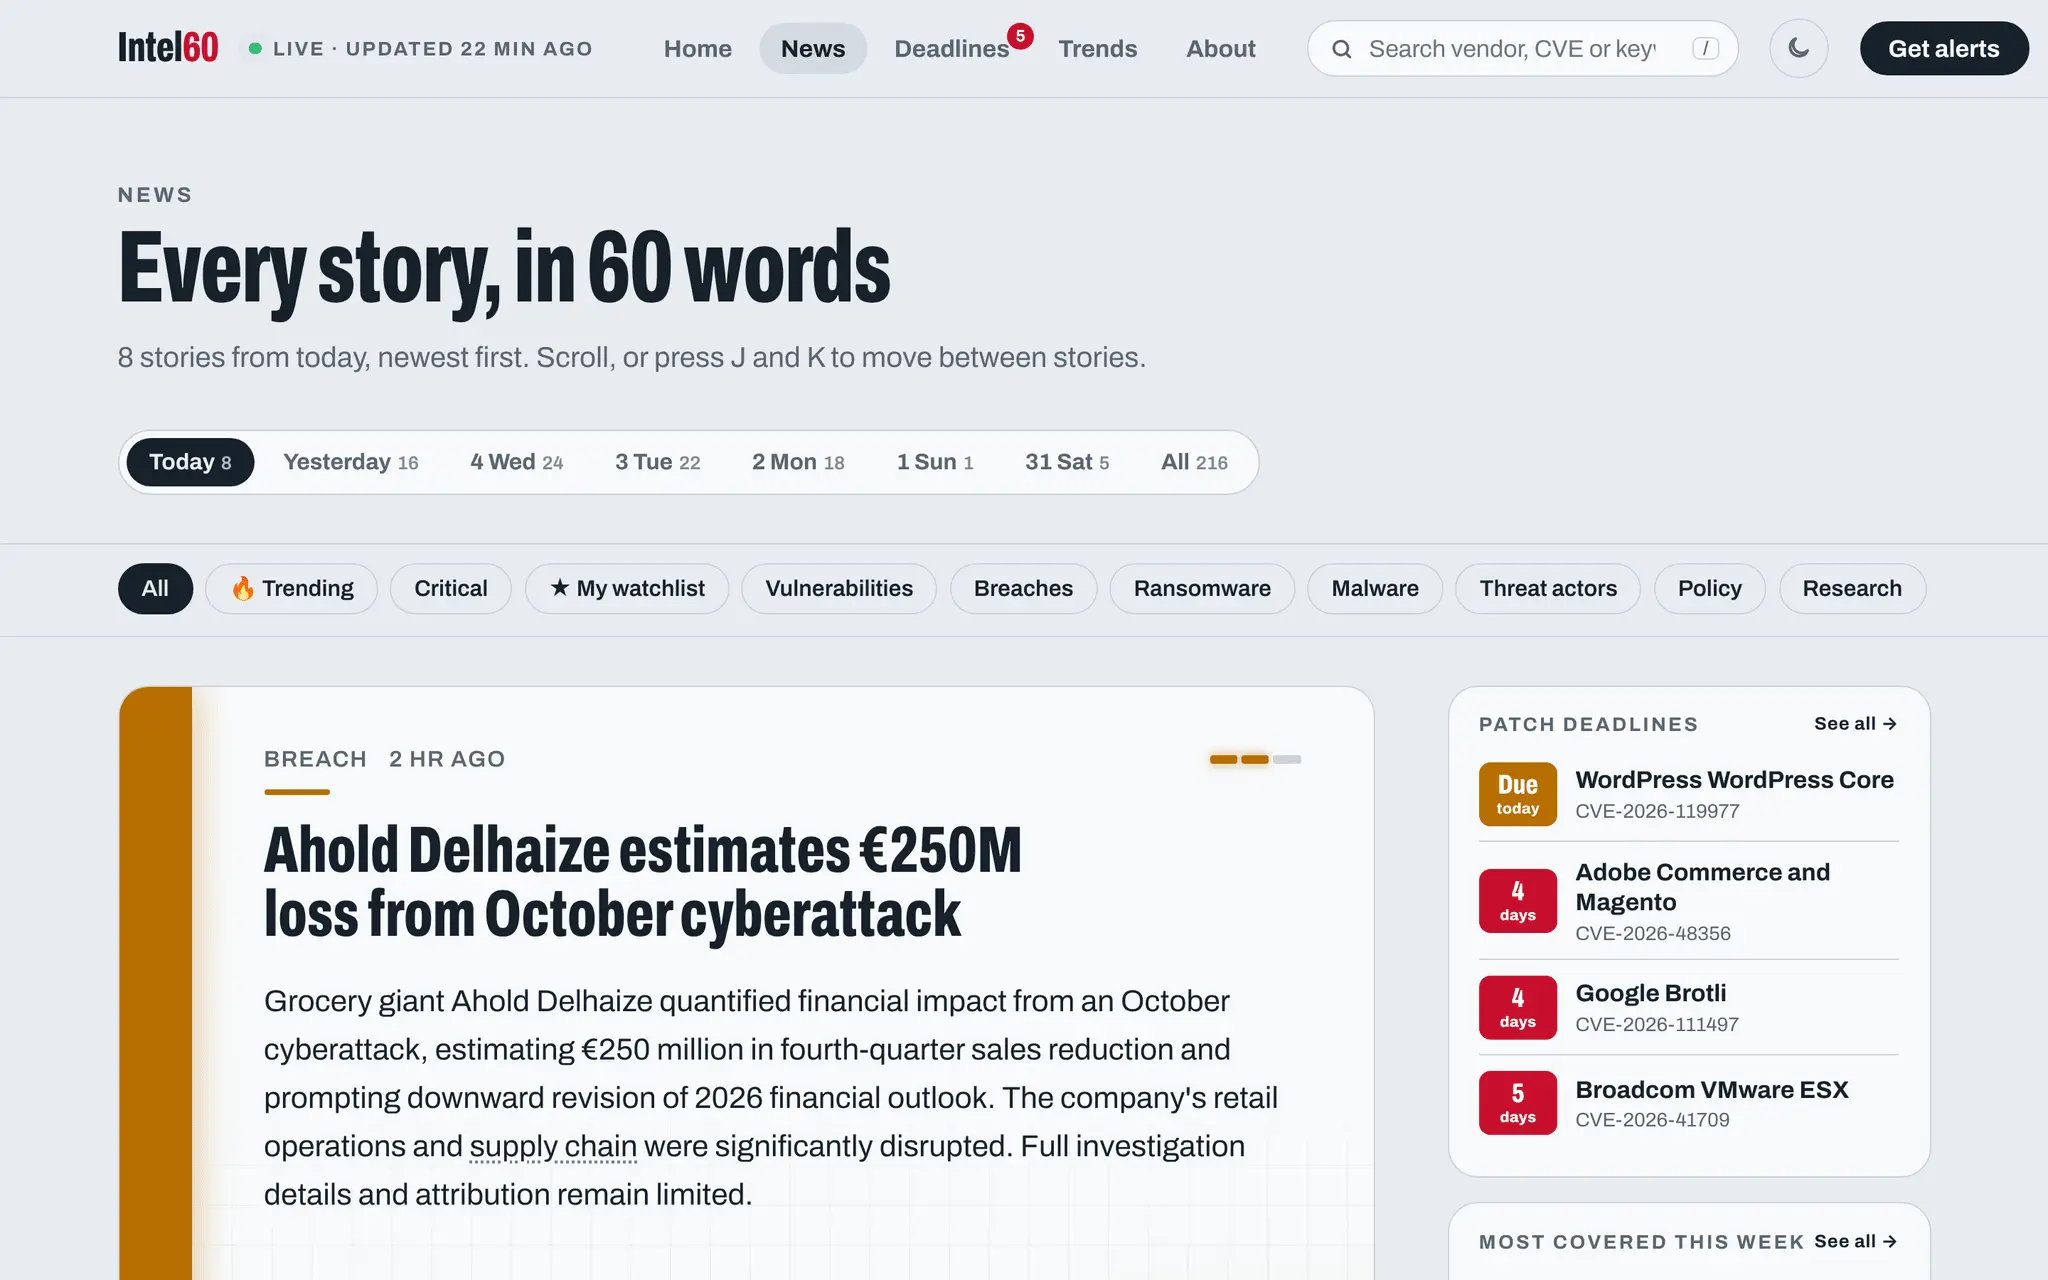
Security news is scattered across dozens of sites and newsletters, and the one story that matters, an actively exploited vulnerability in software you run, looks just like the hundred that don't. Analysts either spend an hour a day reading or miss things. Intel60 fixes that by turning cybersecurity news into short, severity-rated briefs you can scan in minutes. How it works: every 30 minutes, Intel60 pulls the latest stories from 8 trusted sources (BleepingComputer, The Hacker News, SecurityWeek, The Record, Dark Reading, Krebs on Security, CyberScoop and SANS ISC) plus the CISA Known Exploited Vulnerabilities catalog. AI condenses each story into a 60-word brief covering what happened, who's affected, patch status and what to do, then rates it critical, high or info. Duplicate coverage of the same incident is merged into one card. Every CVE is enriched with real data: its CVSS severity score (NVD), its probability of exploitation (FIRST EPSS), and whether it's being actively exploited (CISA KEV). Also included: - Deadlines view counting down CISA patch due dates - Trends view showing the week's top vendors and severity mix - Explain mode that defines terms like RCE and KEV in plain English - Critical alerts via a public Telegram channel - Links to the original article on every card Built for SOC analysts, IT teams, students and anyone who needs to stay current without the noise. Free, no account needed, installable on your phone, and open source.
Product Video
Watch a video demo of Intel60.
Screenshots
Reviews (0)
No reviews yet. Be the first to rate this product!
Comments (1)
How do you pick the severity rating for each item? With only 60 words per story I can see the rating being the part readers rely on most, so I'm curious whether you link back to the original advisory.
AI rates each story with a fixed rubric (exploited/KEV or CVSS 9+ = critical) and shows CVSS, EPSS and KEV data on every card. Cards link to the source article; clickable CVE links to NVD and advisories are coming next.