Literal Security
Site offlineReal-time security scanning for AI-generated content

Details
- Follow on
- Categories
- Target Audience
- Pricing
- Subscription from $14.99
Discovery signals
How AI and people discover Literal Security on PeerPush
- ChatGPT
- Perplexity
- +3 other AI crawlers
Reads by these AI engines
Crawlers behind these engines read this listing on PeerPush.About Literal Security
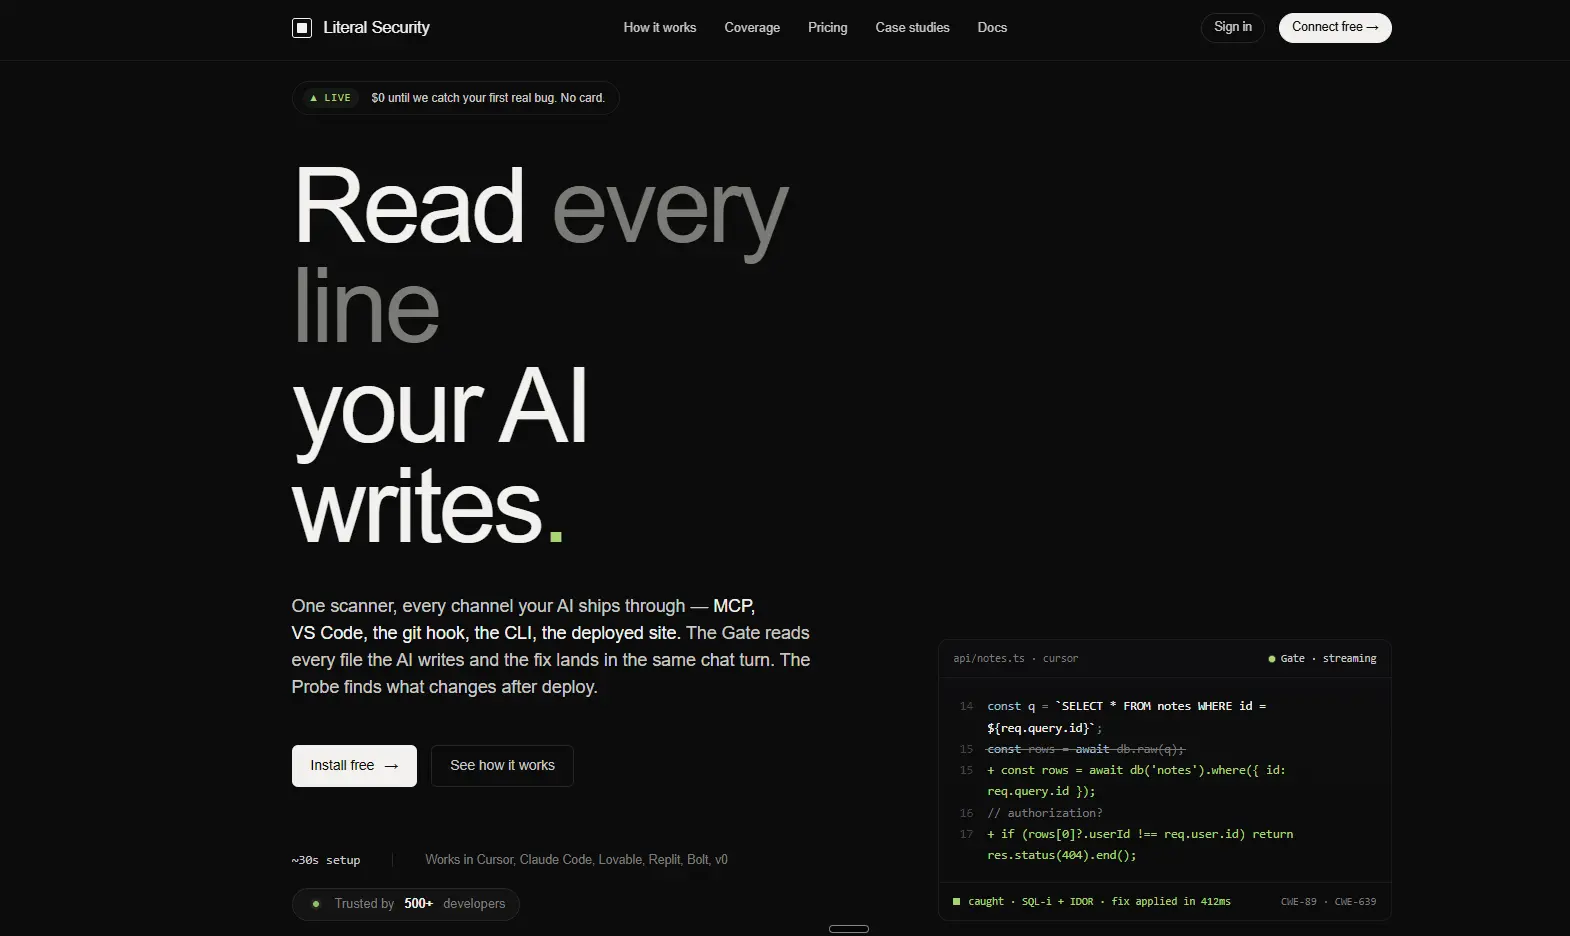
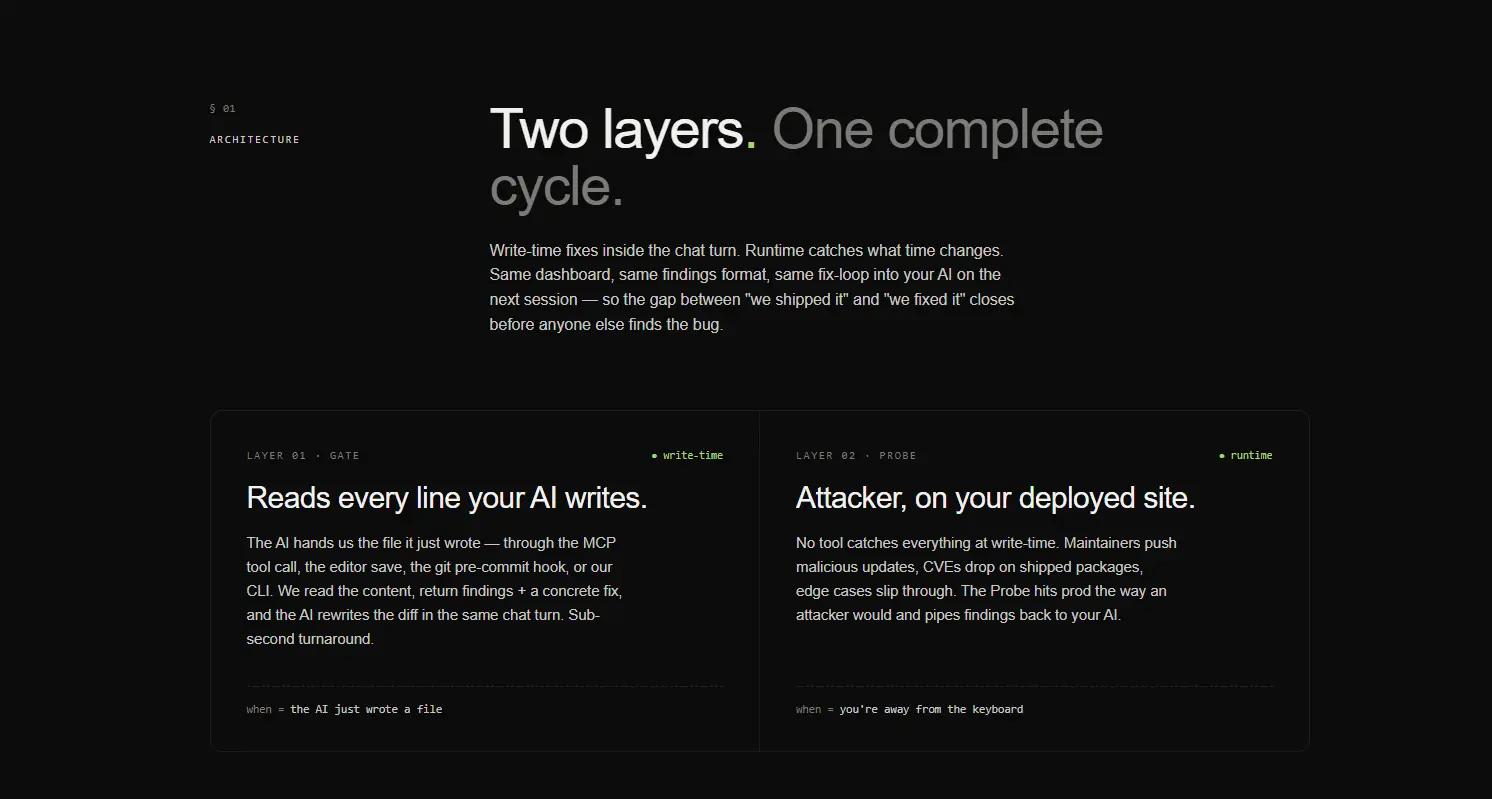
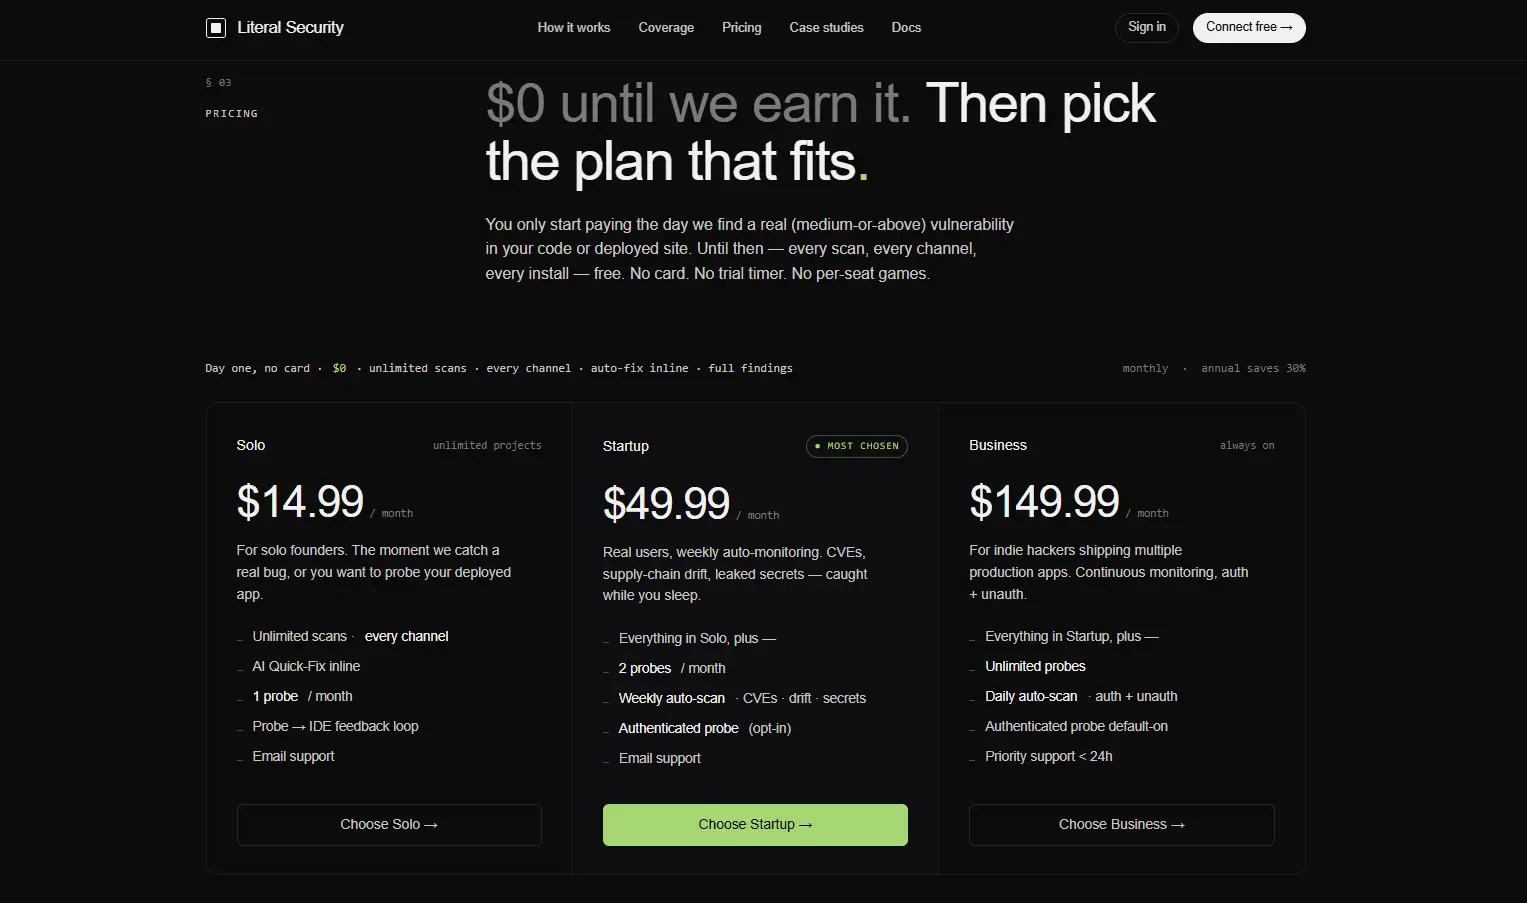
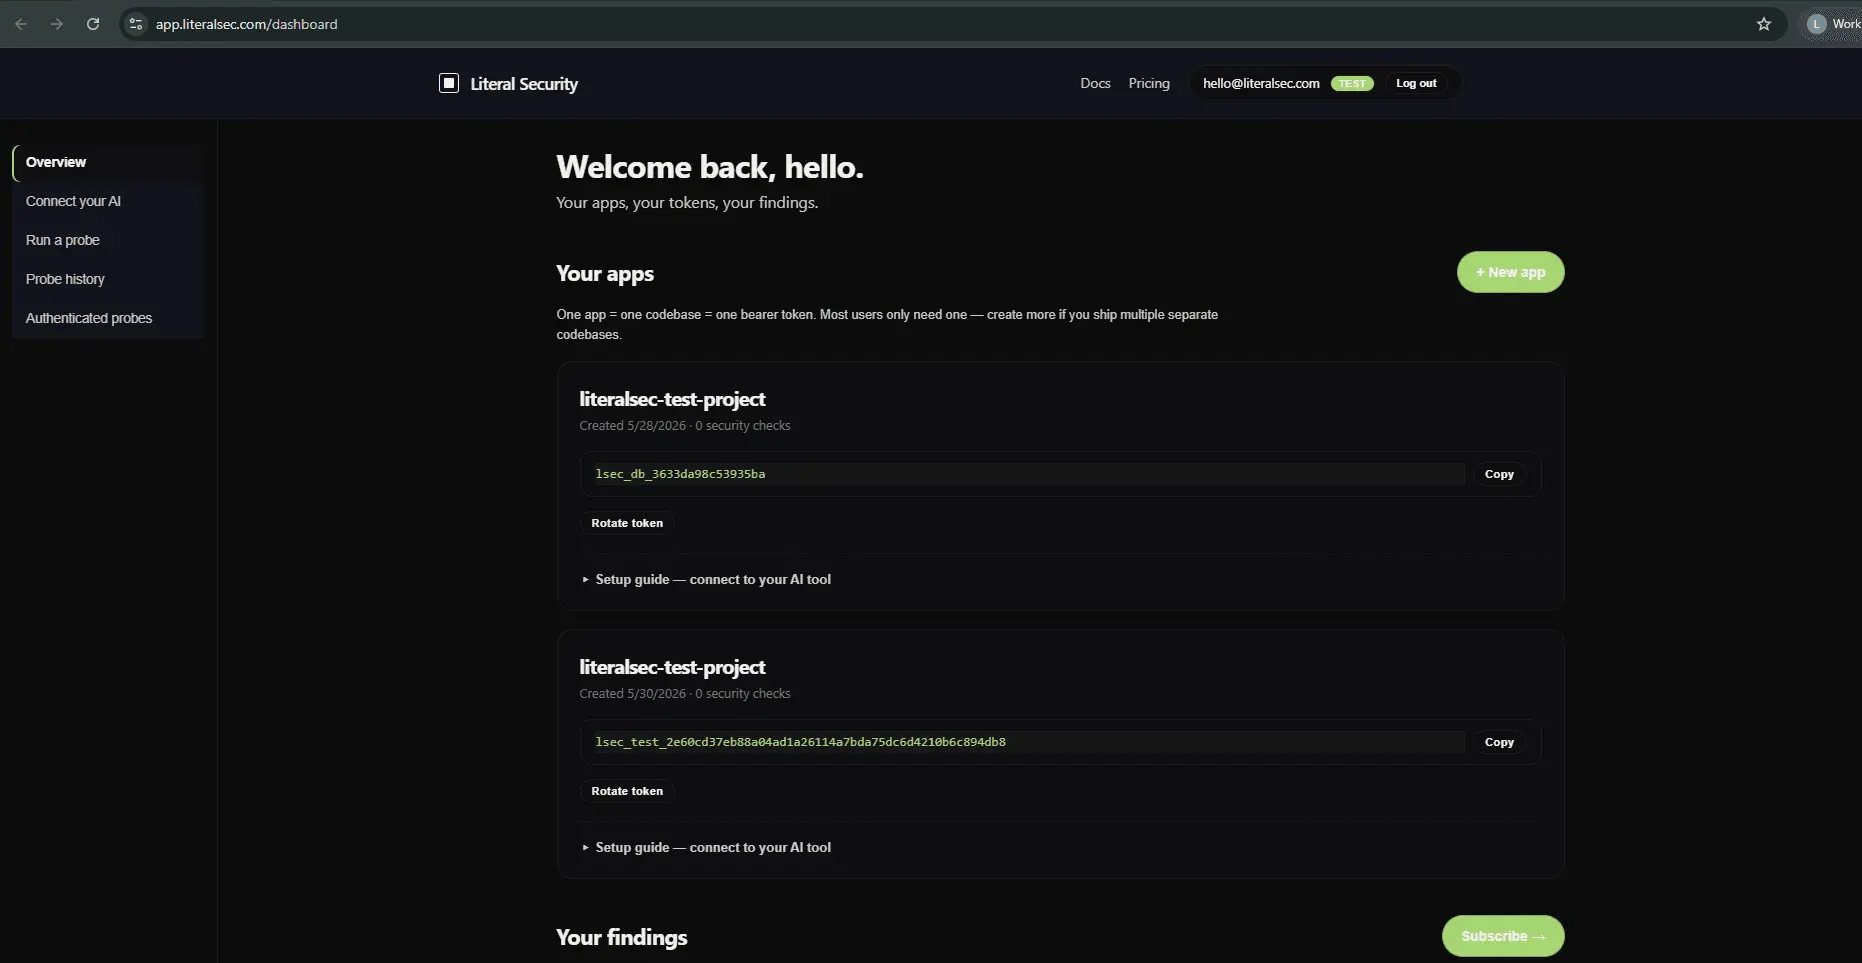
Literal Security is the AI security layer for vibe-coded apps. We catch the bugs AI loves to ship hardcoded API keys, missing auth on admin routes, exposed source maps in production, supply-chain attack surface by plugging into every channel the AI writes through (Cursor, Claude Code, Lovable, Replit, Bolt, v0, plus a CLI, VS Code extension, and git pre-commit hook). Findings come back in the same chat turn with concrete remediation code, applied by the AI before the file lands on disk. After deploy, an active probe runs a real security review of the live site catching what write-time can't see: exposed admin routes, leaked credentials in shipped JavaScript, source maps in production, dependency drift. Findings chain back into the write-time loop so the AI sees post-deploy issues while editing. What you get: attack chains with the exact remediation code, not "maybe consider." False positives stay near zero. Setup takes 30 seconds. Free until we catch your first real medium-or-above bug. Solo $14.99 · Startup $49.99 · Business $149.99/mo.
Screenshots
Reviews (0)
No reviews yet. Be the first to rate this product!
Comments (0)
No comments yet. Be the first to share your thoughts!