ScanMySaaS
Security checks for websites and public GitHub repos
Details
- Categories
- Use Cases
- Target Audience
- Pricing
- Freemium from $29
- Platforms
Discovery signals
How AI and people discover ScanMySaaS on PeerPush
About ScanMySaaS
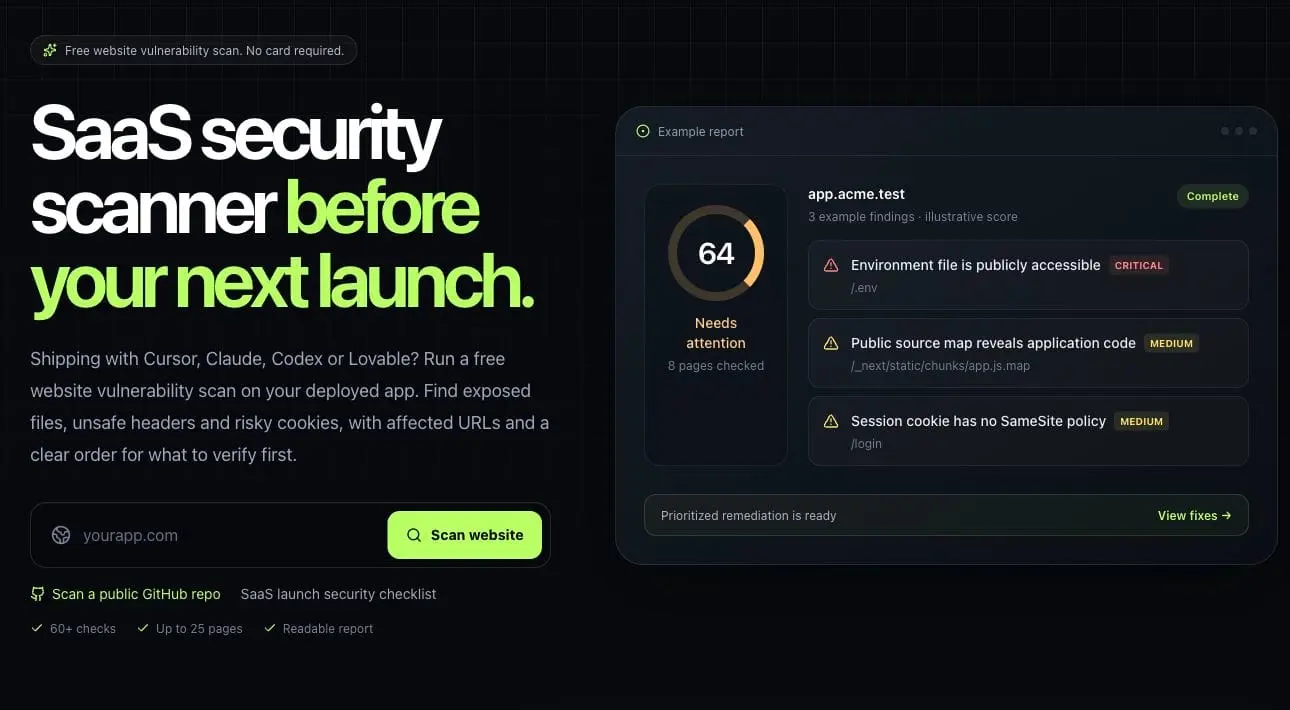
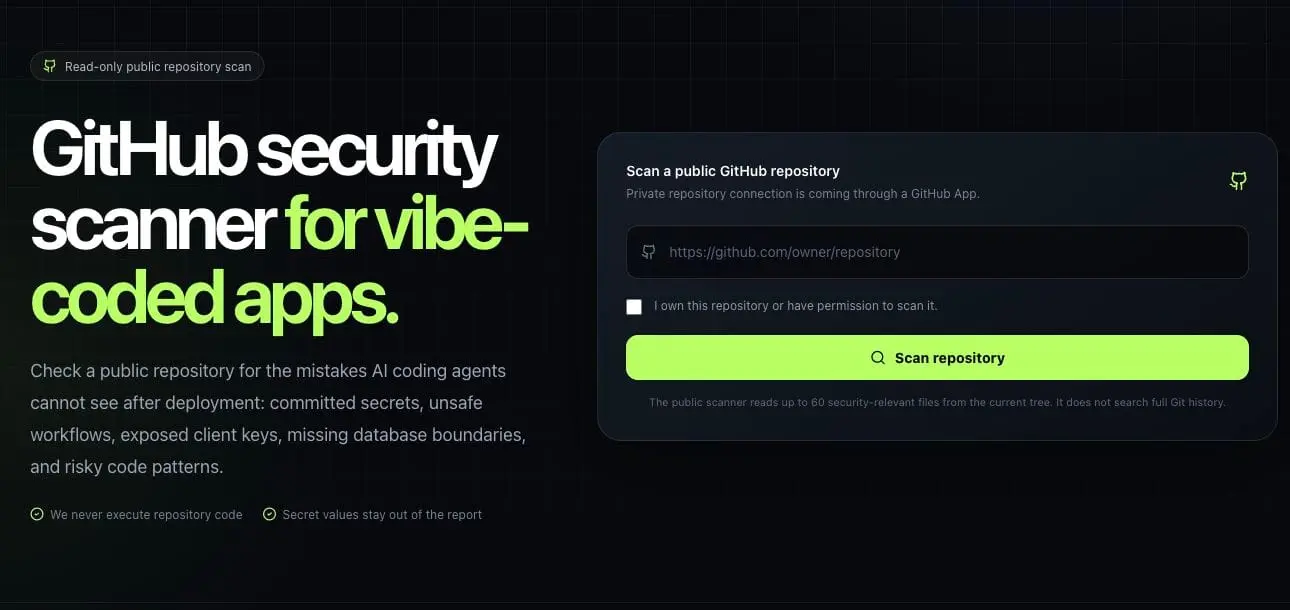
ScanMySaaS helps SaaS founders and small product teams spot security risks before and after launch. Enter a public website URL you own or are authorized to test to check up to 25 reachable pages and review findings by severity and affected URL. The public GitHub repository scanner checks committed secret patterns, risky GitHub Actions, exposed client keys, Supabase configuration signals and unsafe code patterns. It reads a bounded set of public files without running repository code. Findings can become technical fix prompts for Cursor, Claude, Codex or another coding agent. Your first website scan is free, with no credit card. Paid plans start at $29/month and add detailed remediation plus credits for checking new releases. Automated findings need verification; a public scan does not test logged-in business logic or certify an app as secure.
Screenshots
Reviews (0)
No reviews yet. Be the first to rate this product!
Comments (1)
I built ScanMySaaS for founders shipping with AI coding tools. Try your first website scan free and tell me which findings help, what is unclear, and what would make verifying a fix easier.