SteelSuit
Scan your site for exposed secrets, bad TLS & weak headers

Details
- Target Audience
- DevelopersIndie HackersAgencies
- Pricing
- Freemium from $9.99
- Alternatives
- Vibe App Scanner alternatives

Discovery signals
How AI and people discover SteelSuit on PeerPush
- ChatGPT
- Perplexity
- Claude
- +4 other AI crawlers
Reads by these AI engines
Crawlers behind these engines read this listing on PeerPush.About SteelSuit
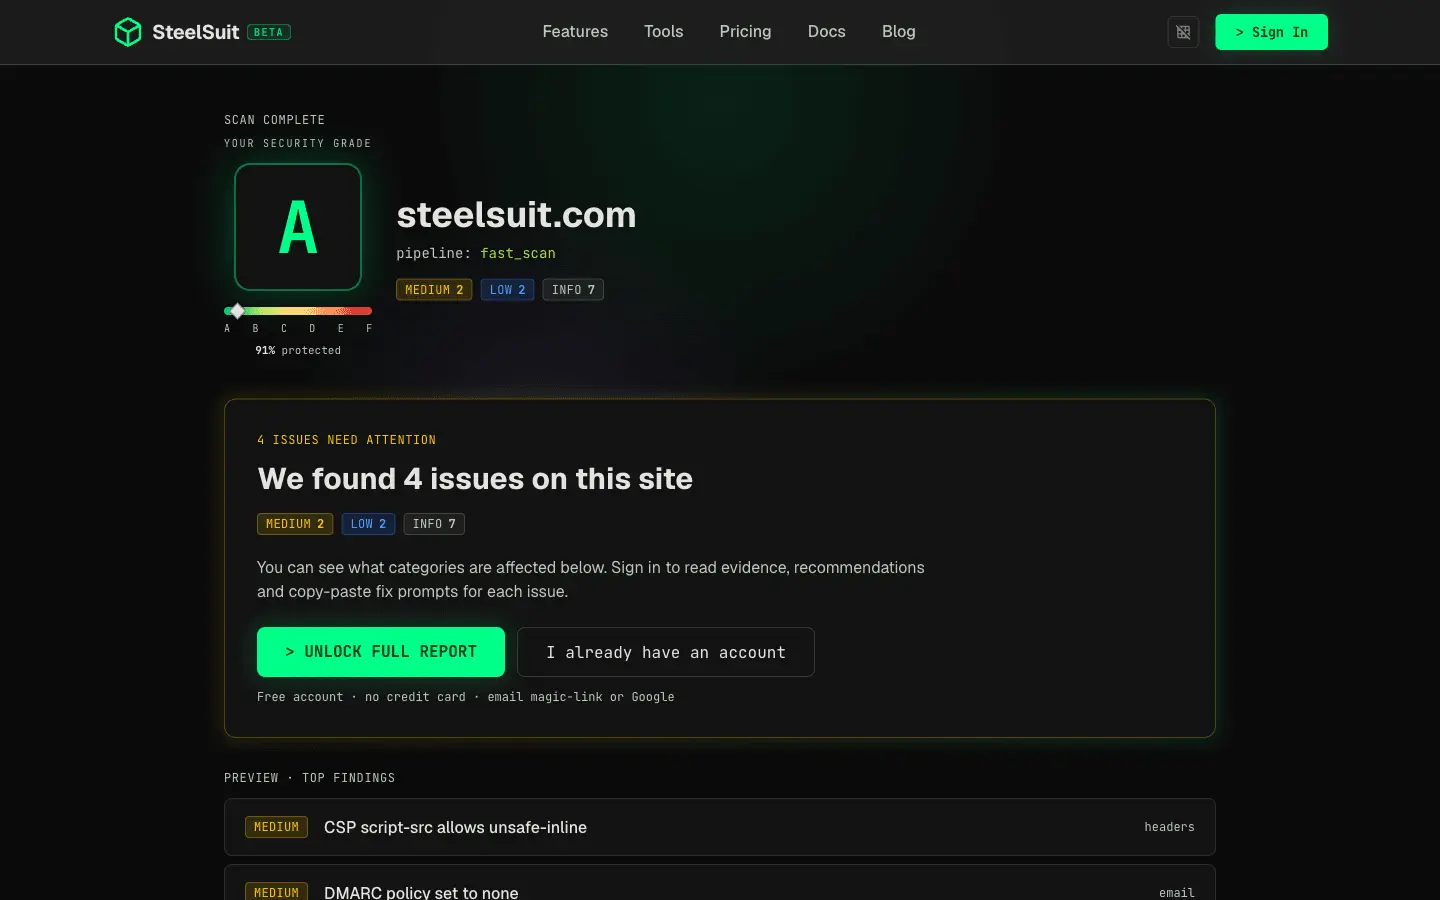
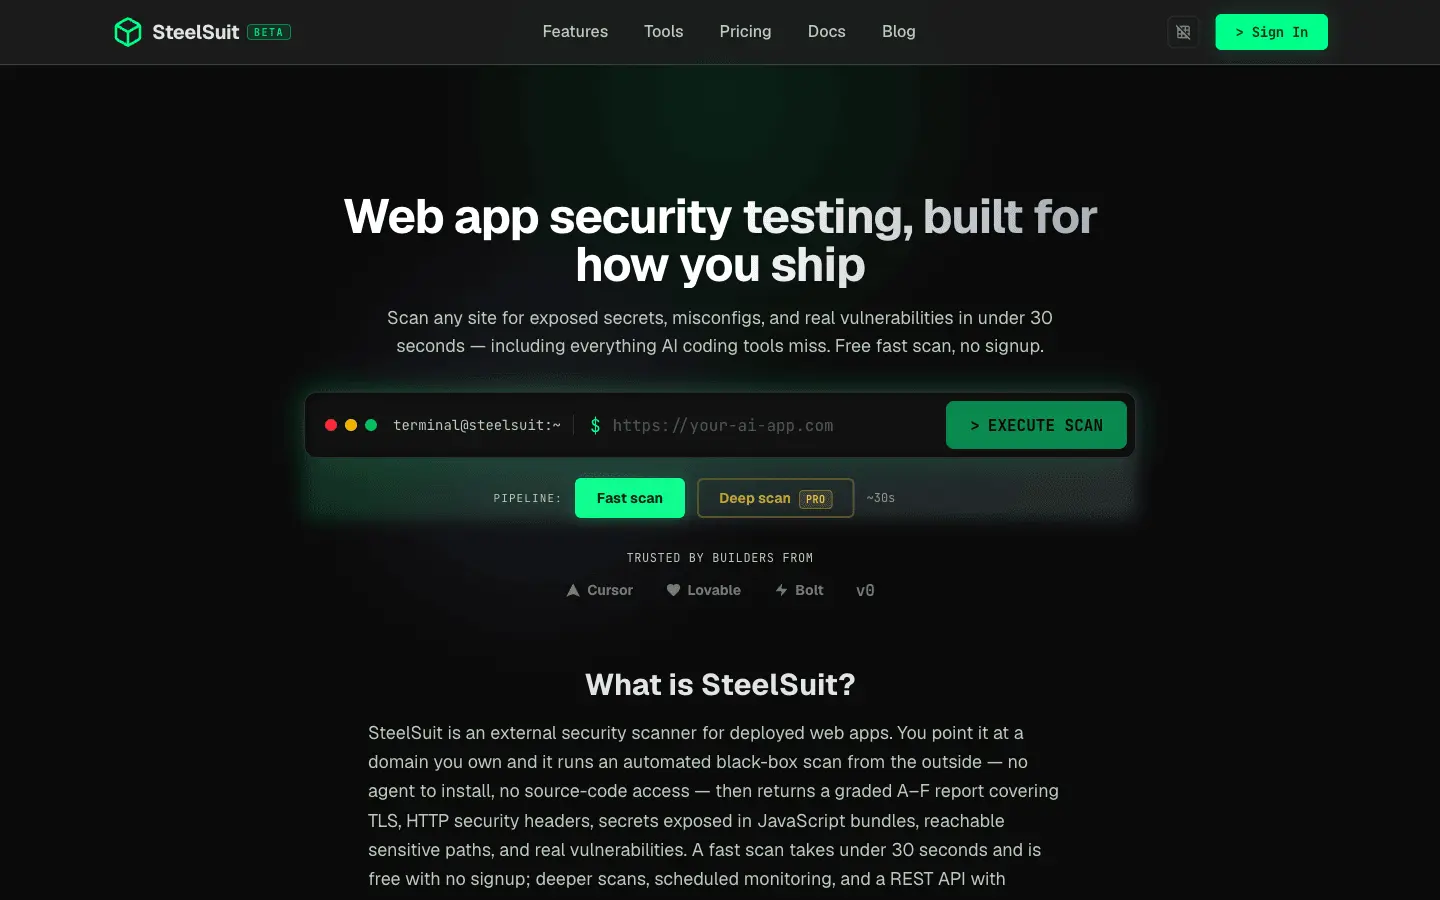
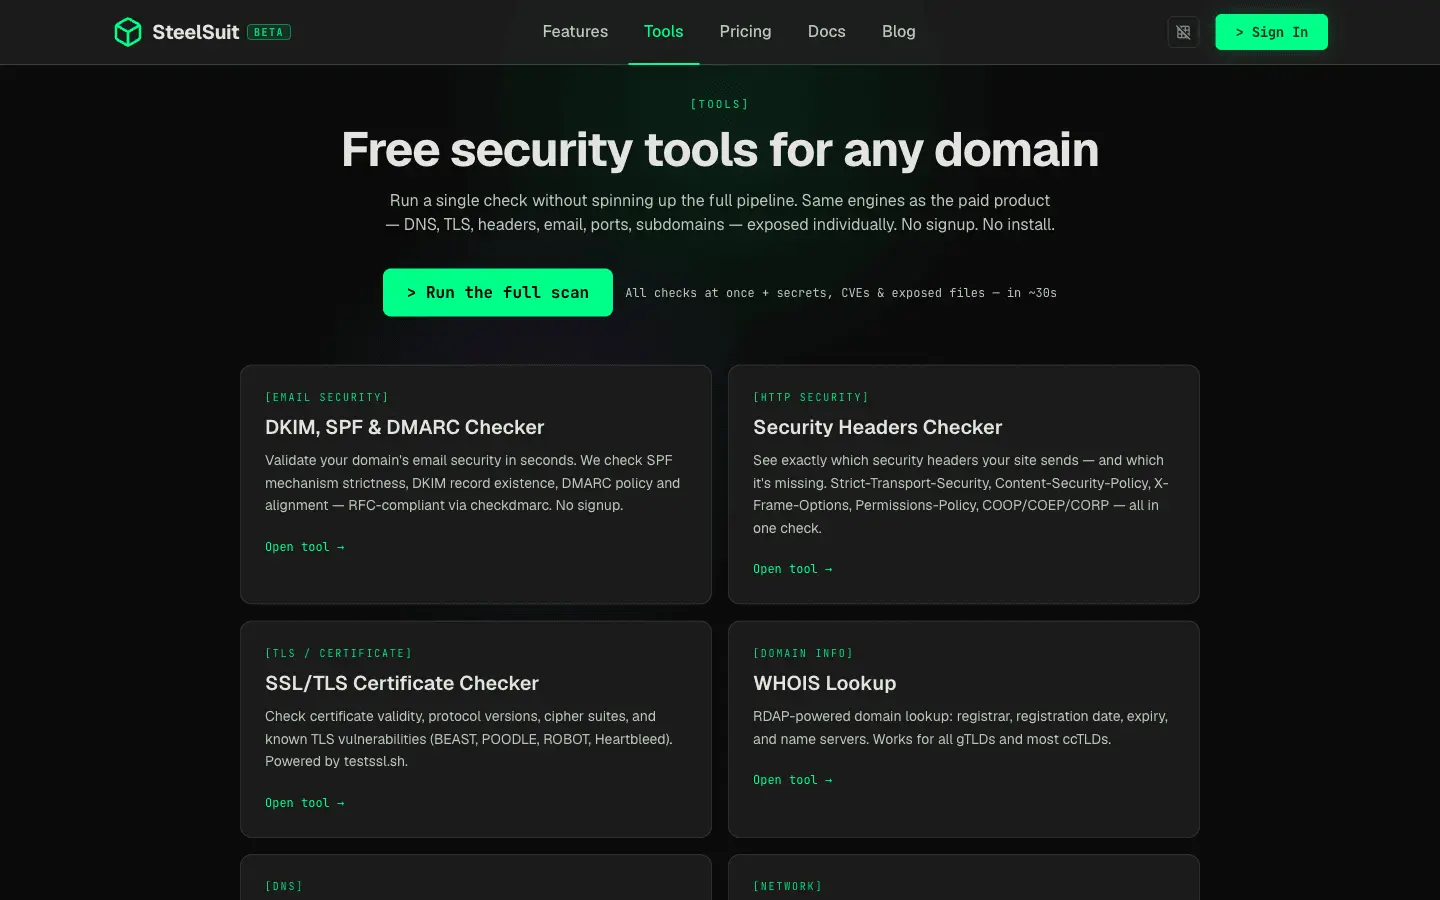
SteelSuit is an external web security scanner built for the people shipping sites without a security team — indie founders, freelancers, agencies, and developers building on AI tools like Cursor, Lovable, Bolt and v0. Point it at a domain you own and it looks at your site the way an attacker would, from the outside: no code access, no installed agent, no repo — just the domain. Under one scan it runs a professional toolchain — port and service detection, Nuclei's 4000+ CVE/misconfig templates, testssl.sh for TLS, subdomain enumeration with takeover detection, content discovery, and JavaScript-bundle secret detection — then aggregates and de-duplicates everything into a single A–F report instead of a wall of raw tool output. What you get: - An A–F security grade with an executive summary and the top issues up front - TLS/SSL, security-header and CSP analysis, with exact misconfigurations called out - Exposed-secret detection in JS bundles (we detect patterns — we never test your keys against the provider) - Subdomain enumeration + takeover detection, content discovery, and Wayback exposure (what the archive leaked: old .git, dev domains, backups) - Email posture — SPF, DKIM, DMARC, BIMI — RFC-correct - Stack-specific fix snippets: not "your CSP is weak" but the exact block to paste into next.config.js, your Cloudflare rules, or nginx - Compliance mapping to PCI DSS 4.0, ISO 27001:2022 and GDPR on every finding - A PDF deliverable, JSON/LLM-ready export (each finding ships a fix_prompt for Cursor/Claude/ChatGPT), continuous monitoring with diff alerts (webhook/email/Slack/Telegram), and a REST API for your CI/CD - Free single-purpose tools: email (SPF/DKIM/DMARC), SSL, headers, CORS, subdomain, port, DNS, WHOIS How it's different: deeper than the cheap single-purpose scanners (it's not just an SSL test or a header checker — it's all of them plus CVEs, subdomains and secrets in one report), and a fraction of the price and friction of the enterprise platforms (Detectify, Probely, Intruder). It is external and read-only — browser-equivalent traffic, no exploitation, no DoS, no credential testing. The more thorough deep scan is gated behind a DNS ownership check, so you can only run it against domains you control. Free tier with no credit card; paid plans from $9.99/mo. You only scan domains you own or are authorized to assess.
Screenshots
Reviews (0)
No reviews yet. Be the first to rate this product!
Comments (1)
SteelSuit is the scan I wanted for my own sites: one A–F report instead of SSL Labs + SecurityHeaders + MXToolbox in three tabs. External and read-only — scan domains you own. Free tier, no card.