Zoltra
AI security agent that finds and fixes app vulnerabilities

Details
- Categories
- Target Audience
- Pricing
- Subscription from $80
- Platforms
- Alternatives
 Snyk alternatives
 Aikido alternatives
About Zoltra
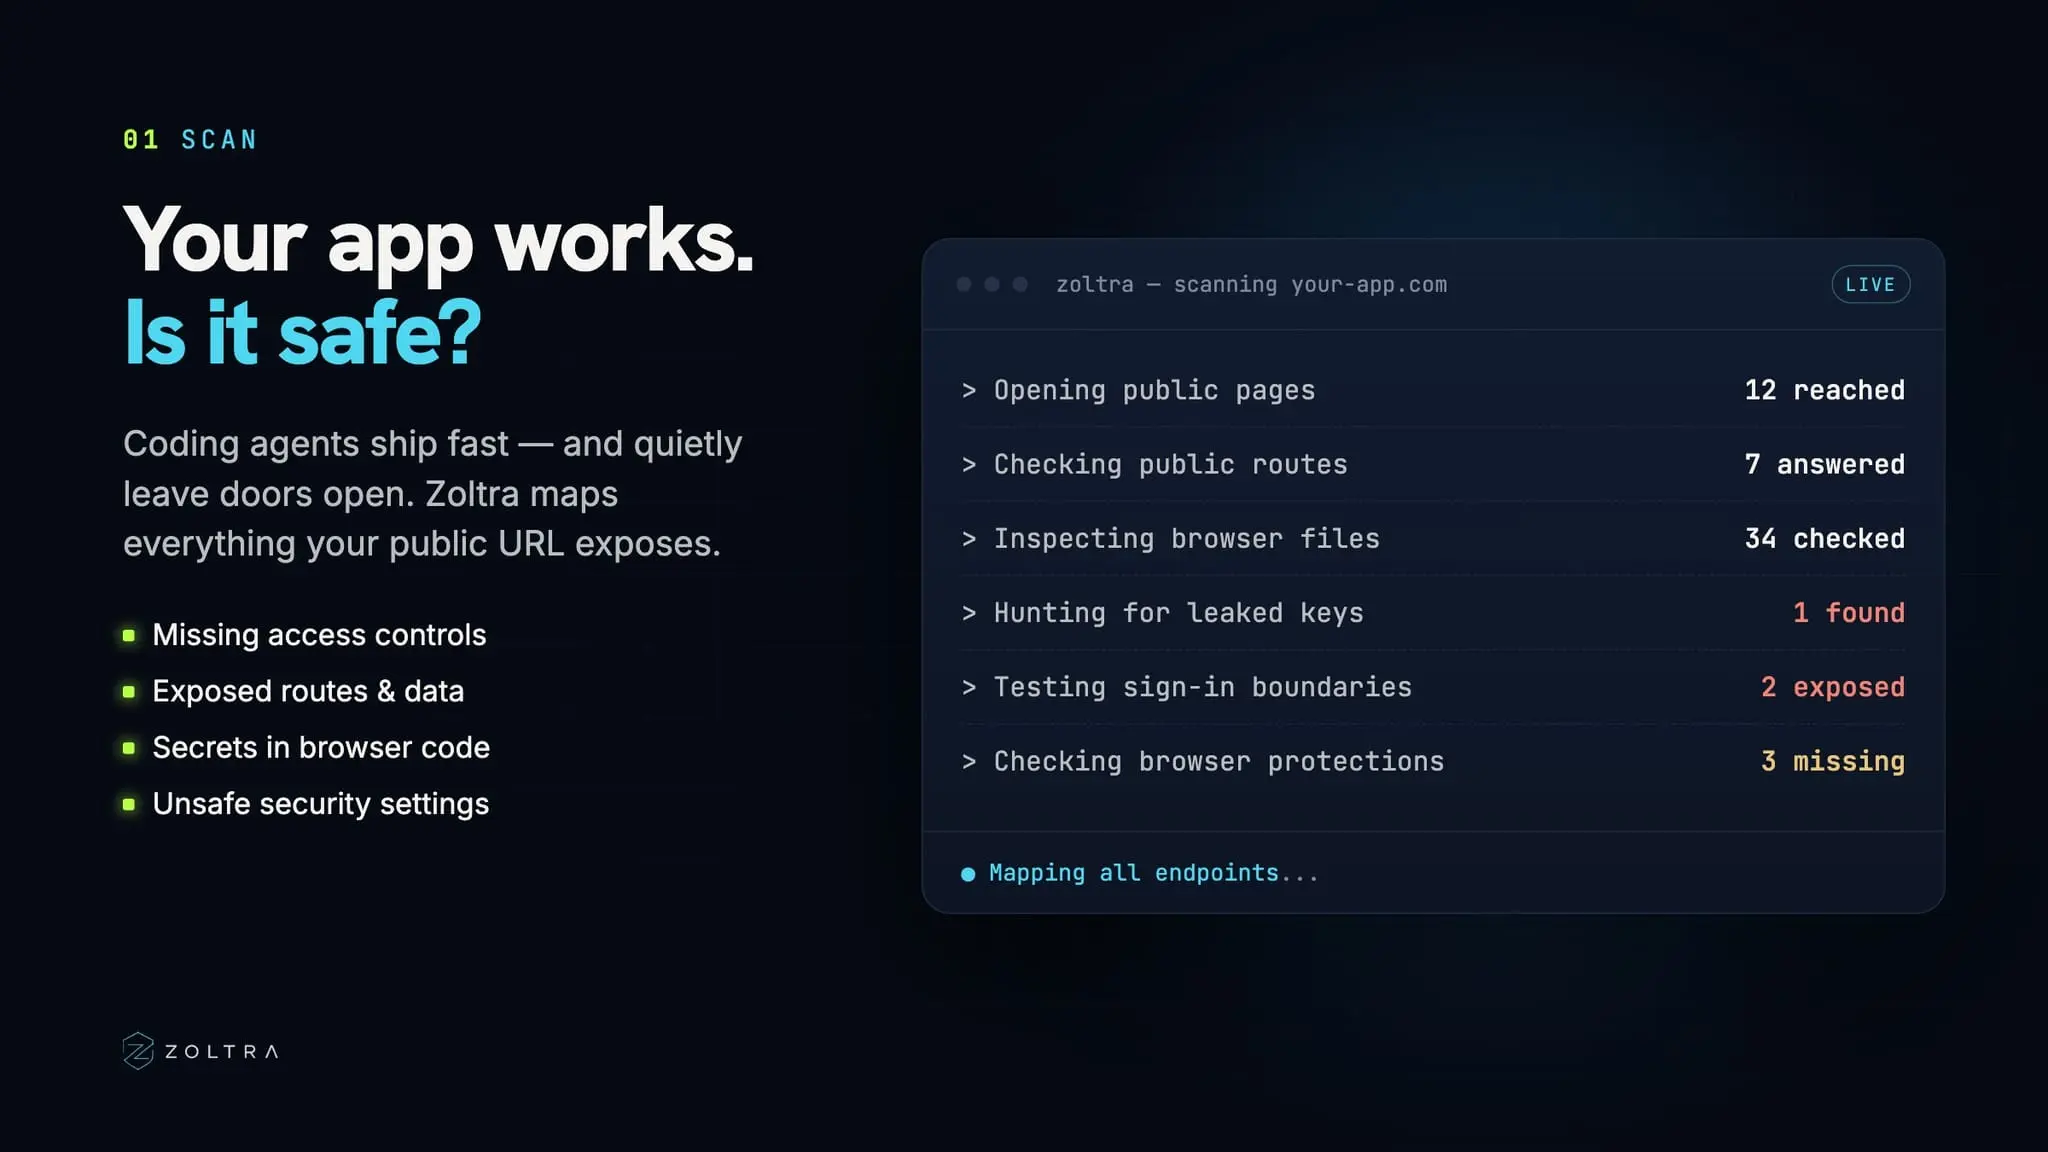
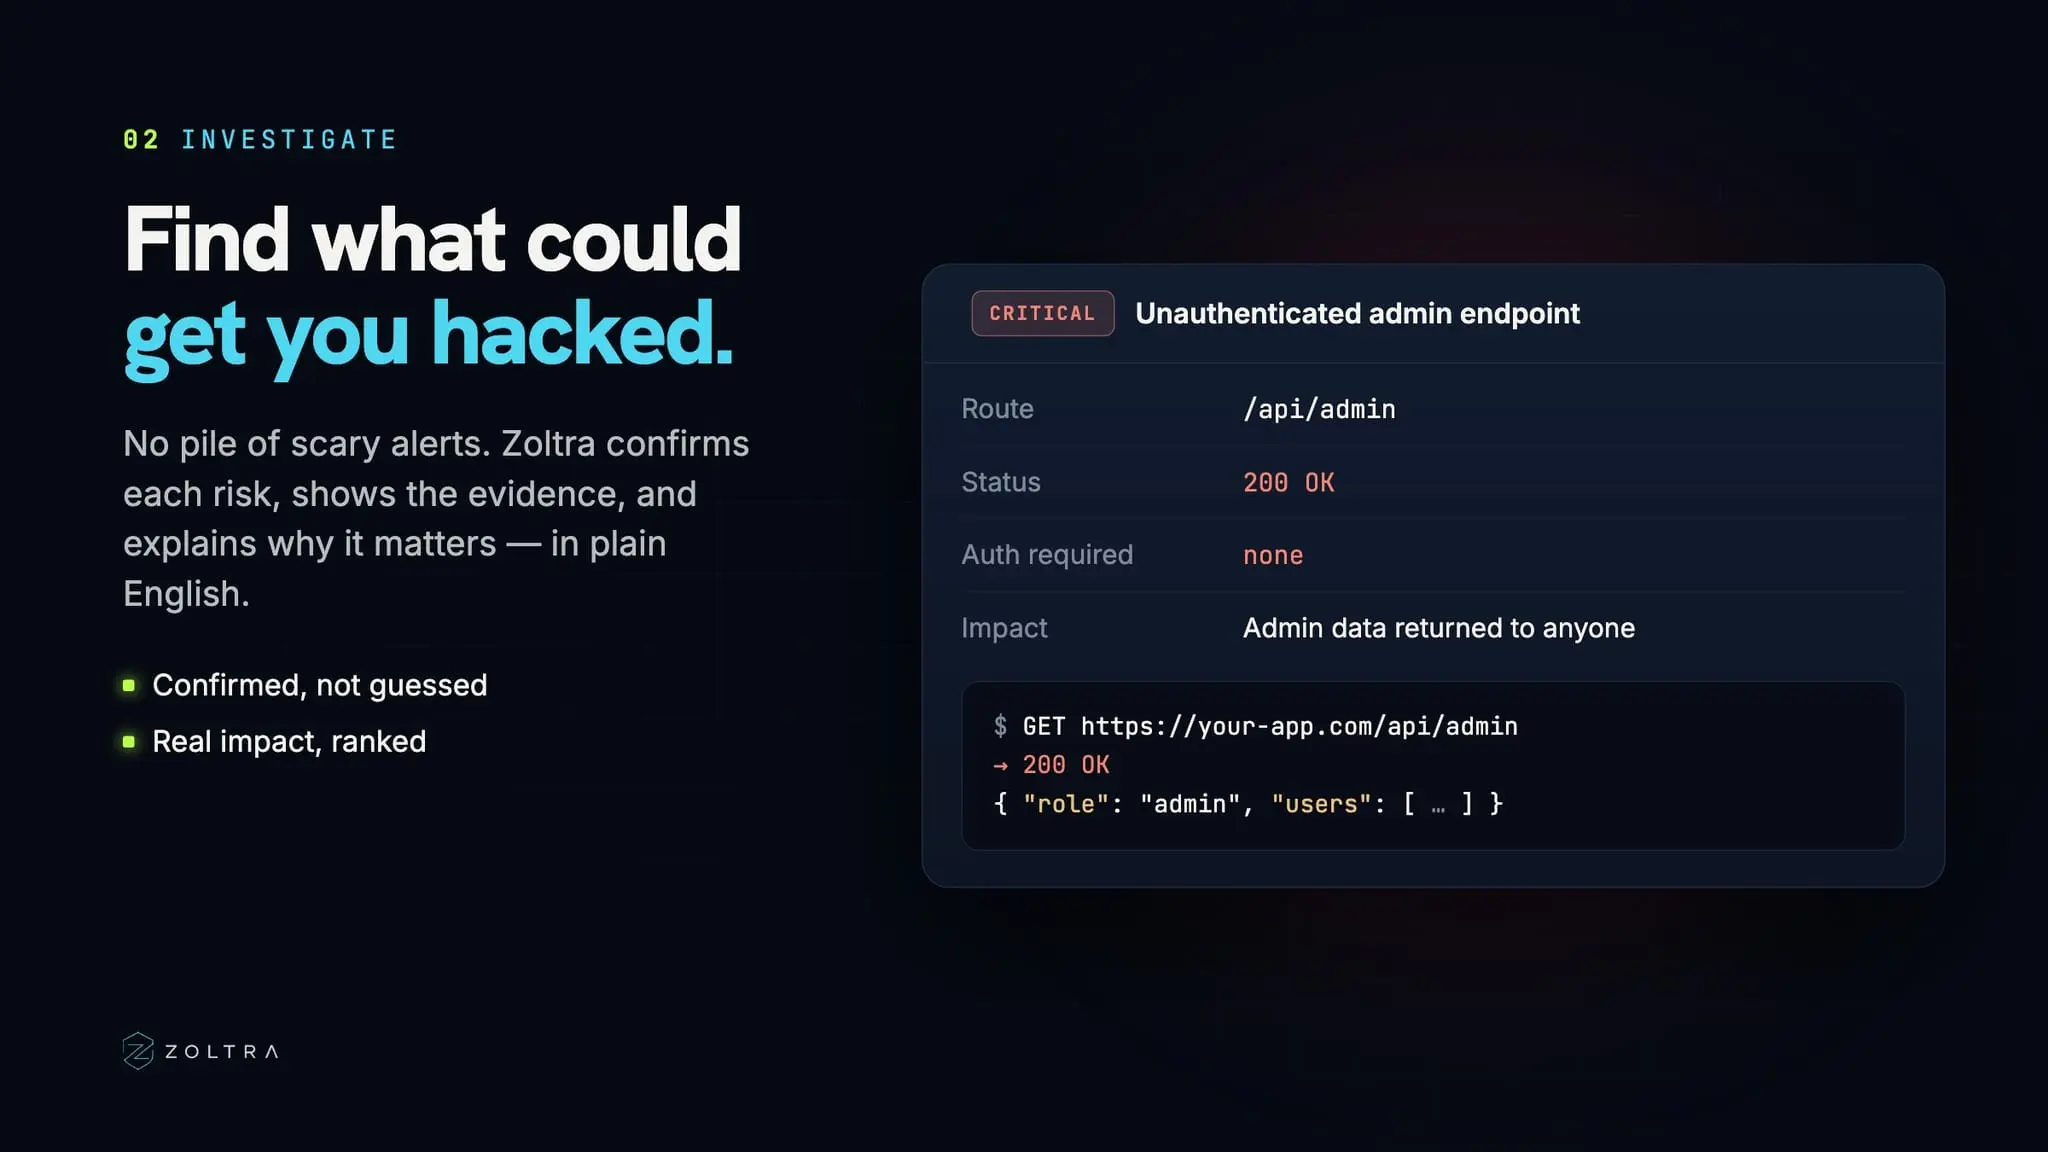
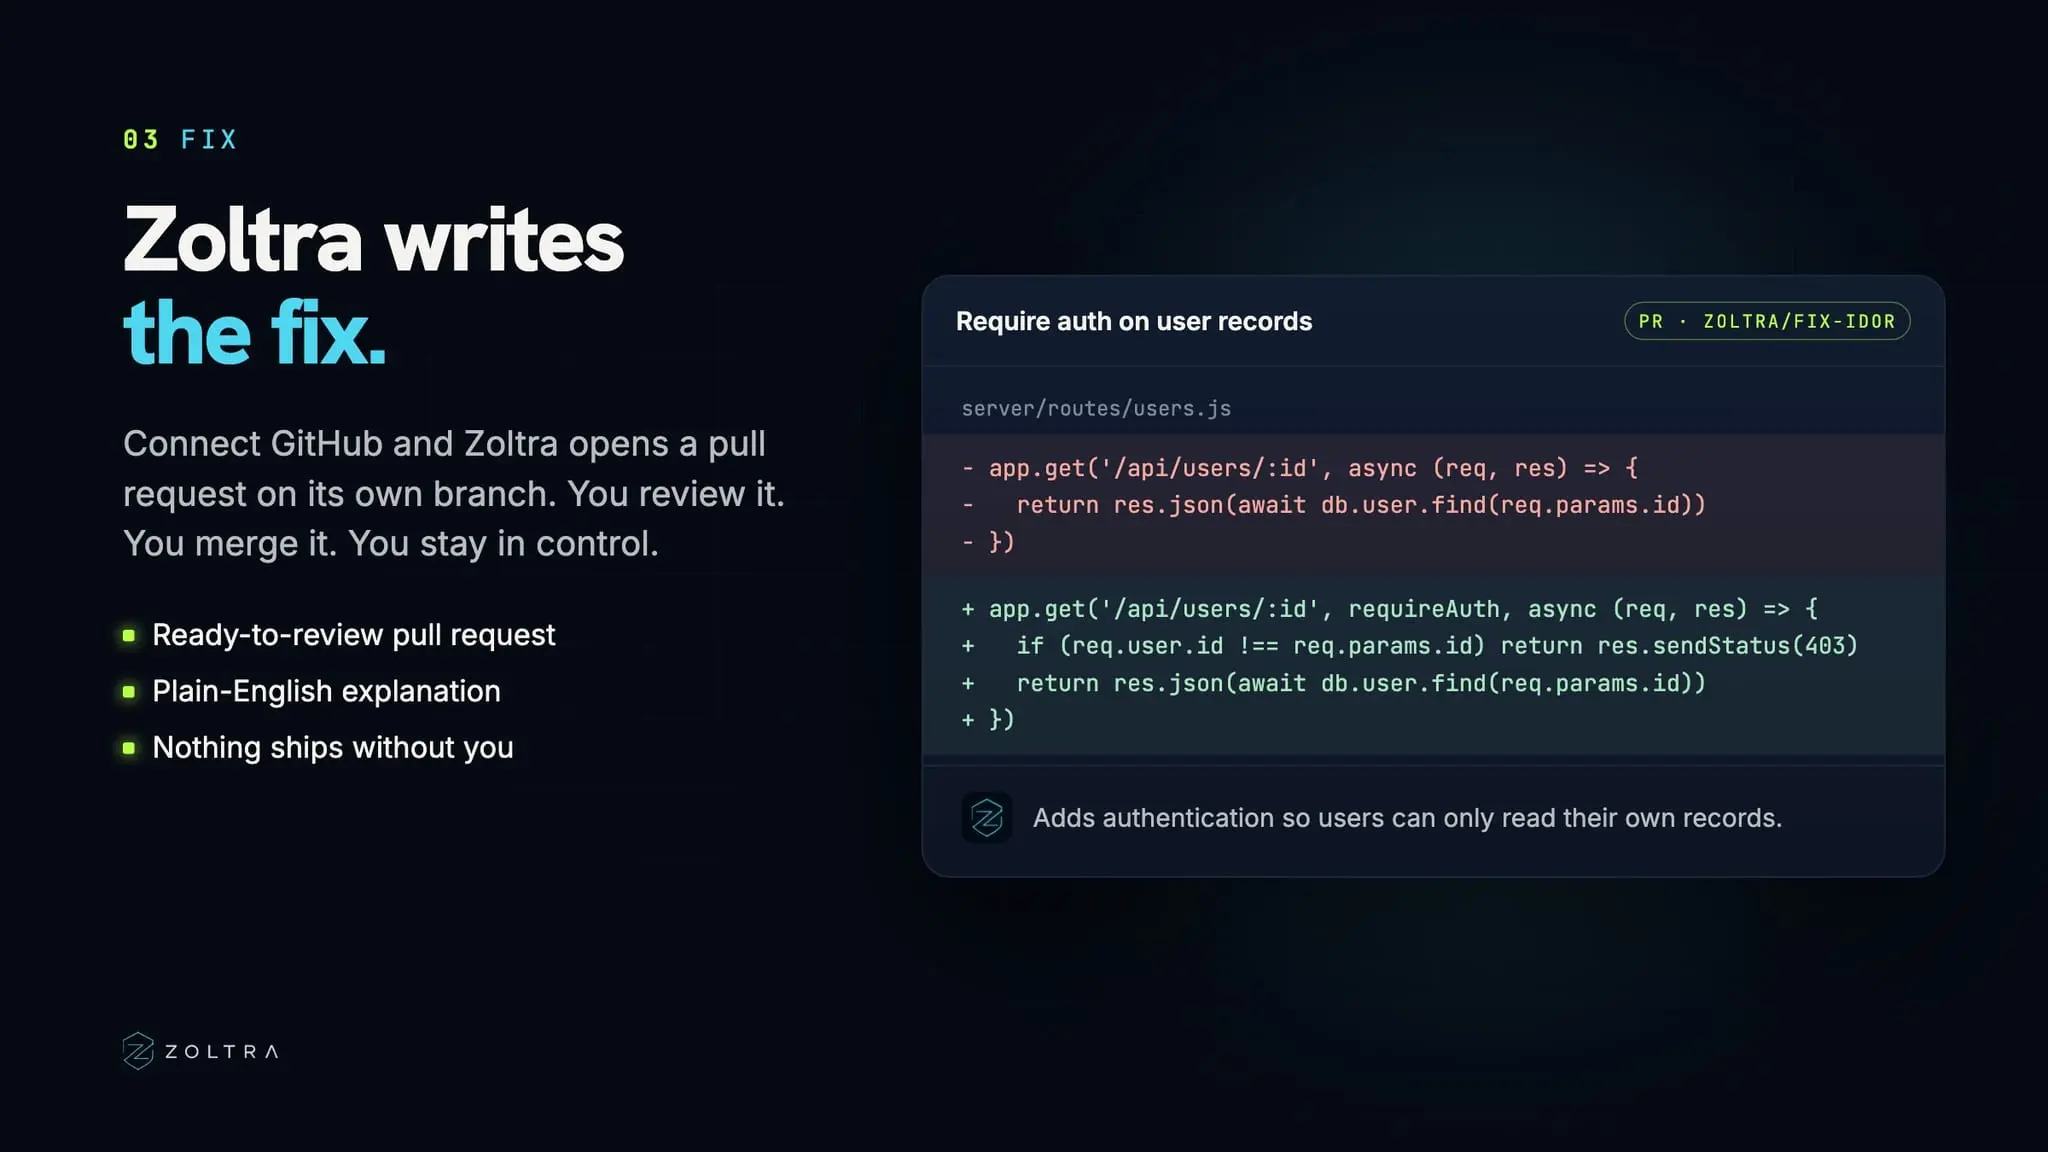
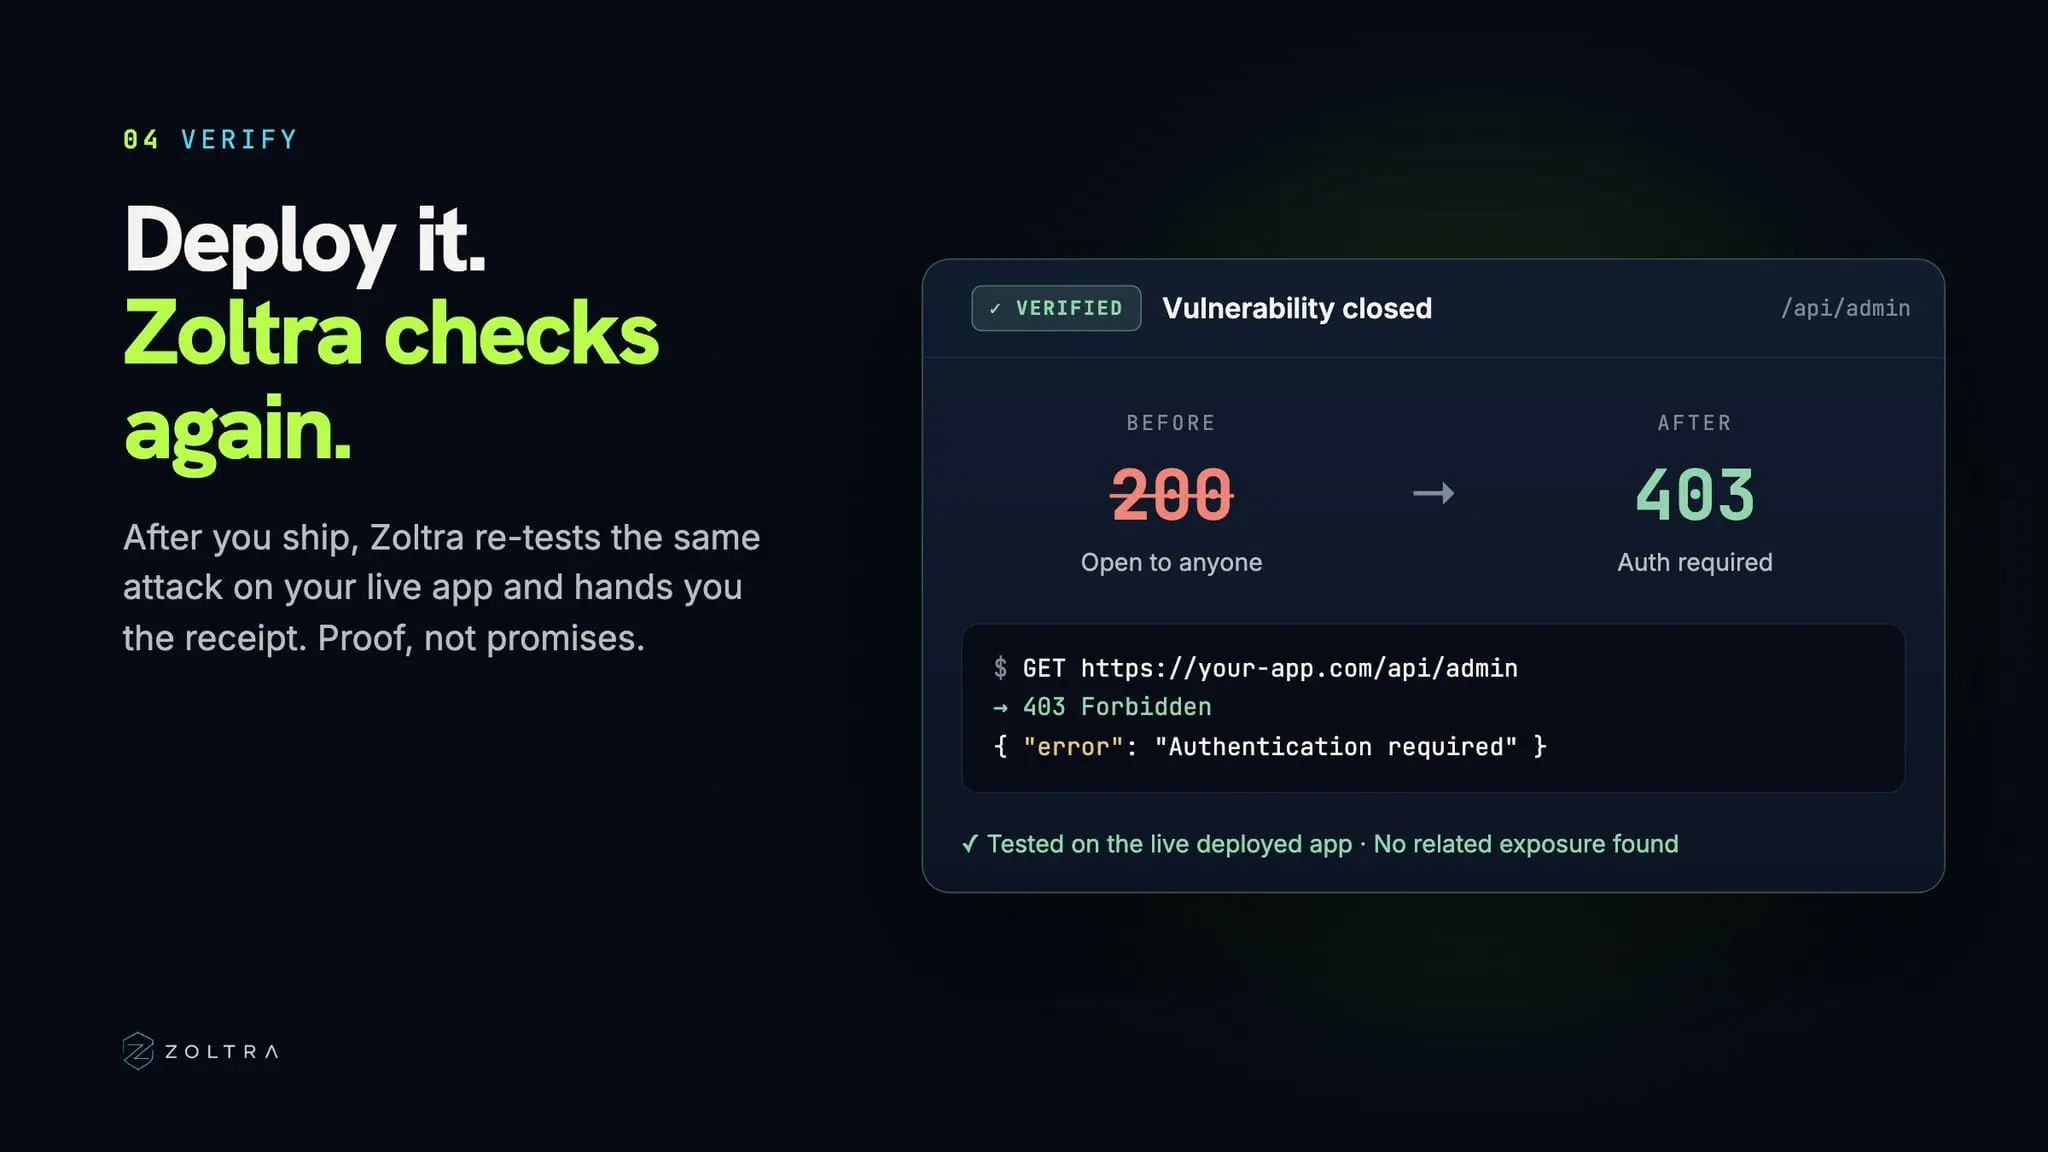
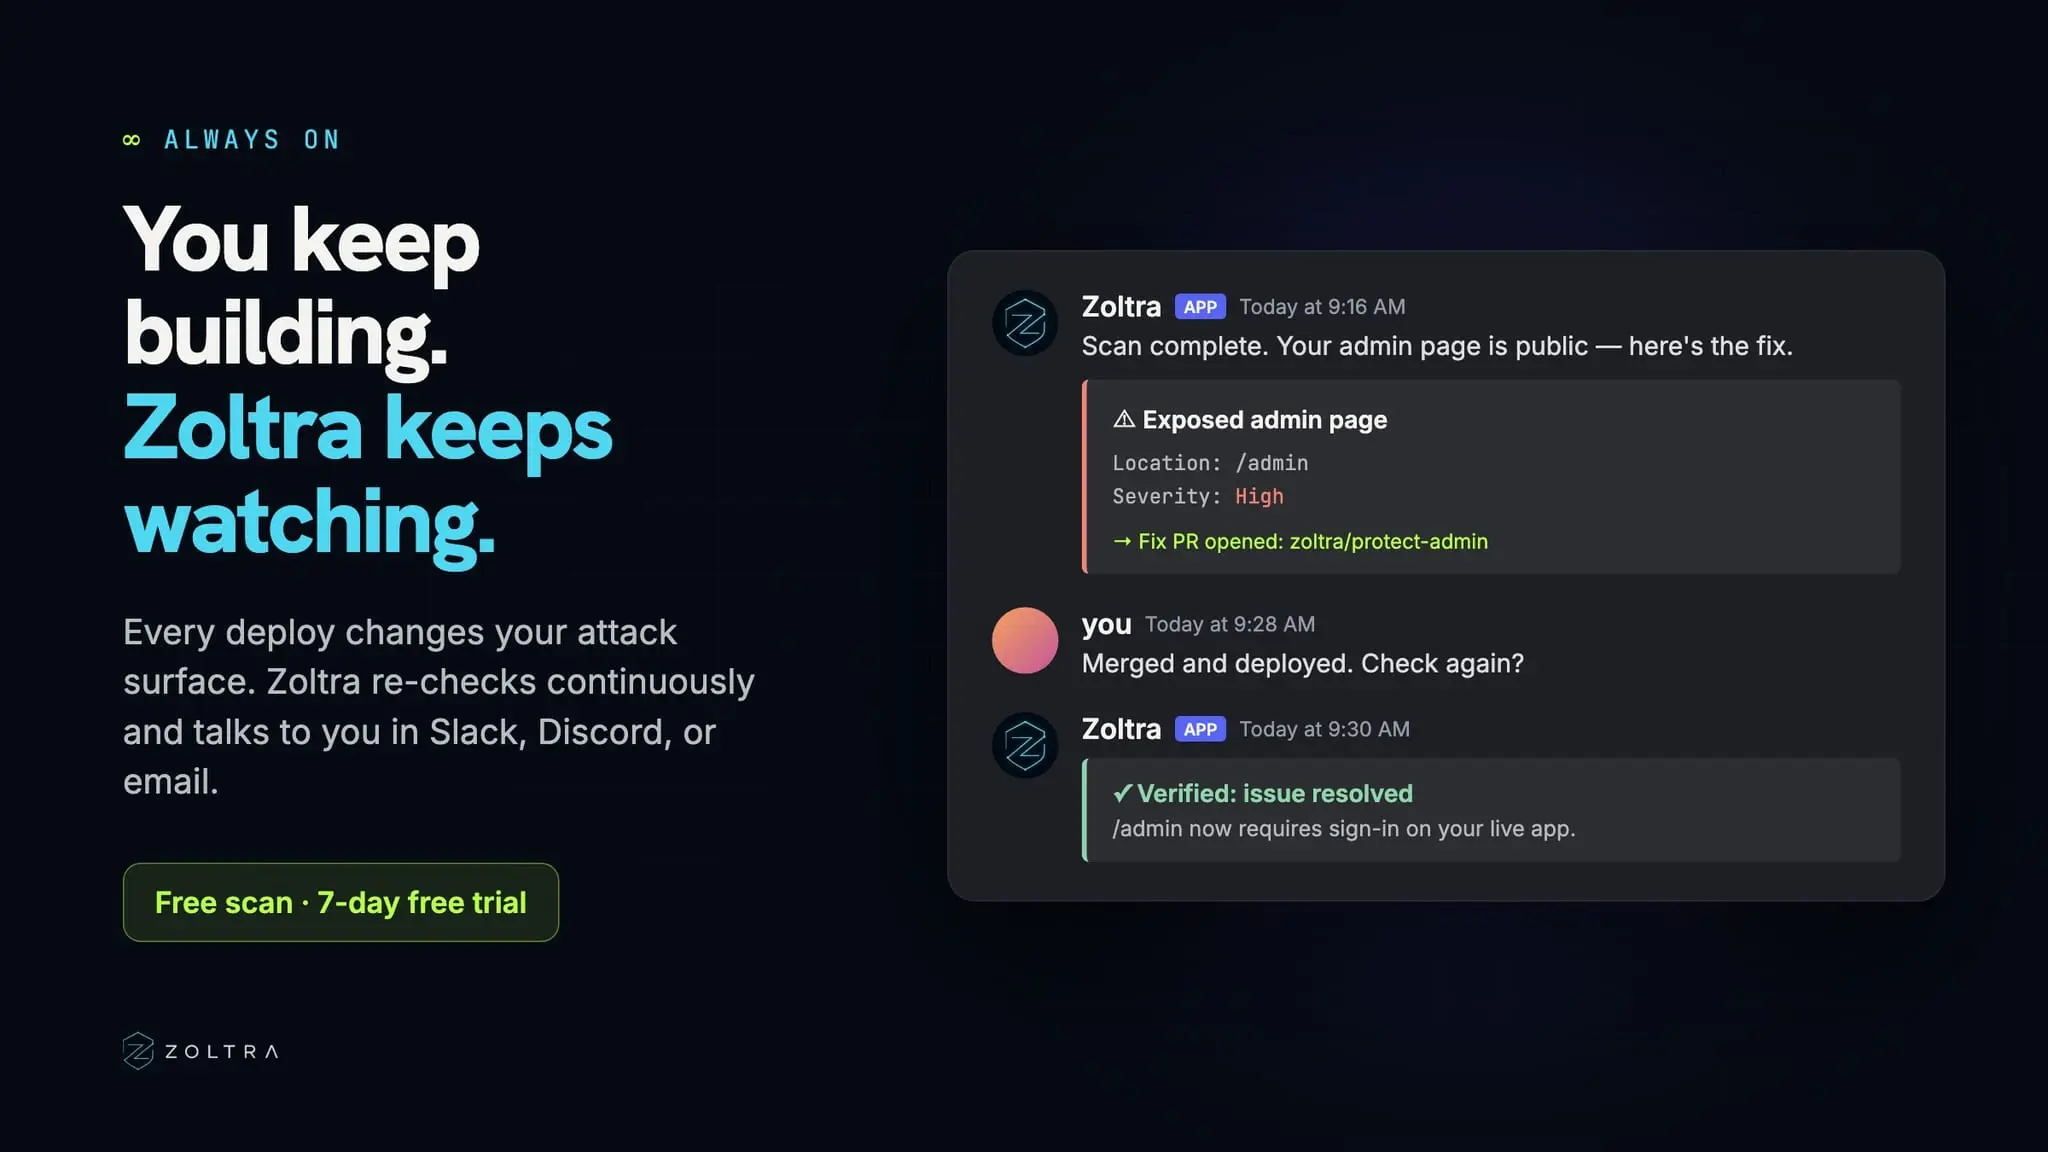
AI built your app. Zoltra secures it. Coding tools like Claude Code, Lovable, Codex, and Cursor made shipping fast. They didn't make it safe. AI-built apps routinely go live with open admin routes, API keys sitting in browser code, missing access checks, and absent security settings, while every feature still looks like it works. Most founders only find out when someone else does. Zoltra is an AI security agent that closes the whole loop for you: 1. Scan: Give Zoltra your live URL. It maps everything your public app exposes: pages, routes, API endpoints, browser files, sign-in boundaries, and security settings. 2. Investigate: No pile of 200 scary alerts. Zoltra confirms each risk, shows the evidence (the actual request and response), and explains in plain English why it matters and what to fix first. 3. Fix: Connect GitHub and Zoltra prepares the repair as a pull request on a separate branch, with a clear explanation. You review it, merge it, and deploy on your terms. Nothing ships without you. 4. Verify: After you deploy, Zoltra re-tests the same issue against your live app and hands you the receipt. Before: 200 OK, open to anyone. After: 403, sign-in required. Proof, not promises. Then it keeps watching. Every new feature changes your attack surface, so Zoltra keeps checking and talks to you where you already work: Slack, Discord, or email, plus a weekly security summary for your team. WHAT ZOLTRA CATCHES - Missing access controls and unauthenticated endpoints - Exposed admin pages, routes, and private data - API keys and secrets leaked into browser code - Unsafe security settings and missing browser protections WHO IT'S FOR - Vibecoders and solo founders shipping AI-built apps without a security team - Indie hackers on Next.js, Vercel, Supabase, and similar stacks - AI-agent builders whose products hold credentials or call tools - Small studios that need a plain-English security handoff for client apps WHY ZOLTRA IS DIFFERENT Most scanners stop at a report and leave you to decode it. Zoltra investigates, writes the fix, and verifies it on your live app. The full loop, not just the alert. Deep scans run only on domains you own and verify. PRICING Start with a free scan of your live URL. The full plan is 7 days free, then $80/month.
Discount Codes
$20 OFF(-25% OFF)
Valid until Oct 16, 2031
Product Video
Watch a video demo of Zoltra.
Screenshots
Reviews (0)
No reviews yet. Be the first to rate this product!
Comments (1)
Hey PeerPush. I built Zoltra because AI tools let us ship in a weekend but leave vulnerabilities by default. Drop your live URL for a free scan, the holes they left open will surprise you.