Kubiieo Security Report
Multi-account AWS security posture assessments
Details
- Follow on
- Categories
- Use Cases
- Target Audience
- Pricing
- Freemium from $35
- Platforms
- Featured in
- Alternatives
 Vanta alternatives
 Aikido alternatives
Discovery signals
How AI and people discover Kubiieo Security Report on PeerPush
About Kubiieo Security Report
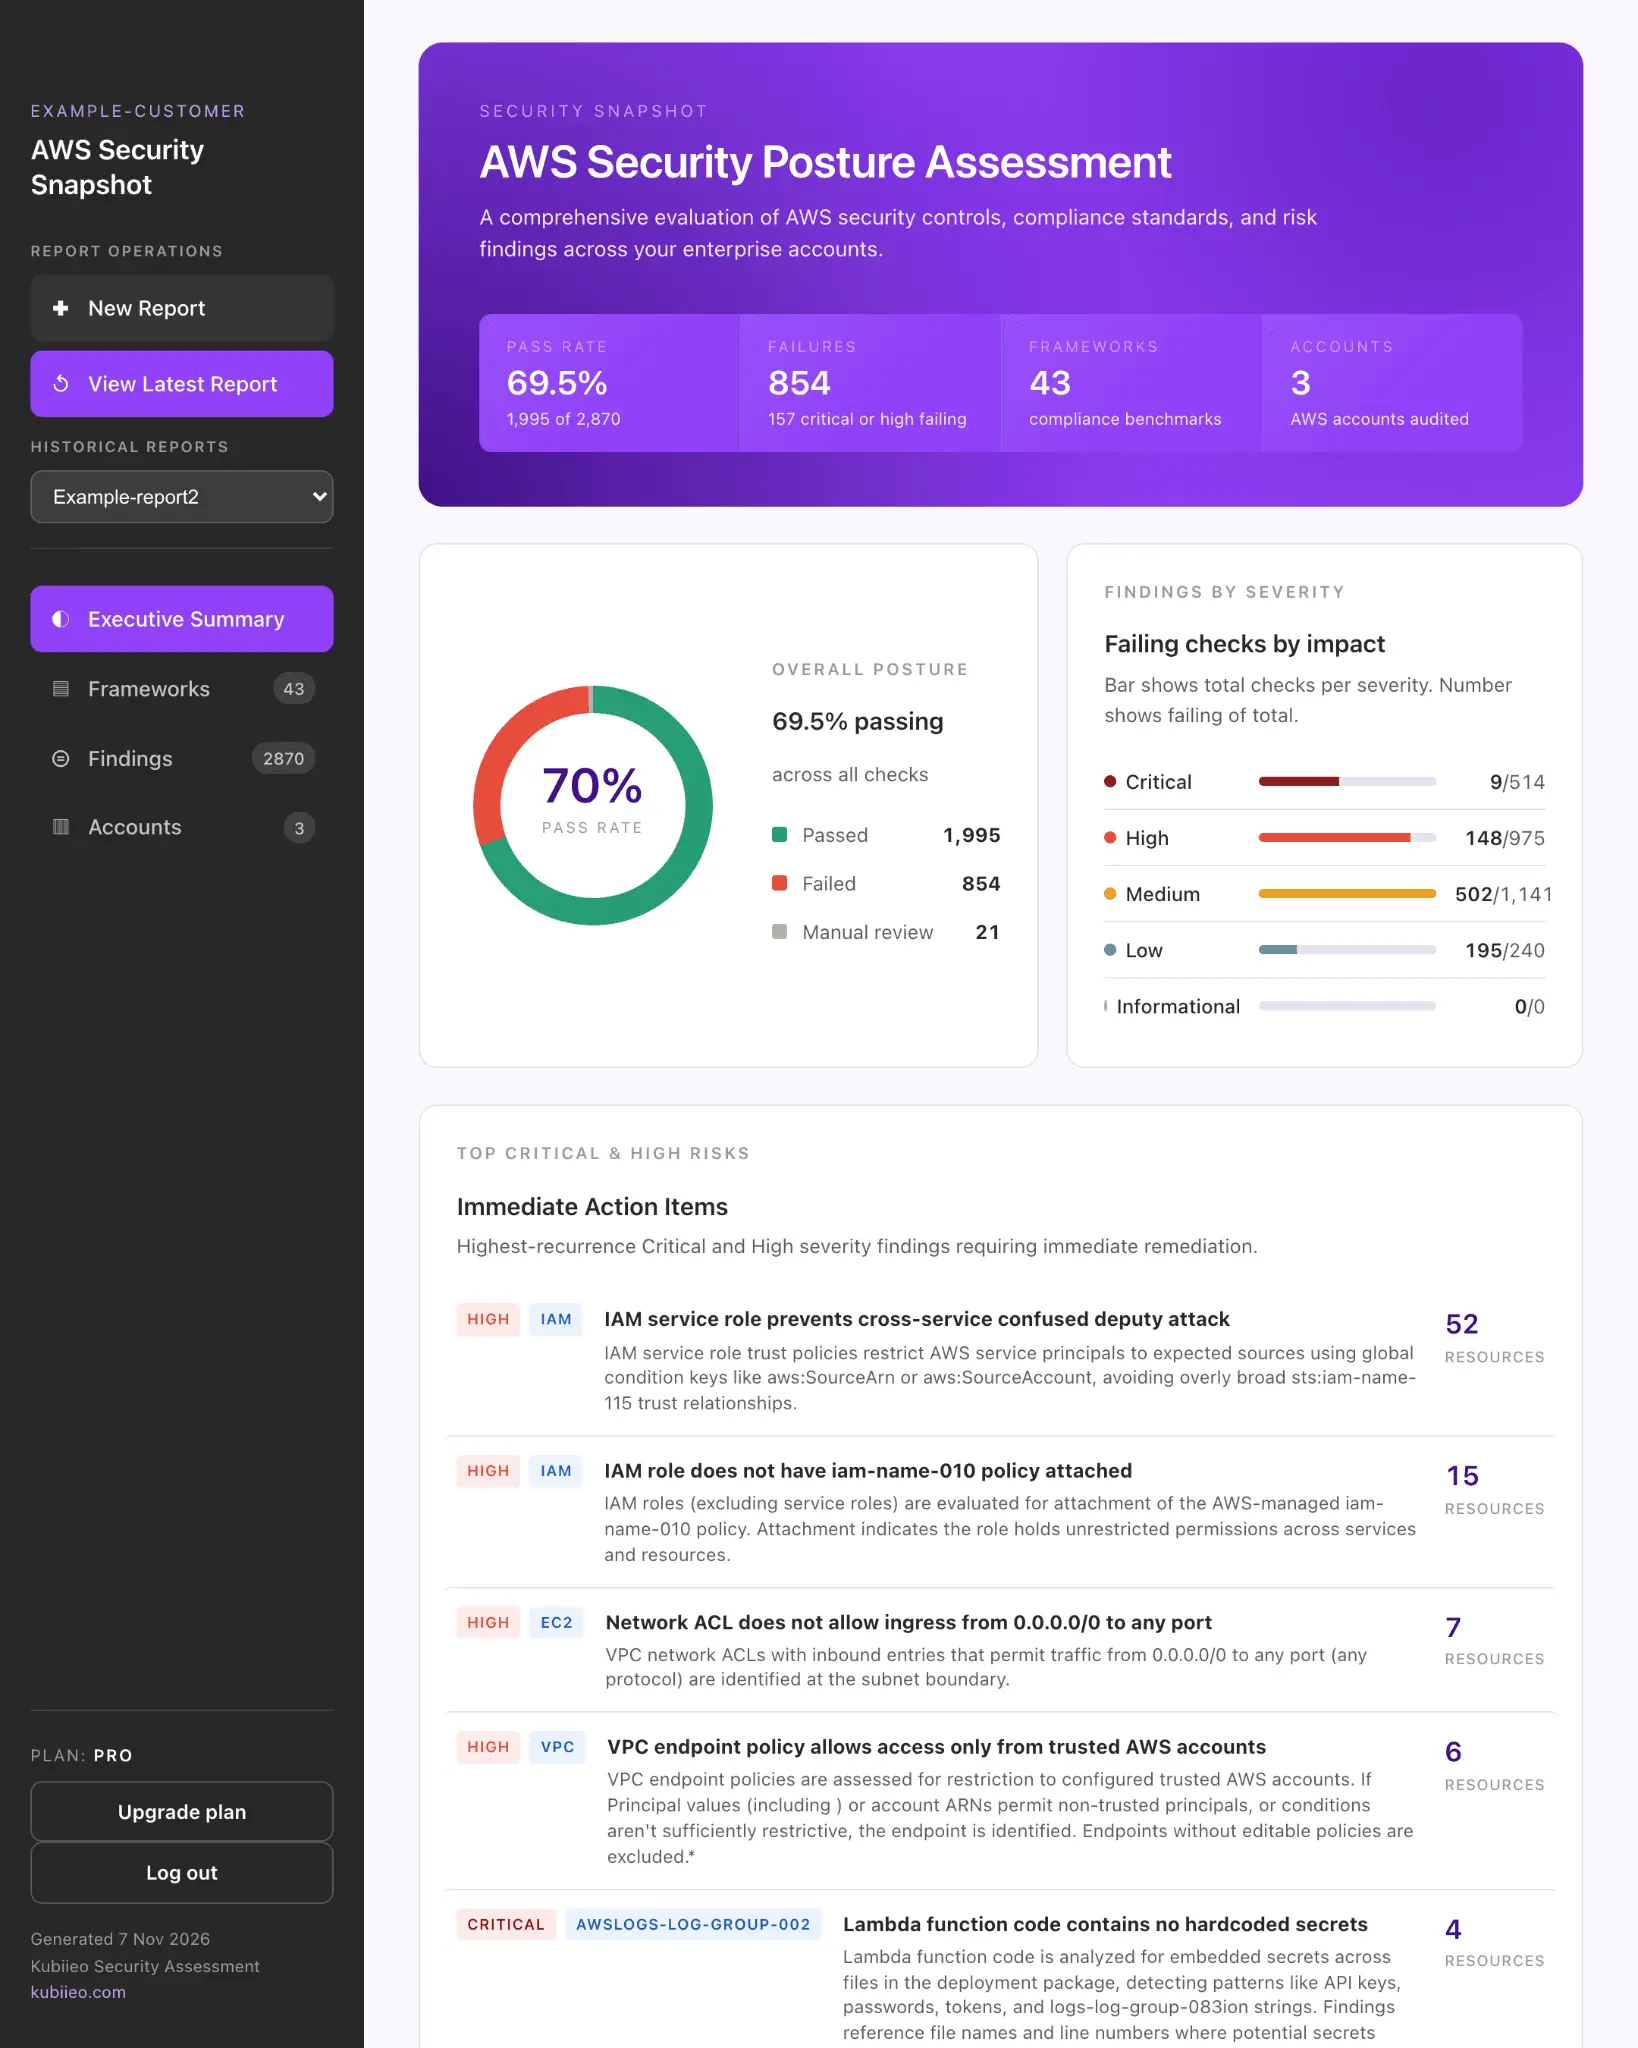
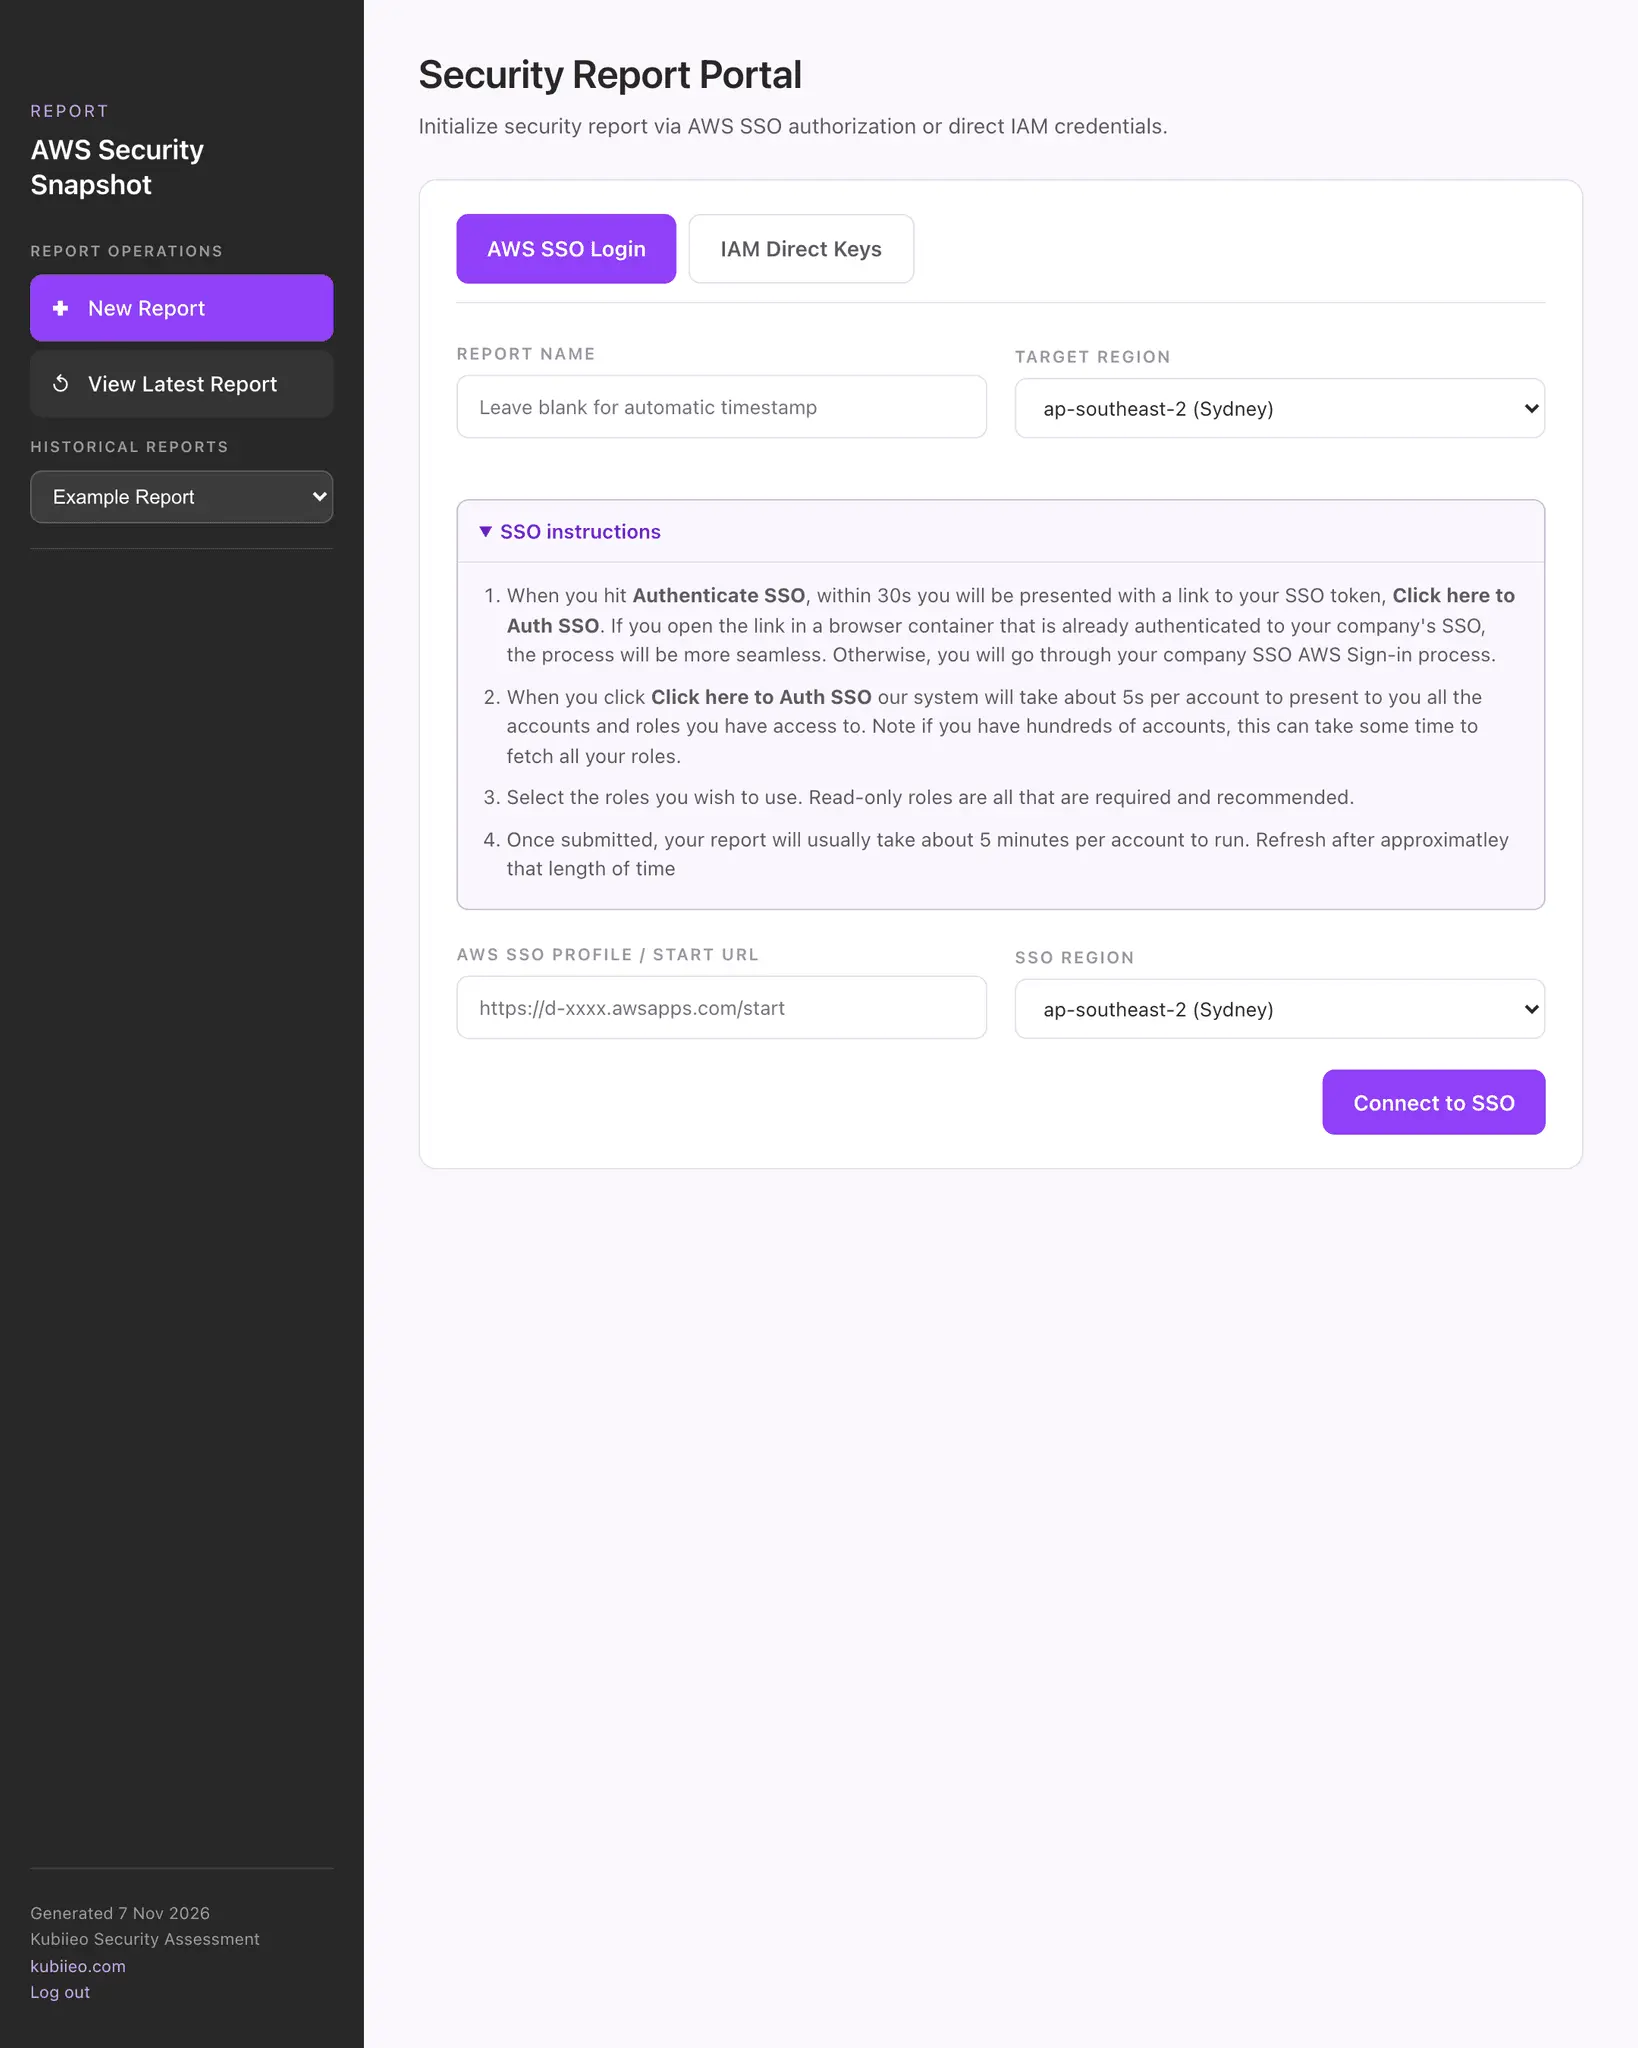
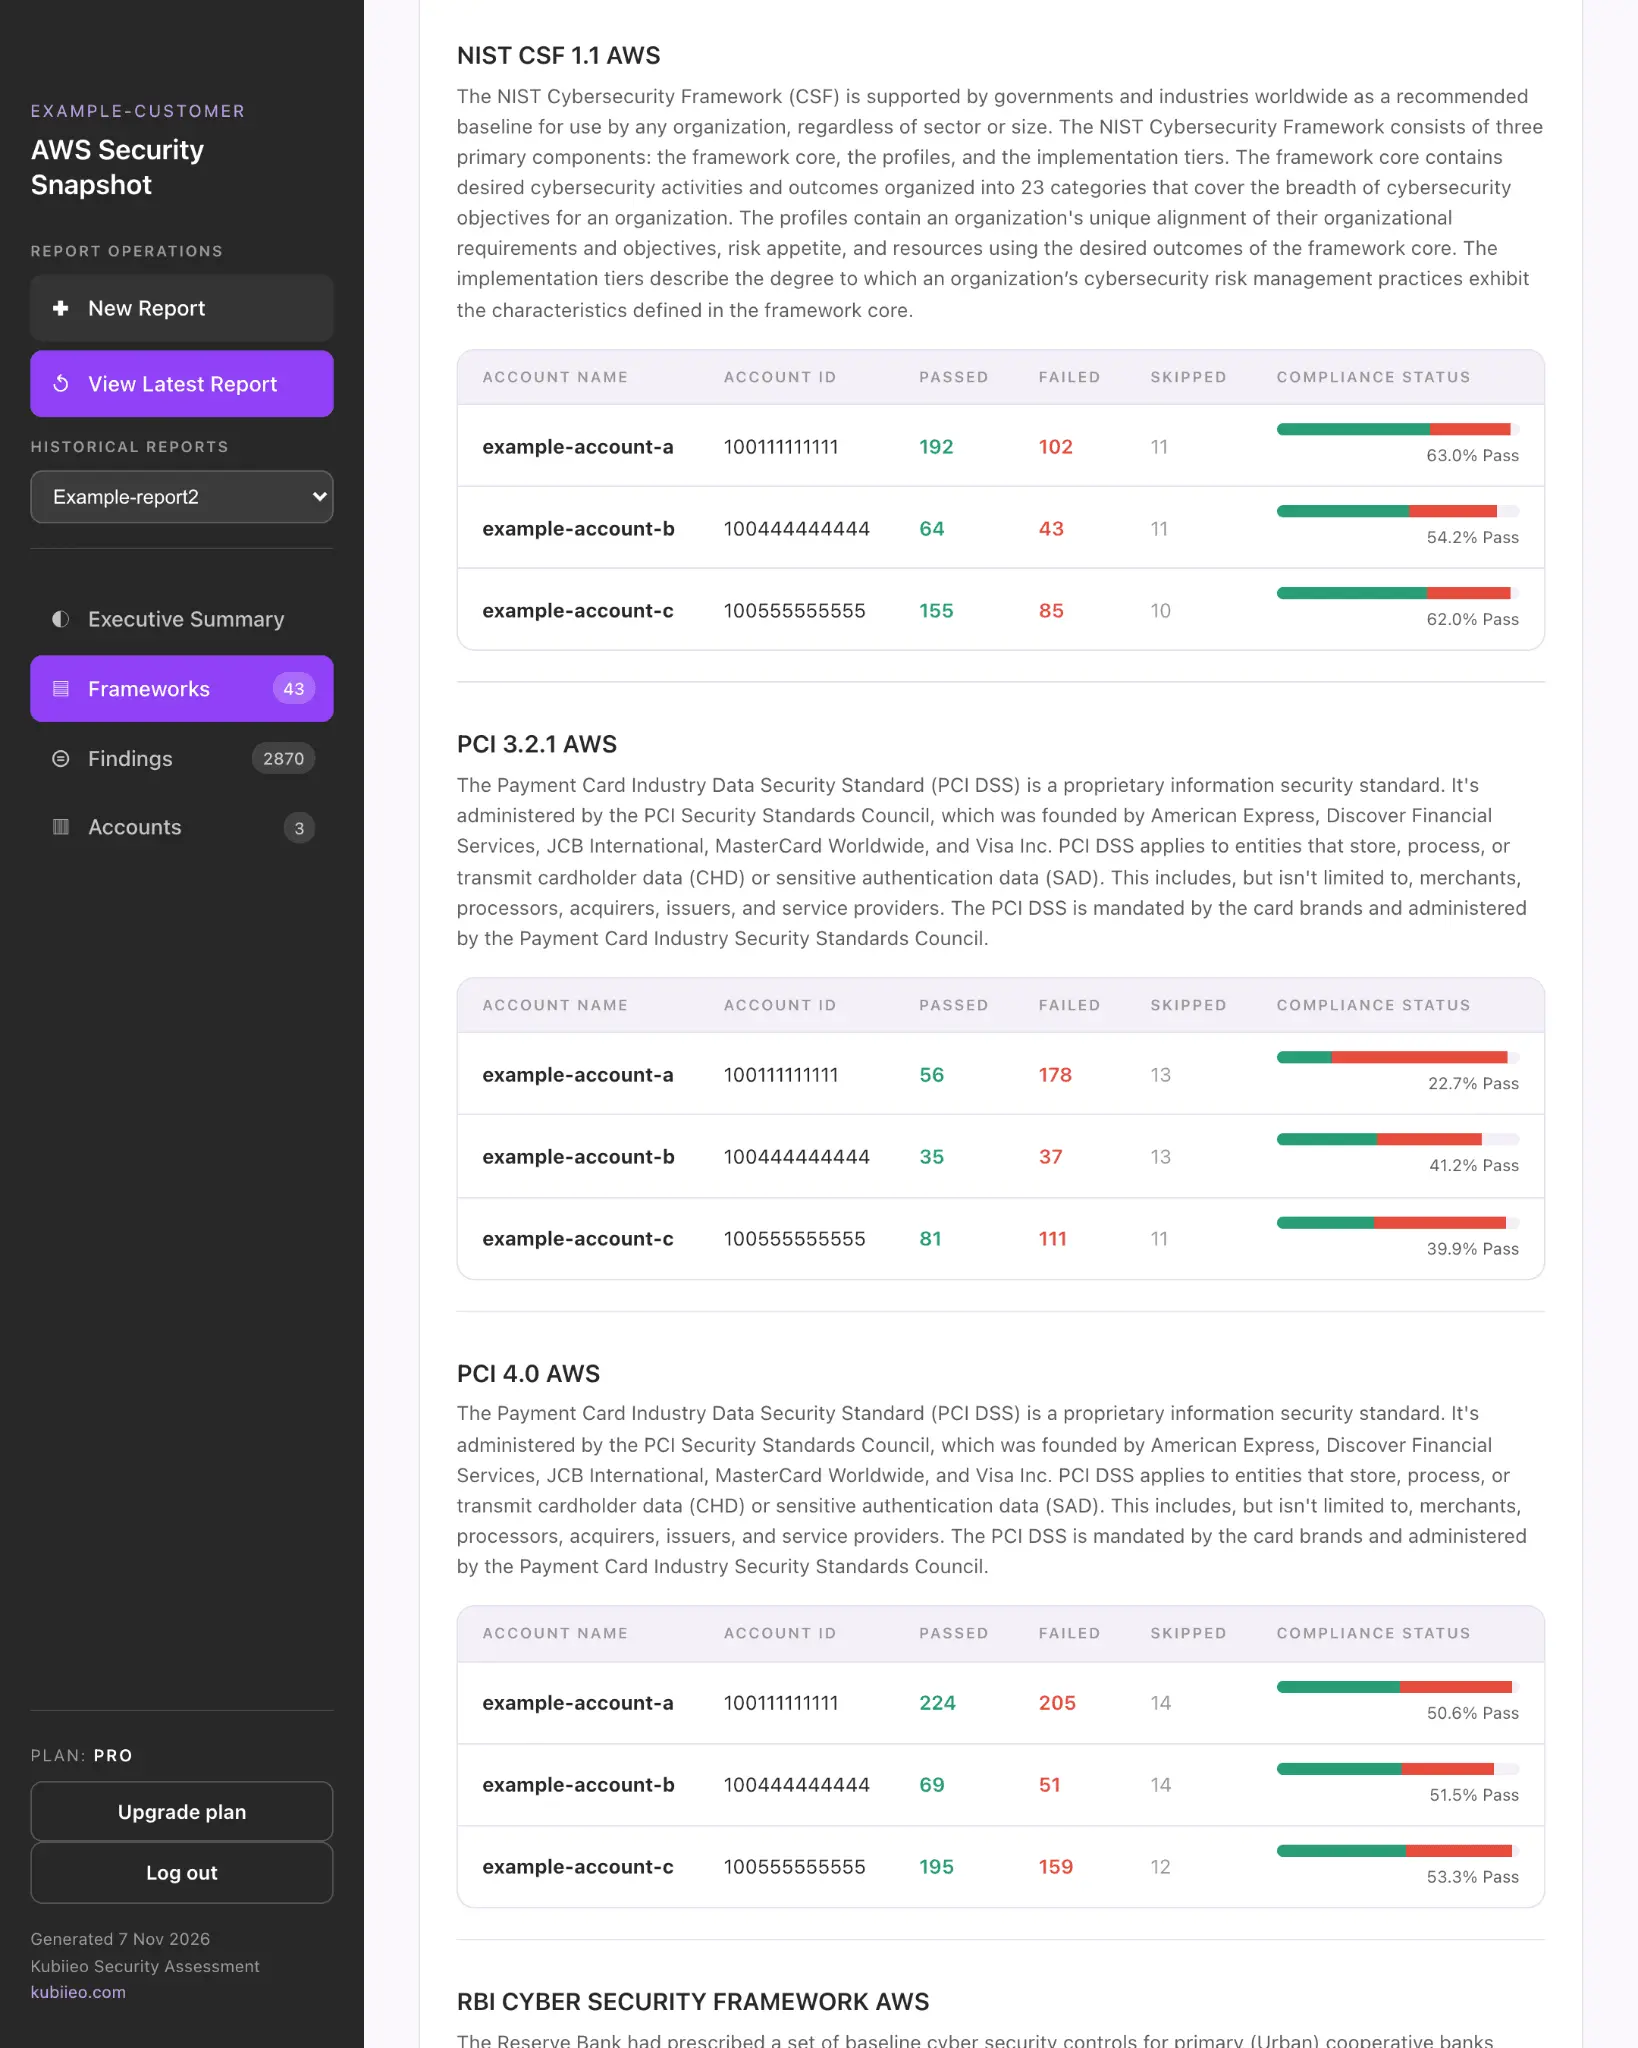
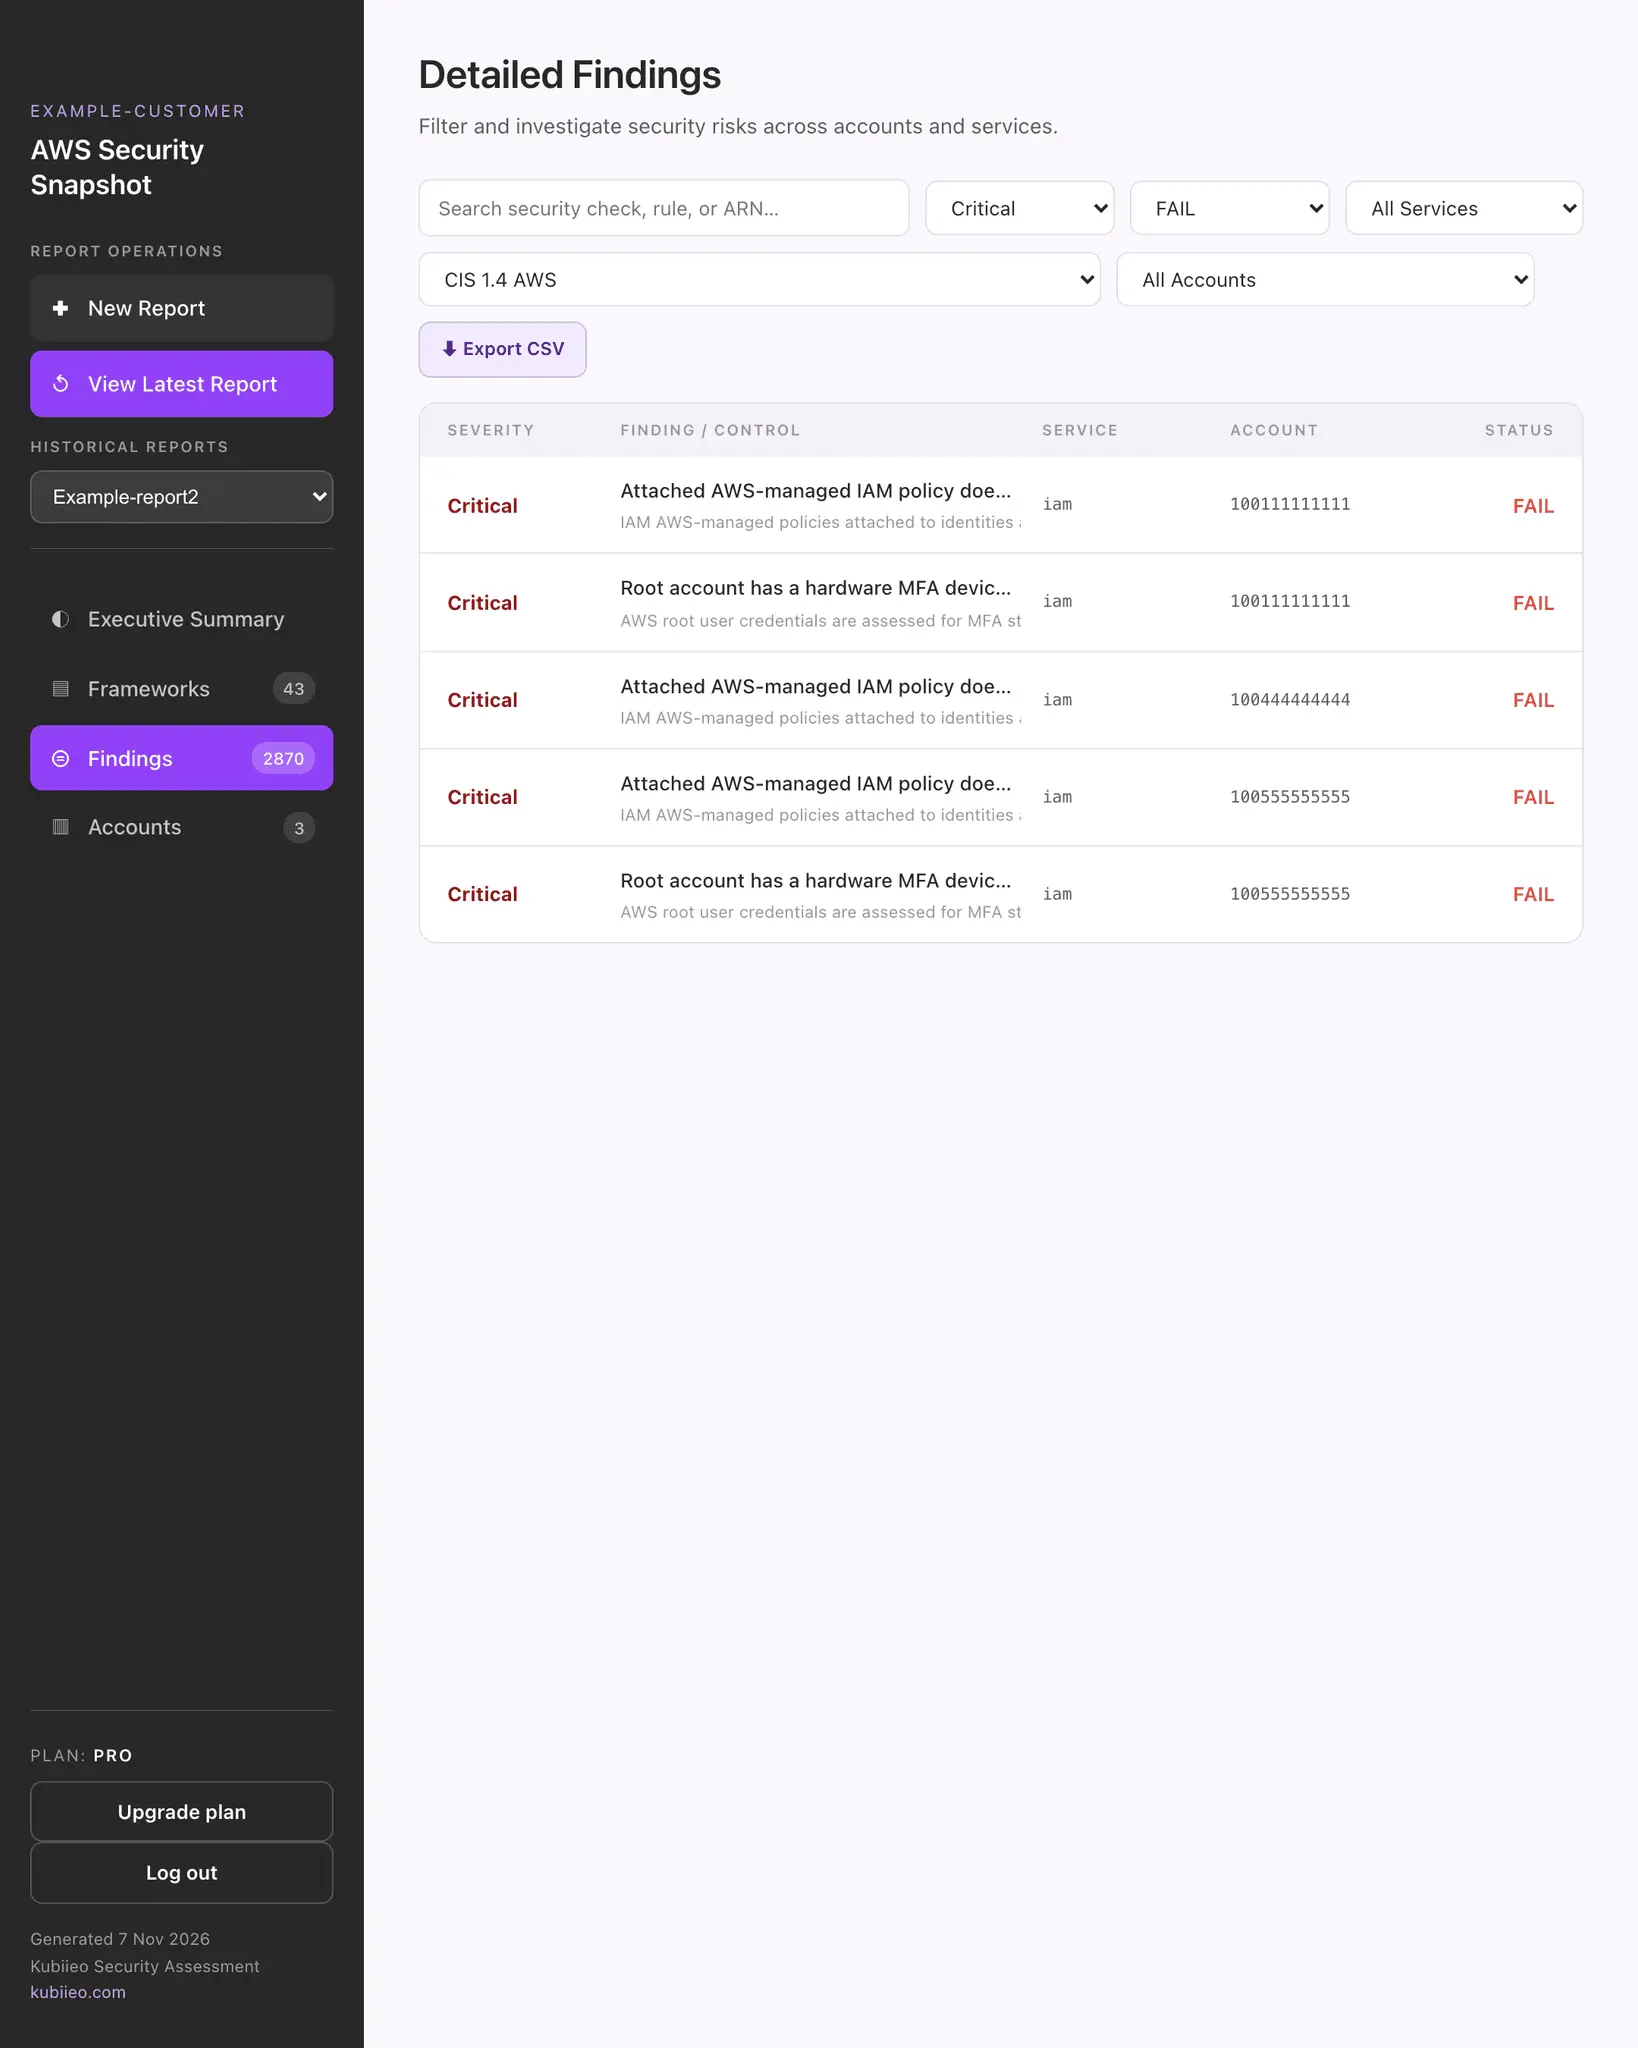
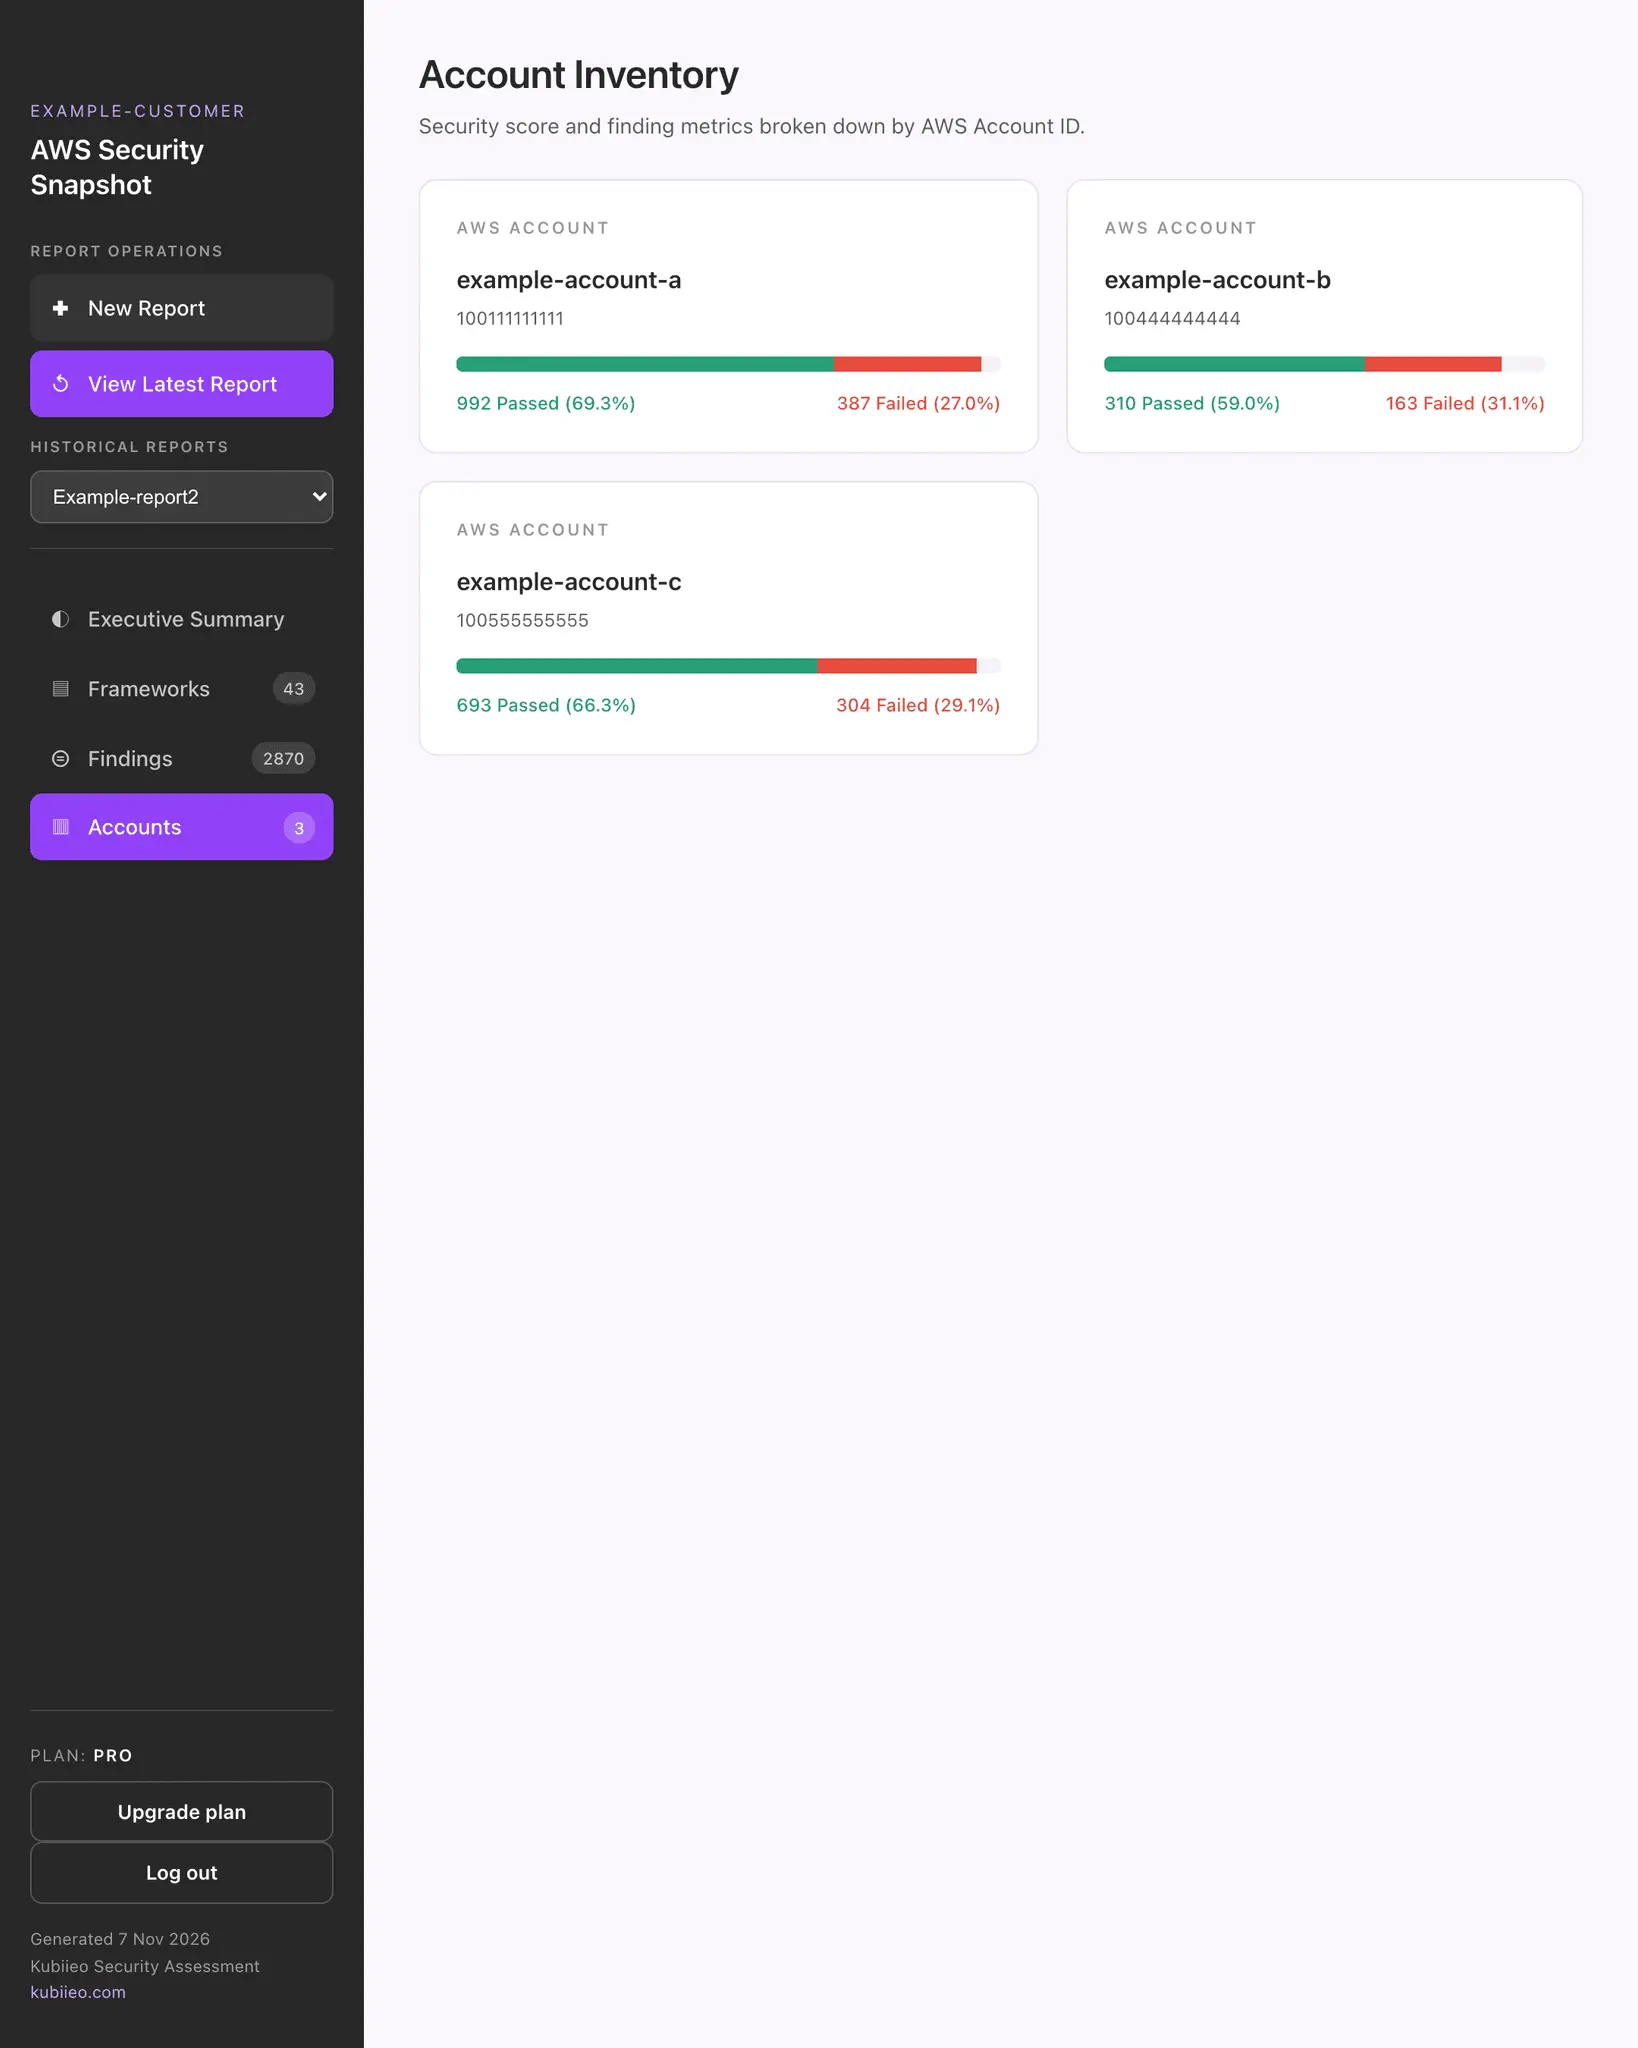
Kubiieo Security Console: AWS security posture checks across all your accounts Most AWS environments have security gaps nobody has looked at in a while: public S3 buckets, root accounts without MFA, overly broad IAM permissions, unencrypted storage, logging that was never switched on. Finding them means checking every account and region against hundreds of best-practice rules. Kubiieo Security Console does that for you and shows you exactly what is failing and where. How it works Sign in with Google or a local account, then connect your AWS environment with your organisation’s existing AWS SSO (IAM Identity Center). Enter your SSO start URL and region, sign in the way you normally do, and the tool lists every account and role you have access to. Pick the ones you want to scan. Read-only roles are all it needs. If you don’t use SSO, you can connect with IAM access keys instead. There’s nothing to install: no agents, no CloudFormation stacks, no cross-account roles to set up. Sessions are temporary and credentials are never stored. Scans run on the open-source Prowler engine, so the checks are ones the AWS security community already knows and trusts. What you get Executive summary: your overall pass rate, checks broken down by severity, and the most common critical and high-severity failures across your environment. Compliance frameworks: see how your accounts measure up against frameworks such as CIS, with pass and fail counts per control. Detailed findings: every check, filterable by severity, status, service, framework and account, and searchable by check name or resource ARN. Finding details: the affected resource, a description of the risk, recommended remediation, and the compliance controls each finding maps to. Per-account view: see which accounts need the most attention. CSV export: take the findings into your own tracking or ticketing tools. Report history: keep earlier scans and compare your posture over time. Who it’s for Security and platform engineers who want a fast baseline across many accounts. Engineering managers and CTOs preparing for audits or customer security questionnaires. Consultants and MSPs assessing client environments. It works for anything from a single AWS account to a large multi-account AWS Organization. Why teams use it Quick to start: connect with the SSO you already have and get a report the same day. Safe: read-only access, temporary sessions, nothing stored. Clear priorities: findings ranked by severity, so you know what to fix first. Whole-organisation view: scan many accounts in one run instead of one at a time. Plans Start free. The free plan shows your full security summary, framework scores and every failing check, so you can see where you stand straight away. Paid plans unlock the details you need to fix things: the affected resources, the accounts they live in, and remediation steps for each finding, along with more report runs per month. About Kubiieo Kubiieo is an Australian cloud consultancy and AWS Advanced Tier Services Partner, working across cloud, DevSecOps and security engineering.
Product Video
Watch a video demo of Kubiieo Security Report.
Screenshots
Reviews (1)
Average 5.0 out of 5
Based on 1 review

The combination of read-only AWS scans, temporary sessions, and no agents to deploy makes this a reassuringly low-friction security baseline. Clear per-account findings and remediation guidance look especially useful for teams.
Comments (2)
The read-only scans across AWS accounts, with temporary sessions and no agents to install, sound like a thoughtful way to get a baseline. Per-account findings and remediation details should make prioritization clearer.
If you find the tool useful and know others who would too, we run an affiliate program, with a link on our welcome page. Feedback and feature requests are very welcome!