Rizzqo
Asset-first compliance execution. Made in Germany.
Details
- Follow on
- Categories
- Use Cases
- Target Audience
- Pricing
- Subscription
- Platforms
- Alternatives
 Drata alternatives
Discovery signals
How AI and people discover Rizzqo on PeerPush
By AI reads among Cybersecurity & Privacy tools
2,127 AI reads in the last 30 days, ranked against every Cybersecurity & Privacy tool listed.About Rizzqo
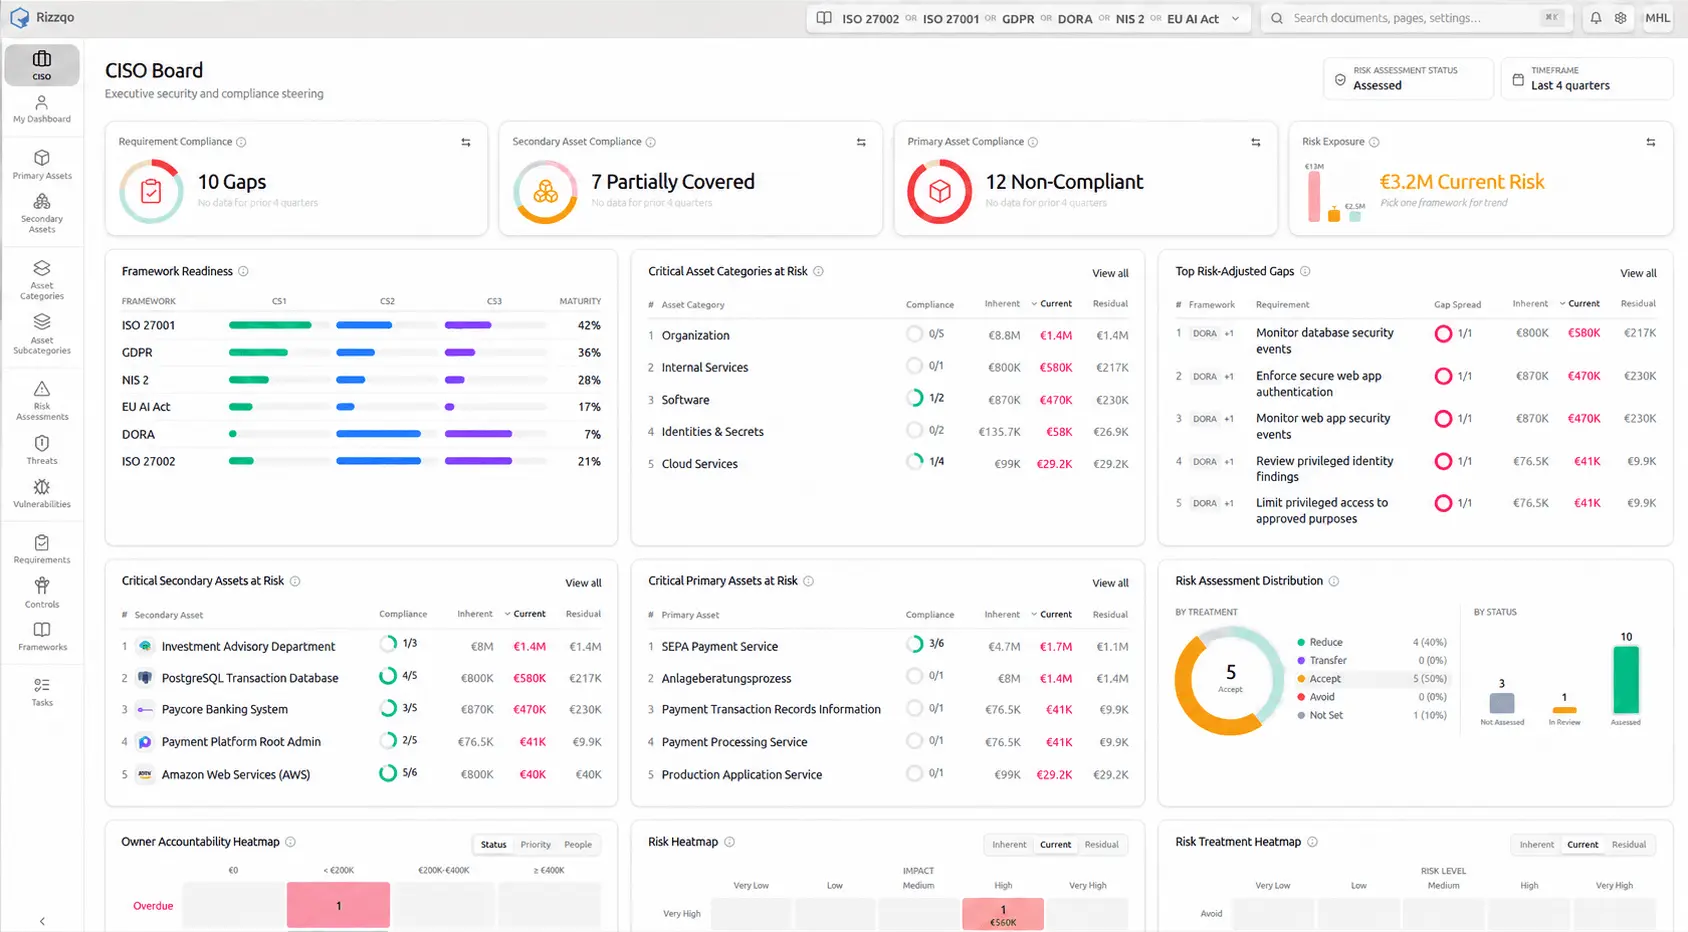
Rizzqo is asset-first compliance execution software for regulated organizations. Most compliance programs are built top-down: frameworks become controls, controls become policies, and the security team is left trying to find out whether those policies are actually implemented anywhere. A policy is not proof of implementation. Rizzqo starts from the organization instead. You model the critical services, information and processes you protect, the applications, systems, infrastructure and suppliers they depend on, and who is responsible for each. Frameworks such as ISO 27001, ISO 27002, NIS2, DORA, GDPR, EU AI Act, CRA, TISAX, ISO 21434, ISO 27017, MVSP, NIST CSF 2.0 and your own rule sets are translated into requirements per asset type. When an asset is added or classified, the requirements that apply to it appear automatically and are assigned to its owner. The owner answers, attaches evidence and confirms with a logged timestamp. Compliance status is calculated from confirmed answers, never self-declared. One requirement can satisfy controls from several frameworks, so work is done once. Open requirements are visible as gaps. Gaps become risk assessments with inherent, current and residual scoring, monetary evaluation and a documented treatment decision. Remediation tasks are assigned, tracked and synchronized with Jira. Dashboards show ISMS teams and CISOs framework readiness and which critical business services are exposed by unfinished work. Suppliers, personal data flows and AI systems are handled in the same asset model. Made in Germany. Deployed on-premises or in a cloud in the customer's own country. SSO and SCIM, audit log, daily backups. Annual subscription per organization, 30-day free trial.
Product Video
Watch a video demo of Rizzqo.
Screenshots
Reviews (2)
Average 5.0 out of 5
Based on 2 reviews

Comments (1)
A policy is not proof. Rizzqo puts every ISO 27001, NIS2 and DORA requirement on the actual asset and the actual owner. Happy to show how.